Stats
- First seen
- January 2022
- Last seen
- November 2026
Description
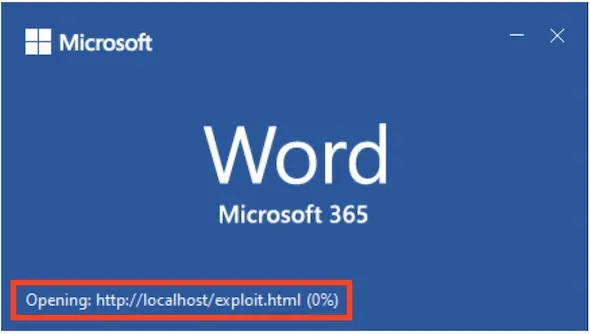
Detects a document exploiting CVE-2021-40444, the Microsoft Office and MSHTML ActiveX bypass that runs a remote ActiveX control without prompting. The rule matches the encoded control identifier that the exploit embeds, and the flaw saw active exploitation before the September 2021 fix.