

Description
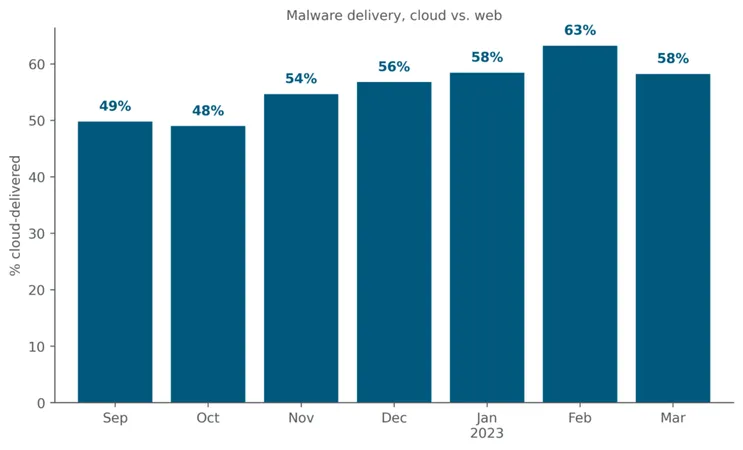
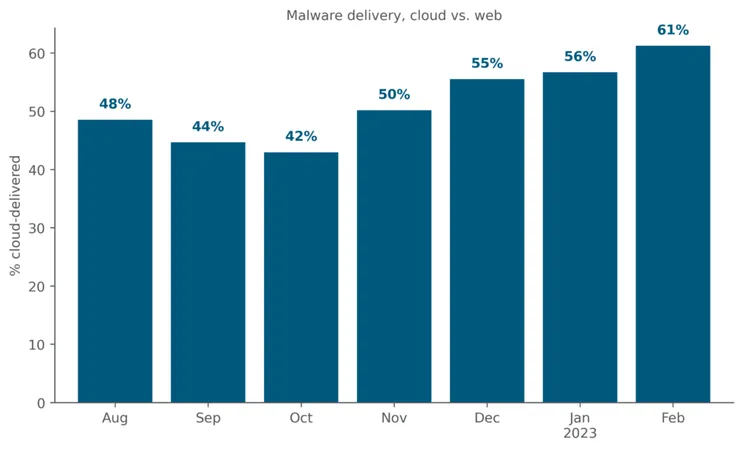
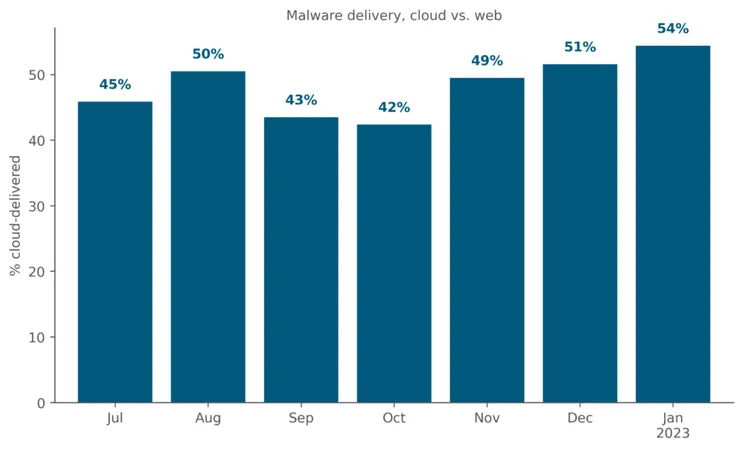
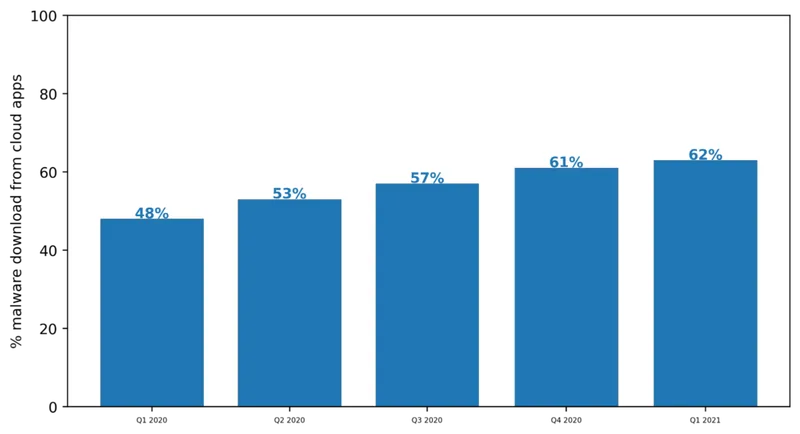
Detects network traffic carrying the Windows portable executable (PE) signature. Executables transferred over the web are a primary malware delivery vector, so identification supports file blocking and inspection policies.
Related blogs
2 SIDs: 25515, 52057
Detects network traffic carrying the Windows portable executable (PE) signature. Executables transferred over the web are a primary malware delivery vector, so identification supports file blocking and inspection policies.