$100k in Crypto Drained by the Underground Operation
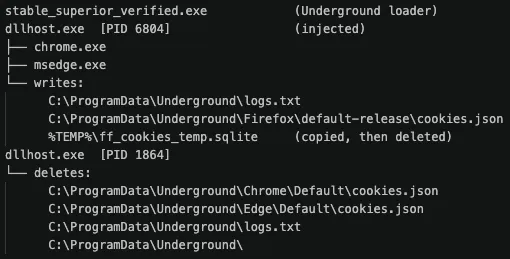
A Vidar-class stealer injected into dllhost.exe takes its commands from rotating Cloudflare-fronted /api/machine gates, automatically drains crypto-exchange accounts, and rewrites the withdrawal confirmation email in the victim's webmail.