Description
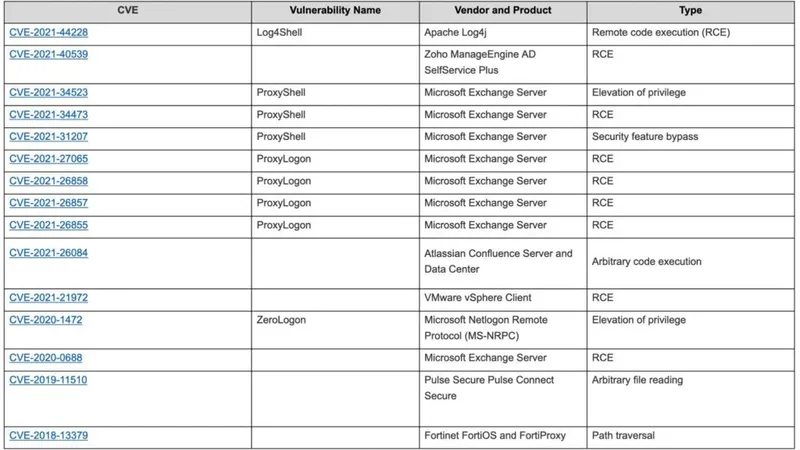
Detects an attempt to exploit CVE-2021-26855, a server-side request forgery flaw that can make the server send requests to internal or external targets in Microsoft Exchange Server. The flaw is part of the ProxyLogon exploit chain that saw mass exploitation of Exchange servers, often followed by webshell deployment, then ransomware.