Description
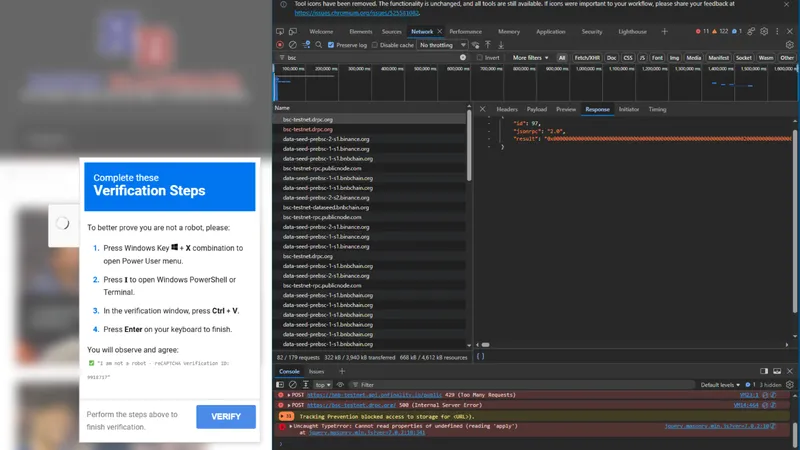
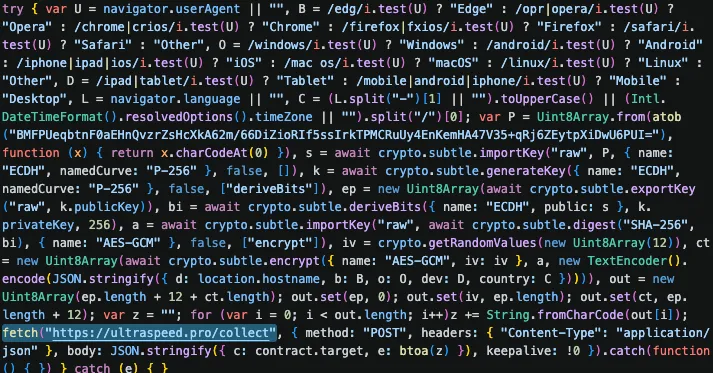
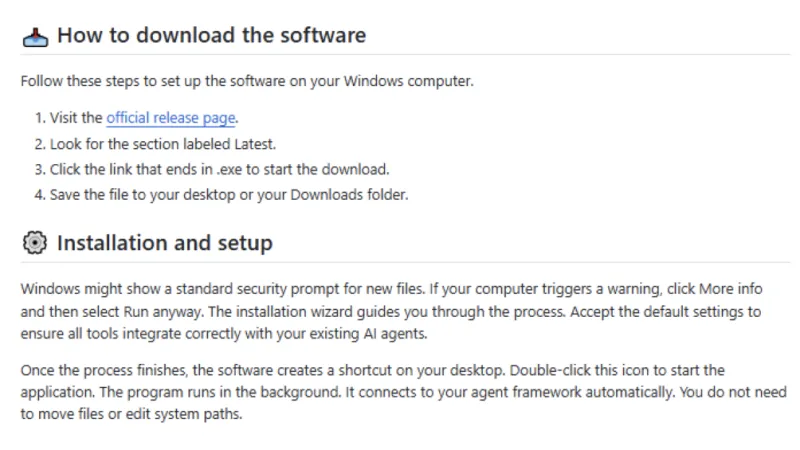
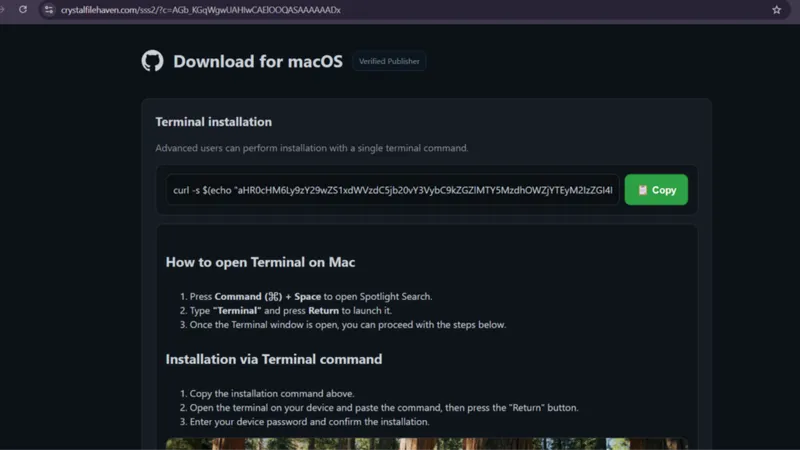
ClickFix is a social engineering technique in which cyberattackers present a fake CAPTCHA, browser update, or error message and instruct users to copy an obfuscated command and paste it into the Windows Run dialog or a terminal. Because users run the command themselves, the attack bypasses email filters, browser sandboxes, and other defenses that block malicious file downloads, and it has become a leading delivery method for infostealers such as Lummastealer and Amatera since late 2024.
Stats
- First seen
- October 2024
- Last seen
- October 2026
Also known as
Clickfix
Alert name variants
| Alert Name | Engine |
|---|---|
| Document-HTML.Malware.ClickFix | ATP Sandbox Adv. Heuristics |
| Document-HTML.Trojan.ClickFix | ATP Sandbox Adv. Heuristics |
| Generic.JS.Clickfix.1.0022DC61 | AV |
| Generic.JS.Clickfix.1.01441D81 | AV |
| Generic.JS.Clickfix.1.0145628D | AV |
| Generic.JS.Clickfix.1.01E8A1DE | AV |
| Generic.JS.Clickfix.1.02FE4744 | AV |
| Generic.JS.Clickfix.1.03023234 | AV |
| Generic.JS.Clickfix.1.03403FF3 | AV |
| Generic.JS.Clickfix.1.0447F4FC | AV |
| Generic.JS.Clickfix.1.048B8FC9 | AV |
| Generic.JS.Clickfix.1.06465E60 | AV |
| Generic.JS.Clickfix.1.066B292D | AV |
| Generic.JS.Clickfix.1.06700AE8 | AV |
| Generic.JS.Clickfix.1.068C959D | AV |
| Generic.JS.Clickfix.1.074235A6 | AV |
| Generic.JS.Clickfix.1.0811E215 | AV |
| Generic.JS.Clickfix.1.0854F0CB | AV |
| Generic.JS.Clickfix.1.08B9D107 | AV |
| Generic.JS.Clickfix.1.08FC83C1 | AV |
| Generic.JS.Clickfix.1.092932EA | AV |
| Generic.JS.Clickfix.1.09684CA3 | AV |
| Generic.JS.Clickfix.1.0BED7FAF | AV |
| Generic.JS.Clickfix.1.0C1CDA5B | AV |
| Generic.JS.Clickfix.1.0C3A21E7 | AV |
| Generic.JS.Clickfix.1.0CB0C83F | AV |
| Generic.JS.Clickfix.1.0CC7F949 | AV |
| Generic.JS.Clickfix.1.0D5F6605 | AV |
| Generic.JS.Clickfix.1.0E963A21 | AV |
| Generic.JS.Clickfix.1.0F6D9AEF | AV |
| Generic.JS.Clickfix.1.0FA5B5F9 | AV |
| Generic.JS.Clickfix.1.0FD5A95F | AV |
| Generic.JS.Clickfix.1.1065BF3B | AV |
| Generic.JS.Clickfix.1.1070234B | AV |
| Generic.JS.Clickfix.1.116F982B | AV |
| Generic.JS.Clickfix.1.126B43BC | AV |
| Generic.JS.Clickfix.1.12EDEBF4 | AV |
| Generic.JS.Clickfix.1.14B1D586 | AV |
| Generic.JS.Clickfix.1.15B28C27 | AV |
| Generic.JS.Clickfix.1.15BAC798 | AV |
| Generic.JS.Clickfix.1.161DD290 | AV |
| Generic.JS.Clickfix.1.17C2A24A | AV |
| Generic.JS.Clickfix.1.17D52754 | AV |
| Generic.JS.Clickfix.1.18339A0A | AV |
| Generic.JS.Clickfix.1.1867FBAF | AV |
| Generic.JS.Clickfix.1.18B17772 | AV |
| Generic.JS.Clickfix.1.198DE759 | AV |
| Generic.JS.Clickfix.1.1998968A | AV |
| Generic.JS.Clickfix.1.1A30189C | AV |
| Generic.JS.Clickfix.1.1AA56C41 | AV |
| Generic.JS.Clickfix.1.1B0CE1FD | AV |
| Generic.JS.Clickfix.1.1C80E190 | AV |
| Generic.JS.Clickfix.1.1CE66E36 | AV |
| Generic.JS.Clickfix.1.1E84CBB9 | AV |
| Generic.JS.Clickfix.1.1F26F722 | AV |
| Generic.JS.Clickfix.1.20D7B2BF | AV |
| Generic.JS.Clickfix.1.2120A727 | AV |
| Generic.JS.Clickfix.1.216250B5 | AV |
| Generic.JS.Clickfix.1.21B5FD88 | AV |
| Generic.JS.Clickfix.1.230DFCC5 | AV |
| Generic.JS.Clickfix.1.232CDE72 | AV |
| Generic.JS.Clickfix.1.2331072C | AV |
| Generic.JS.Clickfix.1.2331BEED | AV |
| Generic.JS.Clickfix.1.2335F9E4 | AV |
| Generic.JS.Clickfix.1.246915BC | AV |
| Generic.JS.Clickfix.1.24757853 | AV |
| Generic.JS.Clickfix.1.2476E0CA | AV |
| Generic.JS.Clickfix.1.24D9EBD7 | AV |
| Generic.JS.Clickfix.1.25282D7A | AV |
| Generic.JS.Clickfix.1.253C672B | AV |
| Generic.JS.Clickfix.1.2564C361 | AV |
| Generic.JS.Clickfix.1.259416A4 | AV |
| Generic.JS.Clickfix.1.25EDC5AB | AV |
| Generic.JS.Clickfix.1.2659D684 | AV |
| Generic.JS.Clickfix.1.266406EA | AV |
| Generic.JS.Clickfix.1.27B15AE8 | AV |
| Generic.JS.Clickfix.1.28966A3C | AV |
| Generic.JS.Clickfix.1.297B38B6 | AV |
| Generic.JS.Clickfix.1.2A975EEA | AV |
| Generic.JS.Clickfix.1.2AEF9BEF | AV |
| Generic.JS.Clickfix.1.2B322349 | AV |
| Generic.JS.Clickfix.1.2BC5DA57 | AV |
| Generic.JS.Clickfix.1.2C031A43 | AV |
| Generic.JS.Clickfix.1.2DFC2366 | AV |
| Generic.JS.Clickfix.1.2E286788 | AV |
| Generic.JS.Clickfix.1.2E6641CC | AV |
| Generic.JS.Clickfix.1.2E9F8EFC | AV |
| Generic.JS.Clickfix.1.2F241FAB | AV |
| Generic.JS.Clickfix.1.2F7F7F5F | AV |
| Generic.JS.Clickfix.1.2FB50F9D | AV |
| Generic.JS.Clickfix.1.30496F3B | AV |
| Generic.JS.Clickfix.1.306411C5 | AV |
| Generic.JS.Clickfix.1.30B21ADC | AV |
| Generic.JS.Clickfix.1.30FFBDFC | AV |
| Generic.JS.Clickfix.1.315D7848 | AV |
| Generic.JS.Clickfix.1.326F9D0E | AV |
| Generic.JS.Clickfix.1.32C2A634 | AV |
| Generic.JS.Clickfix.1.3326E07D | AV |
| Generic.JS.Clickfix.1.334871BE | AV |
| Generic.JS.Clickfix.1.33ACB904 | AV |
| Generic.JS.Clickfix.1.33B42F04 | AV |
| Generic.JS.Clickfix.1.341BEAA7 | AV |
| Generic.JS.Clickfix.1.344D4614 | AV |
| Generic.JS.Clickfix.1.345197E6 | AV |
| Generic.JS.Clickfix.1.348F6DCB | AV |
| Generic.JS.Clickfix.1.3631DD4E | AV |
| Generic.JS.Clickfix.1.369EBF7E | AV |
| Generic.JS.Clickfix.1.379B42AE | AV |
| Generic.JS.Clickfix.1.379C9A1C | AV |
| Generic.JS.Clickfix.1.381373C9 | AV |
| Generic.JS.Clickfix.1.38AECB8A | AV |
| Generic.JS.Clickfix.1.39328DE1 | AV |
| Generic.JS.Clickfix.1.3969A7B6 | AV |
| Generic.JS.Clickfix.1.39B00327 | AV |
| Generic.JS.Clickfix.1.3B84727F | AV |
| Generic.JS.Clickfix.1.3C639D12 | AV |
| Generic.JS.Clickfix.1.3C8E15A3 | AV |
| Generic.JS.Clickfix.1.3CCF07ED | AV |
| Generic.JS.Clickfix.1.3D6D466A | AV |
| Generic.JS.Clickfix.1.3DE503A6 | AV |
| Generic.JS.Clickfix.1.3DF35809 | AV |
| Generic.JS.Clickfix.1.3FACAF29 | AV |
| Generic.JS.Clickfix.1.3FD6D0A5 | AV |
| Generic.JS.Clickfix.1.3FFD9E86 | AV |
| Generic.JS.Clickfix.1.40288F94 | AV |
| Generic.JS.Clickfix.1.41A3CCDA | AV |
| Generic.JS.Clickfix.1.422A15F1 | AV |
| Generic.JS.Clickfix.1.43521072 | AV |
| Generic.JS.Clickfix.1.435670EF | AV |
| Generic.JS.Clickfix.1.43699328 | AV |
| Generic.JS.Clickfix.1.43A502A7 | AV |
| Generic.JS.Clickfix.1.450CF562 | AV |
| Generic.JS.Clickfix.1.457B815A | AV |
| Generic.JS.Clickfix.1.45E6AF0B | AV |
| Generic.JS.Clickfix.1.462DA437 | AV |
| Generic.JS.Clickfix.1.4662D308 | AV |
| Generic.JS.Clickfix.1.467E3838 | AV |
| Generic.JS.Clickfix.1.47445CCB | AV |
| Generic.JS.Clickfix.1.48ACB37E | AV |
| Generic.JS.Clickfix.1.48BB0BD5 | AV |
| Generic.JS.Clickfix.1.48BECE98 | AV |
| Generic.JS.Clickfix.1.49B5A827 | AV |
| Generic.JS.Clickfix.1.49F90147 | AV |
| Generic.JS.Clickfix.1.4A643121 | AV |
| Generic.JS.Clickfix.1.4B533AC7 | AV |
| Generic.JS.Clickfix.1.4BBD969C | AV |
| Generic.JS.Clickfix.1.4BD1B7B5 | AV |
| Generic.JS.Clickfix.1.4C7E6C35 | AV |
| Generic.JS.Clickfix.1.4CDF7583 | AV |
| Generic.JS.Clickfix.1.4CE990B8 | AV |
| Generic.JS.Clickfix.1.4D068774 | AV |
| Generic.JS.Clickfix.1.4D365389 | AV |
| Generic.JS.Clickfix.1.4DCBD531 | AV |
| Generic.JS.Clickfix.1.4E25D1B8 | AV |
| Generic.JS.Clickfix.1.4E78E4FF | AV |
| Generic.JS.Clickfix.1.4EDCAD41 | AV |
| Generic.JS.Clickfix.1.4F5788F1 | AV |
| Generic.JS.Clickfix.1.4F9DA12D | AV |
| Generic.JS.Clickfix.1.511981CA | AV |
| Generic.JS.Clickfix.1.51A2AE4C | AV |
| Generic.JS.Clickfix.1.5234B75F | AV |
| Generic.JS.Clickfix.1.5256430A | AV |
| Generic.JS.Clickfix.1.52ADA74D | AV |
| Generic.JS.Clickfix.1.53706FF5 | AV |
| Generic.JS.Clickfix.1.53F80381 | AV |
| Generic.JS.Clickfix.1.5444AC16 | AV |
| Generic.JS.Clickfix.1.5489E588 | AV |
| Generic.JS.Clickfix.1.549B0828 | AV |
| Generic.JS.Clickfix.1.54A7A7AB | AV |
| Generic.JS.Clickfix.1.5662FB8A | AV |
| Generic.JS.Clickfix.1.578A173B | AV |
| Generic.JS.Clickfix.1.57DFEB93 | AV |
| Generic.JS.Clickfix.1.583BA591 | AV |
| Generic.JS.Clickfix.1.58AE406D | AV |
| Generic.JS.Clickfix.1.58EA4DA4 | AV |
| Generic.JS.Clickfix.1.59DDE0F3 | AV |
| Generic.JS.Clickfix.1.5A26CF7E | AV |
| Generic.JS.Clickfix.1.5AD71660 | AV |
| Generic.JS.Clickfix.1.5B0A99D3 | AV |
| Generic.JS.Clickfix.1.5D24B87F | AV |
| Generic.JS.Clickfix.1.5D71F72E | AV |
| Generic.JS.Clickfix.1.5E363A11 | AV |
| Generic.JS.Clickfix.1.5E666213 | AV |
| Generic.JS.Clickfix.1.5E80A10C | AV |
| Generic.JS.Clickfix.1.5EEB5BD0 | AV |
| Generic.JS.Clickfix.1.5F5B4C1C | AV |
| Generic.JS.Clickfix.1.6129C181 | AV |
| Generic.JS.Clickfix.1.612AE506 | AV |
| Generic.JS.Clickfix.1.613CD4E7 | AV |
| Generic.JS.Clickfix.1.614232C8 | AV |
| Generic.JS.Clickfix.1.6196ED5F | AV |
| Generic.JS.Clickfix.1.61A30165 | AV |
| Generic.JS.Clickfix.1.62A9D988 | AV |
| Generic.JS.Clickfix.1.62D382B5 | AV |
| Generic.JS.Clickfix.1.63544EAB | AV |
| Generic.JS.Clickfix.1.636EB656 | AV |
| Generic.JS.Clickfix.1.640829C0 | AV |
| Generic.JS.Clickfix.1.6422C811 | AV |
| Generic.JS.Clickfix.1.644F3583 | AV |
| Generic.JS.Clickfix.1.64800814 | AV |
| Generic.JS.Clickfix.1.648C75A4 | AV |
| Generic.JS.Clickfix.1.649F0746 | AV |
| Generic.JS.Clickfix.1.64C12CC1 | AV |
| Generic.JS.Clickfix.1.651155F8 | AV |
| Generic.JS.Clickfix.1.66115B87 | AV |
| Generic.JS.Clickfix.1.66B4ADF7 | AV |
| Generic.JS.Clickfix.1.66F0887A | AV |
| Generic.JS.Clickfix.1.674B53EB | AV |
| Generic.JS.Clickfix.1.676B82E5 | AV |
| Generic.JS.Clickfix.1.68012082 | AV |
| Generic.JS.Clickfix.1.689A897F | AV |
| Generic.JS.Clickfix.1.69D65C3D | AV |
| Generic.JS.Clickfix.1.6A6E75EC | AV |
| Generic.JS.Clickfix.1.6B972EC5 | AV |
| Generic.JS.Clickfix.1.6BD2D5BC | AV |
| Generic.JS.Clickfix.1.6BF9F08A | AV |
| Generic.JS.Clickfix.1.6CB22E4C | AV |
| Generic.JS.Clickfix.1.6CDC06A7 | AV |
| Generic.JS.Clickfix.1.6CFA145C | AV |
| Generic.JS.Clickfix.1.6D103365 | AV |
| Generic.JS.Clickfix.1.6D11E964 | AV |
| Generic.JS.Clickfix.1.6EC3F1A1 | AV |
| Generic.JS.Clickfix.1.6F0282C2 | AV |
| Generic.JS.Clickfix.1.6F756574 | AV |
| Generic.JS.Clickfix.1.700DCE9C | AV |
| Generic.JS.Clickfix.1.70117C90 | AV |
| Generic.JS.Clickfix.1.705386F6 | AV |
| Generic.JS.Clickfix.1.718A963A | AV |
| Generic.JS.Clickfix.1.71D337CA | AV |
| Generic.JS.Clickfix.1.729492A0 | AV |
| Generic.JS.Clickfix.1.73728A50 | AV |
| Generic.JS.Clickfix.1.738D2EEA | AV |
| Generic.JS.Clickfix.1.739F2660 | AV |
| Generic.JS.Clickfix.1.73AC9A9F | AV |
| Generic.JS.Clickfix.1.73F1AC0F | AV |
| Generic.JS.Clickfix.1.74B03A41 | AV |
| Generic.JS.Clickfix.1.751735E5 | AV |
| Generic.JS.Clickfix.1.755B748B | AV |
| Generic.JS.Clickfix.1.75E442A9 | AV |
| Generic.JS.Clickfix.1.75FE37C2 | AV |
| Generic.JS.Clickfix.1.76D3CB9C | AV |
| Generic.JS.Clickfix.1.7795F0A0 | AV |
| Generic.JS.Clickfix.1.78078F5C | AV |
| Generic.JS.Clickfix.1.791B0C35 | AV |
| Generic.JS.Clickfix.1.7A2D1D45 | AV |
| Generic.JS.Clickfix.1.7B2E249C | AV |
| Generic.JS.Clickfix.1.7C3E782C | AV |
| Generic.JS.Clickfix.1.7C54620F | AV |
| Generic.JS.Clickfix.1.7D29BDB7 | AV |
| Generic.JS.Clickfix.1.7E1A01EF | AV |
| Generic.JS.Clickfix.1.7E2461CC | AV |
| Generic.JS.Clickfix.1.7E34EFBF | AV |
| Generic.JS.Clickfix.1.7E88480E | AV |
| Generic.JS.Clickfix.1.7FA3FFC2 | AV |
| Generic.JS.Clickfix.1.80231ABD | AV |
| Generic.JS.Clickfix.1.80E1CDBF | AV |
| Generic.JS.Clickfix.1.810A763C | AV |
| Generic.JS.Clickfix.1.814E3EBF | AV |
| Generic.JS.Clickfix.1.81AD4475 | AV |
| Generic.JS.Clickfix.1.81B3DFB3 | AV |
| Generic.JS.Clickfix.1.825CFBA1 | AV |
| Generic.JS.Clickfix.1.830FCAC6 | AV |
| Generic.JS.Clickfix.1.83C3E21C | AV |
| Generic.JS.Clickfix.1.84412157 | AV |
| Generic.JS.Clickfix.1.84453463 | AV |
| Generic.JS.Clickfix.1.847DCBF2 | AV |
| Generic.JS.Clickfix.1.848704EE | AV |
| Generic.JS.Clickfix.1.84DB10F2 | AV |
| Generic.JS.Clickfix.1.85B555C2 | AV |
| Generic.JS.Clickfix.1.86F45B86 | AV |
| Generic.JS.Clickfix.1.883919CD | AV |
| Generic.JS.Clickfix.1.88F65895 | AV |
| Generic.JS.Clickfix.1.89854E86 | AV |
| Generic.JS.Clickfix.1.8993662E | AV |
| Generic.JS.Clickfix.1.89F8D57E | AV |
| Generic.JS.Clickfix.1.8BB58580 | AV |
| Generic.JS.Clickfix.1.8C039D66 | AV |
| Generic.JS.Clickfix.1.8C64D594 | AV |
| Generic.JS.Clickfix.1.8C814BA1 | AV |
| Generic.JS.Clickfix.1.8D20B3C8 | AV |
| Generic.JS.Clickfix.1.8D5382E2 | AV |
| Generic.JS.Clickfix.1.8D656668 | AV |
| Generic.JS.Clickfix.1.8D9A9ACD | AV |
| Generic.JS.Clickfix.1.8DE213D1 | AV |
| Generic.JS.Clickfix.1.8E7812EC | AV |
| Generic.JS.Clickfix.1.8E7A6CE5 | AV |
| Generic.JS.Clickfix.1.8F5EEC29 | AV |
| Generic.JS.Clickfix.1.9011FFD1 | AV |
| Generic.JS.Clickfix.1.903994AE | AV |
| Generic.JS.Clickfix.1.90727F76 | AV |
| Generic.JS.Clickfix.1.9098C205 | AV |
| Generic.JS.Clickfix.1.912A0D63 | AV |
| Generic.JS.Clickfix.1.91710D73 | AV |
| Generic.JS.Clickfix.1.92377F8D | AV |
| Generic.JS.Clickfix.1.9386EDD4 | AV |
| Generic.JS.Clickfix.1.94A1BB4C | AV |
| Generic.JS.Clickfix.1.9552F62E | AV |
| Generic.JS.Clickfix.1.9555B054 | AV |
| Generic.JS.Clickfix.1.95DF6A43 | AV |
| Generic.JS.Clickfix.1.96AECF7E | AV |
| Generic.JS.Clickfix.1.97176FD2 | AV |
| Generic.JS.Clickfix.1.97594640 | AV |
| Generic.JS.Clickfix.1.9792E2EB | AV |
| Generic.JS.Clickfix.1.97F963CC | AV |
| Generic.JS.Clickfix.1.9859CE78 | AV |
| Generic.JS.Clickfix.1.98C98383 | AV |
| Generic.JS.Clickfix.1.99269BBA | AV |
| Generic.JS.Clickfix.1.994F8FF8 | AV |
| Generic.JS.Clickfix.1.99AAFCA3 | AV |
| Generic.JS.Clickfix.1.9A4433EE | AV |
| Generic.JS.Clickfix.1.9A636B8A | AV |
| Generic.JS.Clickfix.1.9AEB3C14 | AV |
| Generic.JS.Clickfix.1.9BAE755C | AV |
| Generic.JS.Clickfix.1.9C4C8CAE | AV |
| Generic.JS.Clickfix.1.9C7A9D5B | AV |
| Generic.JS.Clickfix.1.9D9F0A22 | AV |
| Generic.JS.Clickfix.1.9E688E3F | AV |
| Generic.JS.Clickfix.1.9EAD8FE9 | AV |
| Generic.JS.Clickfix.1.9EAF5858 | AV |
| Generic.JS.Clickfix.1.9F3B711A | AV |
| Generic.JS.Clickfix.1.9F87E854 | AV |
| Generic.JS.Clickfix.1.A0956DC1 | AV |
| Generic.JS.Clickfix.1.A1F4E0C4 | AV |
| Generic.JS.Clickfix.1.A304FA71 | AV |
| Generic.JS.Clickfix.1.A30D6BE5 | AV |
| Generic.JS.Clickfix.1.A38695CB | AV |
| Generic.JS.Clickfix.1.A3E7BF1C | AV |
| Generic.JS.Clickfix.1.A3EC31C0 | AV |
| Generic.JS.Clickfix.1.A41A7A4D | AV |
| Generic.JS.Clickfix.1.A468C365 | AV |
| Generic.JS.Clickfix.1.A545B972 | AV |
| Generic.JS.Clickfix.1.A5A862D4 | AV |
| Generic.JS.Clickfix.1.A634BA09 | AV |
| Generic.JS.Clickfix.1.A7B55C30 | AV |
| Generic.JS.Clickfix.1.A9956979 | AV |
| Generic.JS.Clickfix.1.AA21EAFF | AV |
| Generic.JS.Clickfix.1.AAD907B4 | AV |
| Generic.JS.Clickfix.1.AB0FFC2D | AV |
| Generic.JS.Clickfix.1.AB37B4C5 | AV |
| Generic.JS.Clickfix.1.ABB12CA3 | AV |
| Generic.JS.Clickfix.1.ABCCF06B | AV |
| Generic.JS.Clickfix.1.ABCD1146 | AV |
| Generic.JS.Clickfix.1.AC5666B2 | AV |
| Generic.JS.Clickfix.1.ACA0B426 | AV |
| Generic.JS.Clickfix.1.ACA69257 | AV |
| Generic.JS.Clickfix.1.AE9C830B | AV |
| Generic.JS.Clickfix.1.AED5233D | AV |
| Generic.JS.Clickfix.1.AEF0C339 | AV |
| Generic.JS.Clickfix.1.AFB8FE34 | AV |
| Generic.JS.Clickfix.1.AFEE551B | AV |
| Generic.JS.Clickfix.1.B046D0A2 | AV |
| Generic.JS.Clickfix.1.B0ABFEDD | AV |
| Generic.JS.Clickfix.1.B143D8FB | AV |
| Generic.JS.Clickfix.1.B2633585 | AV |
| Generic.JS.Clickfix.1.B34E750E | AV |
| Generic.JS.Clickfix.1.B3F3C53F | AV |
| Generic.JS.Clickfix.1.B4778AFC | AV |
| Generic.JS.Clickfix.1.B5869ED6 | AV |
| Generic.JS.Clickfix.1.B5A2E618 | AV |
| Generic.JS.Clickfix.1.B78EAC87 | AV |
| Generic.JS.Clickfix.1.B7AECFFB | AV |
| Generic.JS.Clickfix.1.B83845E2 | AV |
| Generic.JS.Clickfix.1.B8921984 | AV |
| Generic.JS.Clickfix.1.B8DDEF9B | AV |
| Generic.JS.Clickfix.1.B8F13177 | AV |
| Generic.JS.Clickfix.1.B8F56F82 | AV |
| Generic.JS.Clickfix.1.B90DFE1E | AV |
| Generic.JS.Clickfix.1.B98A1F70 | AV |
| Generic.JS.Clickfix.1.BAA0CA18 | AV |
| Generic.JS.Clickfix.1.BBB0ABB7 | AV |
| Generic.JS.Clickfix.1.BBBB3EF3 | AV |
| Generic.JS.Clickfix.1.BBC6C478 | AV |
| Generic.JS.Clickfix.1.BBCDA639 | AV |
| Generic.JS.Clickfix.1.BC60D36A | AV |
| Generic.JS.Clickfix.1.BCFD5AD1 | AV |
| Generic.JS.Clickfix.1.BE2F9872 | AV |
| Generic.JS.Clickfix.1.BF72147F | AV |
| Generic.JS.Clickfix.1.C0578451 | AV |
| Generic.JS.Clickfix.1.C063FAA0 | AV |
| Generic.JS.Clickfix.1.C094EF6E | AV |
| Generic.JS.Clickfix.1.C0CB12C7 | AV |
| Generic.JS.Clickfix.1.C1A740E7 | AV |
| Generic.JS.Clickfix.1.C2BF2617 | AV |
| Generic.JS.Clickfix.1.C2EA7D90 | AV |
| Generic.JS.Clickfix.1.C3E7EFEE | AV |
| Generic.JS.Clickfix.1.C465019E | AV |
| Generic.JS.Clickfix.1.C4B7BD1E | AV |
| Generic.JS.Clickfix.1.C562E07E | AV |
| Generic.JS.Clickfix.1.C63FD82C | AV |
| Generic.JS.Clickfix.1.C68AC622 | AV |
| Generic.JS.Clickfix.1.C6B1A375 | AV |
| Generic.JS.Clickfix.1.C6EB2D0E | AV |
| Generic.JS.Clickfix.1.C736A65D | AV |
| Generic.JS.Clickfix.1.C7417AAA | AV |
| Generic.JS.Clickfix.1.C7B07DFE | AV |
| Generic.JS.Clickfix.1.C97CE2A0 | AV |
| Generic.JS.Clickfix.1.C9E45819 | AV |
| Generic.JS.Clickfix.1.CC697DFB | AV |
| Generic.JS.Clickfix.1.CD7CBAA4 | AV |
| Generic.JS.Clickfix.1.CE07C2AD | AV |
| Generic.JS.Clickfix.1.CE2F94FA | AV |
| Generic.JS.Clickfix.1.CE59D948 | AV |
| Generic.JS.Clickfix.1.CEE0D95D | AV |
| Generic.JS.Clickfix.1.CF02B7E0 | AV |
| Generic.JS.Clickfix.1.CF96D7D4 | AV |
| Generic.JS.Clickfix.1.CFA4E685 | AV |
| Generic.JS.Clickfix.1.CFFFFBF7 | AV |
| Generic.JS.Clickfix.1.D18E4F22 | AV |
| Generic.JS.Clickfix.1.D4772853 | AV |
| Generic.JS.Clickfix.1.D63E6079 | AV |
| Generic.JS.Clickfix.1.D6E54D4A | AV |
| Generic.JS.Clickfix.1.D6FA48FE | AV |
| Generic.JS.Clickfix.1.D76A06C0 | AV |
| Generic.JS.Clickfix.1.D7C45A19 | AV |
| Generic.JS.Clickfix.1.D7D044C7 | AV |
| Generic.JS.Clickfix.1.D7DAC550 | AV |
| Generic.JS.Clickfix.1.D9268733 | AV |
| Generic.JS.Clickfix.1.D9CE0F3C | AV |
| Generic.JS.Clickfix.1.DA73EAD2 | AV |
| Generic.JS.Clickfix.1.DAF4B8FF | AV |
| Generic.JS.Clickfix.1.DB60542C | AV |
| Generic.JS.Clickfix.1.DC326300 | AV |
| Generic.JS.Clickfix.1.DC50062E | AV |
| Generic.JS.Clickfix.1.DCC2A666 | AV |
| Generic.JS.Clickfix.1.DD70E3AF | AV |
| Generic.JS.Clickfix.1.DD94B109 | AV |
| Generic.JS.Clickfix.1.DDE91B4D | AV |
| Generic.JS.Clickfix.1.DF4AE06E | AV |
| Generic.JS.Clickfix.1.E0FF0932 | AV |
| Generic.JS.Clickfix.1.E1ABEDE9 | AV |
| Generic.JS.Clickfix.1.E1E78C23 | AV |
| Generic.JS.Clickfix.1.E2A3AA91 | AV |
| Generic.JS.Clickfix.1.E2B1E683 | AV |
| Generic.JS.Clickfix.1.E3281893 | AV |
| Generic.JS.Clickfix.1.E3B6313A | AV |
| Generic.JS.Clickfix.1.E45A083D | AV |
| Generic.JS.Clickfix.1.E464B1B7 | AV |
| Generic.JS.Clickfix.1.E4F602C6 | AV |
| Generic.JS.Clickfix.1.E5119EC4 | AV |
| Generic.JS.Clickfix.1.E6637BF9 | AV |
| Generic.JS.Clickfix.1.E689A9F0 | AV |
| Generic.JS.Clickfix.1.E6C543D5 | AV |
| Generic.JS.Clickfix.1.E7009481 | AV |
| Generic.JS.Clickfix.1.E74DFC67 | AV |
| Generic.JS.Clickfix.1.E7D84F5A | AV |
| Generic.JS.Clickfix.1.E832E823 | AV |
| Generic.JS.Clickfix.1.E894046D | AV |
| Generic.JS.Clickfix.1.E929002F | AV |
| Generic.JS.Clickfix.1.E9C0254A | AV |
| Generic.JS.Clickfix.1.E9CED455 | AV |
| Generic.JS.Clickfix.1.EAAE0DA8 | AV |
| Generic.JS.Clickfix.1.EB4F5A55 | AV |
| Generic.JS.Clickfix.1.EC105B94 | AV |
| Generic.JS.Clickfix.1.EC2954F2 | AV |
| Generic.JS.Clickfix.1.EC749C16 | AV |
| Generic.JS.Clickfix.1.ECE5AA1D | AV |
| Generic.JS.Clickfix.1.ECFEC822 | AV |
| Generic.JS.Clickfix.1.EEC6B194 | AV |
| Generic.JS.Clickfix.1.EF034F61 | AV |
| Generic.JS.Clickfix.1.EF396BE1 | AV |
| Generic.JS.Clickfix.1.EF550791 | AV |
| Generic.JS.Clickfix.1.EFB8640F | AV |
| Generic.JS.Clickfix.1.EFFA5AF6 | AV |
| Generic.JS.Clickfix.1.F0129513 | AV |
| Generic.JS.Clickfix.1.F0A5E4D8 | AV |
| Generic.JS.Clickfix.1.F1122CE0 | AV |
| Generic.JS.Clickfix.1.F1574F02 | AV |
| Generic.JS.Clickfix.1.F1D7EA35 | AV |
| Generic.JS.Clickfix.1.F3819042 | AV |
| Generic.JS.Clickfix.1.F435C813 | AV |
| Generic.JS.Clickfix.1.F46C1328 | AV |
| Generic.JS.Clickfix.1.F4E48EA7 | AV |
| Generic.JS.Clickfix.1.F4E833B4 | AV |
| Generic.JS.Clickfix.1.F7CA5564 | AV |
| Generic.JS.Clickfix.1.F7D54934 | AV |
| Generic.JS.Clickfix.1.F807DBD6 | AV |
| Generic.JS.Clickfix.1.F8482BFA | AV |
| Generic.JS.Clickfix.1.F8A5CC58 | AV |
| Generic.JS.Clickfix.1.F9042401 | AV |
| Generic.JS.Clickfix.1.F9F331A8 | AV |
| Generic.JS.Clickfix.1.FA5BF7F0 | AV |
| Generic.JS.Clickfix.1.FA761FB1 | AV |
| Generic.JS.Clickfix.1.FAD23061 | AV |
| Generic.JS.Clickfix.1.FAEE8AFD | AV |
| Generic.JS.Clickfix.1.FB362931 | AV |
| Generic.JS.Clickfix.1.FC1B1B2E | AV |
| Generic.JS.Clickfix.1.FC82A6C9 | AV |
| Generic.JS.Clickfix.1.FDAAB6FA | AV |
| Generic.JS.Clickfix.1.FE84A29F | AV |
| Generic.JS.Clickfix.1.FEC228C2 | AV |
| Generic.JS.Clickfix.1.FEE05954 | AV |
| Generic.JS.Clickfix.1.FFFFC645 | AV |
| Image.Trojan.ClickFix | ATP Sandbox Adv. Heuristics |
| Script-JS.Malware.Clickfix | ATP Sandbox Adv. Heuristics |
| Script-JS.Trojan.Clickfix | ATP Sandbox Adv. Heuristics |
| Script-JS.Trojan.ClickFix | ATP Sandbox Adv. Heuristics |
| Script-PowerShell.Trojan.Clickfix | ATP Sandbox Adv. Heuristics |
| Shortcut.Trojan.ClickFix | ATP Sandbox Adv. Heuristics |
| Trojan.ClickFix.2 | AV |
| Win32.Trojan.ClickFix | ATP Sandbox Adv. Heuristics |
| Win64.Trojan.Clickfix | ATP Sandbox Adv. Heuristics |
Related IPS Signatures
Related blogs