Description
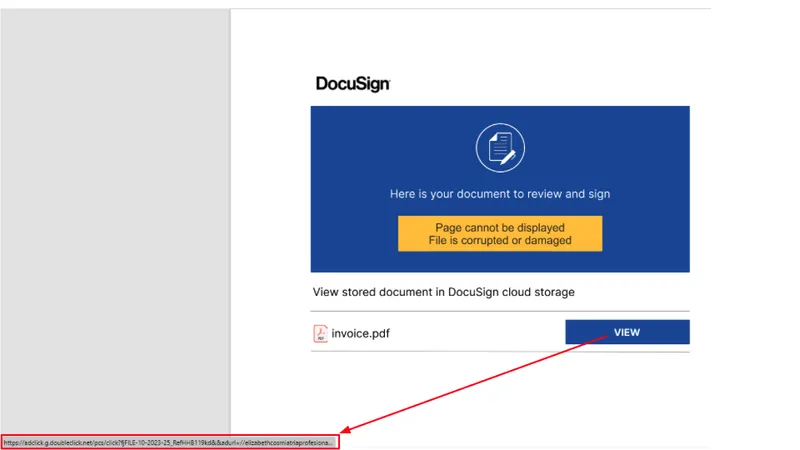
DarkGate is a malware loader and remote access trojan that continues to evolve with new variants and loading approaches. Its operators rent it out as a loader, and it delivers payloads such as remote access trojans and information stealers onto infected systems, arriving through phishing, malicious documents, and abuse of messaging platforms. The loader checks its environment before deploying, and its frequent rewrites reflect an operation that invests in evading analysis.
Stats
- First seen
- August 2023
- Last seen
- October 2026
Also known as
DarkgateLNKDarkGate
MITRE ATT&CK techniques
58 techniques across 13 tactics.
TA0002 Execution
TA0003 Persistence
TA0004 Privilege Escalation
TA0005 Stealth
- T1027Obfuscated Files or Information
- T1027.013Encrypted/Encoded File
- T1027Obfuscated Files or Information
- T1027.013Encrypted/Encoded File
- T1036Masquerading
- T1036Masquerading
- T1055Process Injection
- T1055.012Process Hollowing
- T1070Indicator Removal
- T1070.004File Deletion
- T1134Access Token Manipulation
- T1134.004Parent PID Spoofing
- T1140Deobfuscate/Decode Files or Information
- T1480Execution Guardrails
- T1497Virtualization/Sandbox Evasion
- T1497.001System Checks
- T1564Hide Artifacts
- T1564.001Hidden Files and Directories
- T1574Hijack Execution Flow
- T1622Debugger Evasion
TA0006 Credential Access
TA0007 Discovery
TA0009 Collection
TA0011 Command and Control
TA0010 Exfiltration
- T1041Exfiltration Over C2 Channel
TA0040 Impact
TA0112 Defense Impairment
- T1685Disable or Modify Tools
Associated campaigns
Alert name variants
| Alert Name |
|---|
| Binary.Trojan.DarkGate |
| Document-HTML.Trojan.Darkgate |
| Document-HTML.Trojan.DarkGate |
| Document-Office.Downloader.Darkgate |
| Document-Office.Downloader.DarkGate |
| Document-Office.Trojan.Darkgate |
| Document-PDF.Trojan.Darkgate |
| Document-Word.Downloader.Darkgate |
| Email-MSG.Trojan.Darkgate |
| Script-AutoIt.Malware.DarkGate |
Related IPS Signatures
Related blogs