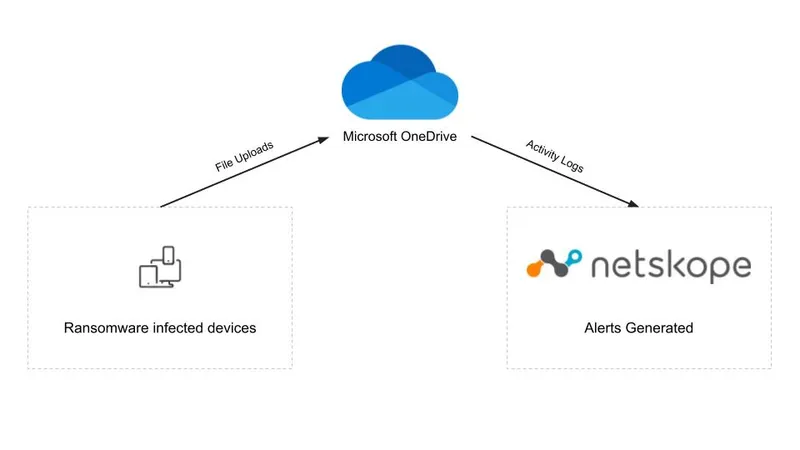
Description
DearCry (a.k.a. DoejoCrypt) is a ransomware family observed in March 2021 that infected unpatched Microsoft Exchange servers through the ProxyLogon vulnerabilities. After exploitation, the malware encrypts files and demands payment, and its campaigns showed how quickly ransomware crews weaponize newly disclosed remote code execution flaws in internet facing infrastructure. Organizations that patched Exchange promptly avoided the family, and its detections usually indicate an unpatched or previously breached mail server.
Stats
- First seen
- March 2022
- Last seen
- October 2026
Also known as
Dearcry
Alert name variants
| Alert Name |
|---|
| Gen:Heur.Mint.SP.Ransom.Dearcry.1 |
| Win32.Ransomware.DearCry |