Description
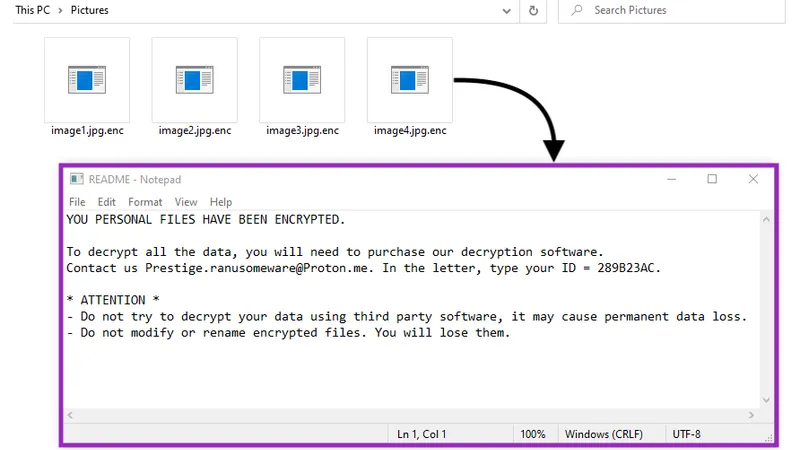
Prestige is ransomware targeting critical infrastructure and logistics organizations in Ukraine and neighboring countries, first observed in late 2022. Its operators delivered the payload through compromised cloud service connections, an unusual vector that highlighted the role of cloud tooling in destructive intrusions. The campaign marked the first time researchers observed Western made ransomware deployed against Ukrainian infrastructure, a notable shift in the regional conflict's cyber dimension.
Stats
- First seen
- October 2022
- Last seen
- October 2026
MITRE ATT&CK techniques
9 techniques across 4 tactics.
TA0002 Execution
TA0007 Discovery
- T1083File and Directory Discovery
Associated groups
Alert name variants
| Alert Name |
|---|
| Trojan.Ransom.Prestige.1 |
| Win32.Ransomware.Prestige |