Description
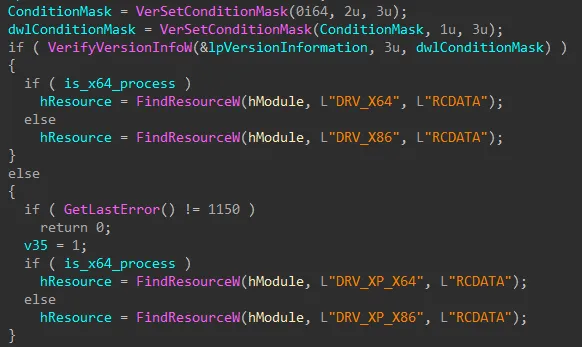
Shamoon is wiper malware first used by an Iranian group known as the Cutting Sword of Justice in 2012, with further versions observed in 2016 and 2018. It leveraged disk driver tooling to carry out data wiping at scale, and analysis has linked it to Kwampirs through shared artifacts and coding patterns. The name sometimes refers to the group using the malware as well as the malware itself.
Stats
- First seen
- March 2022
- Last seen
- October 2026
Also known as
DistTrack
MITRE ATT&CK techniques
24 techniques across 9 tactics.
TA0002 Execution
TA0004 Privilege Escalation
TA0005 Stealth
TA0007 Discovery
TA0008 Lateral Movement
TA0011 Command and Control
TA0040 Impact
TA0112 Defense Impairment
- T1112Modify Registry
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Worm.Shamoon |
| Trojan.Shamoon.A |
| Trojan.Shamoon.B |
| Win32.Trojan.DistTrack |
| Win32.Virus.DistTrack |
| Win64.Trojan.DistTrack |
| Win64.Trojan.Shamoon |