Description
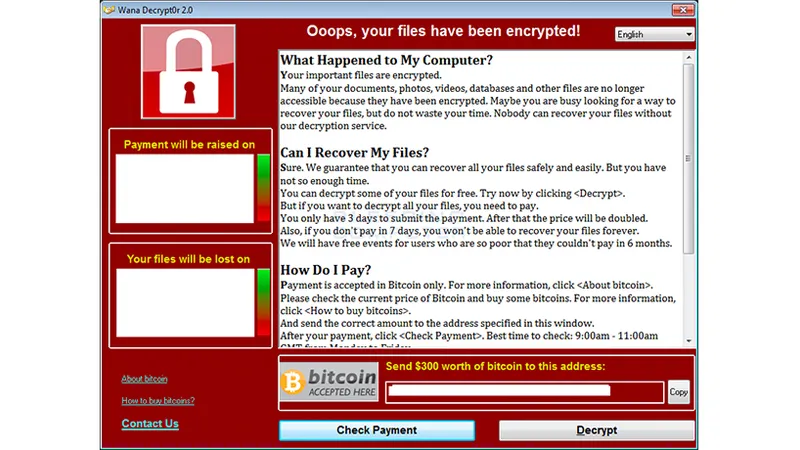
WannaCry is a ransomware worm that spread globally in May 2017 by exploiting the EternalBlue vulnerability in Windows file sharing, infecting hundreds of thousands of machines across more than 150 countries within days. The outbreak devastated hospitals, railways, and businesses, and a kill switch domain slowed its spread while organizations patched. Governments attributed the attack to North Korean actors, and the incident remains the defining case study in the cost of unpatched systems.
Stats
- First seen
- January 2022
- Last seen
- October 2026
Also known as
WanaCryWannaCryptorWannacry
MITRE ATT&CK techniques
16 techniques across 8 tactics.
TA0002 Execution
- T1047Windows Management Instrumentation
TA0007 Discovery
TA0008 Lateral Movement
TA0011 Command and Control
Associated groups
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Ransomware.WannaCry |
| Dump:Generic.Ransom.WannaCryptor.C2312CA0 |
| Gen:Variant.Ransom.Wannacry.125 |
| Gen:Variant.Ransom.Wannacry.126 |
| Gen:Variant.Ransom.WannaCry.24 |
| Gen:Variant.Ransom.WannaCryptor.30 |
| Generic.Ransom.WannaCryptor.292E472B |
| Generic.Ransom.WannaCryptor.92BB81C8 |
| Generic.Ransom.WannaCryptor.C40D3F15 |
| Generic.Ransom.WannaCryptor.CB9EE00D |