Description
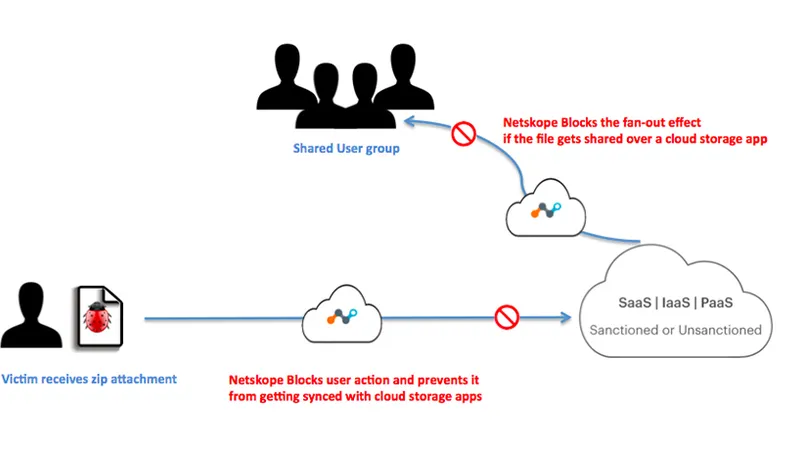
Zepto is a variant of the Locky ransomware that spread through massive spam campaigns, and it encrypts files with appended extensions while leaving ransom demands. It arrived through malicious documents and script downloads, and its frequent version updates tracked the broader Locky operation's churn. Detections under this name indicate exposure to the same delivery chains that made the Locky family one of the most voluminous ransomware operations of its era.
Stats
- First seen
- November 2022
- Last seen
- October 2026
Alert name variants
| Alert Name |
|---|
| Gen:Heur.Ransom.Zepto.1 |
| Gen:Variant.Ransom.Zepto.3 |
| Gen:Variant.Ransom.Zepto.4 |
| Win32.Ransomware.Zepto |