MalwareCredential Theft$100k in Crypto Drained by the Underground OperationOctober 1, 2026·8 min read
MalwareCommand and ControlMalware on the Blockchain: An Ongoing Campaign's New WebRTC TwistAugust 31, 2026·5 min read
MalwareSocial EngineeringEtherHiding in the Browser: ClickFix Chain Ends in AmateraAugust 25, 2026·12 min read
Social EngineeringMalwareFake CAPTCHA, Real Business: Traffic Distribution for HireAugust 4, 2026·8 min read
MalwareCredential TheftDevelopers in the Crosshairs: Fake AI Tools Deliver InfostealerAugust 3, 2026·8 min read
MalwareCredential TheftmacOS ClickFix Lures Deploy AppleScript Stealer & Persistent RATJune 17, 2026·11 min read
VulnerabilityMalwareDirtyFrag: Two Kernel Bugs Give Root on All Major Linux DistrosMay 8, 2026·2 min read
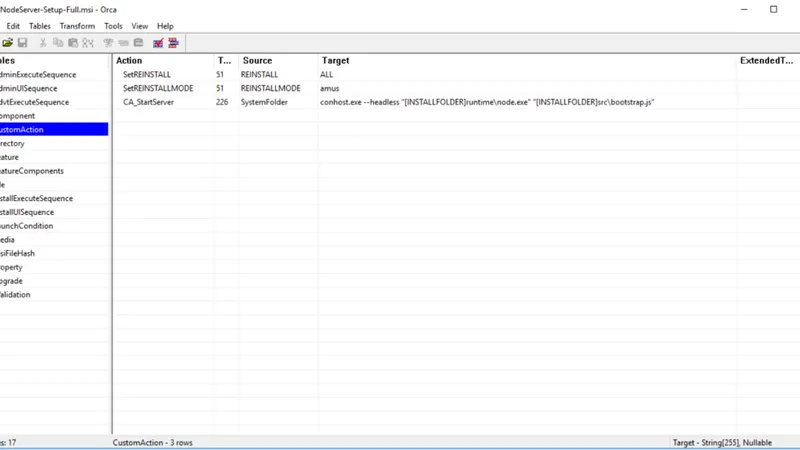
MalwareCredential TheftOpenClaw's Hologram: Fake Installer Ships Rust InfostealerMay 7, 2026·15 min read
MalwareSupply ChainShai-Hulud Resurfaces: Intercom-client@7.0.4 Harvesting Github CredentialsApril 30, 2026·1 min read
MalwareCredential TheftmacOS ClickFix Campaign: AppleScript Stealers & New Terminal ProtectionsApril 20, 2026·6 min read
Malware CryptoFrom ClickFix to MaaS: Exposing a Modular Windows RAT and Its Admin PanelApril 6, 2026·8 min read
MalwareSupply ChainOpenClaw Trap: AI-Assisted Lure Factory Targets Developers & GamersMarch 23, 2026·13 min read
PhishingMalwareAttackers Weaponize Signed RMM Tools via Zoom, Meet, & Teams LuresFebruary 12, 2026·3 min read
MalwareSupply ChainShai-Hulud 2.0: Aggressive, Automated, and Fast SpreadingNovember 26, 2025·26 min read
MalwareCredential TheftRedTiger: New Red Teaming Tool in the Wild Targeting Gamers and Discord AccountsOctober 23, 2025·10 min read
MalwarePhishingPureHVNC RAT Using Fake High-level Job Offers from Fashion and Beauty BrandsMay 28, 2025·7 min read
MalwareCredential TheftNew Evasive Campaign Delivers LegionLoader via Fake CAPTCHA & CloudFlare TurnstileApril 4, 2025·8 min read
RansomwareMalwareAnalyzing Elysium, a Variant of the Ghost (Cring) Ransomware FamilyMarch 11, 2025·4 min read
MalwareCredential TheftLumma Stealer: Fake CAPTCHAs & New Techniques to Evade DetectionJanuary 23, 2025·5 min read
MalwareCredential TheftPython NodeStealer Targets Facebook Ads Manager with New TechniquesNovember 20, 2024·5 min read
MalwareCloudGitHub Comments from Legitimate Repositories Exploited to Deliver Remcos RATOctober 21, 2024·2 min read
CloudMalwareCloud Threats Memo: Iranian Threat Actors Continue to Exploit AzureSeptember 11, 2024·3 min read
MalwareLatrodectus Rapid Evolution Continues With Latest New Payload FeaturesAugust 29, 2024·6 min read
RansomwareMalwareREPLAY: Revisiting Play Ransomware Anti-Analysis TechniquesAugust 8, 2024·9 min read
CloudMalwareCloud Threats Memo: CloudSorcerer, a Recently Discovered APT, is Exploiting Multiple Legitimate Cloud ServicesJuly 12, 2024·2 min read
CloudMalwareTwo Recent Campaigns from Brazil and Korea Exploiting Legitimate Cloud ServicesJune 13, 2024·3 min read
MalwareCredential TheftFrom Delivery To Execution: An Evasive Azorult Campaign Smuggled Through Google SitesMarch 15, 2024·9 min read
MalwarePhishingCloud Threats Memo: Google Drive Abused to Target Organizations in Asian CountriesMarch 6, 2024·2 min read
MalwareCloudCloud Threats Memo: Back to the Basics: New DarkGate Campaign Exploiting Microsoft TeamsFebruary 9, 2024·3 min read
MalwarePhishingThreat Actors Distributing Screenshotter Malware from OneDriveJanuary 26, 2024·2 min read
MalwarePhishingA Look at the Nim-based Campaign Using Microsoft Word Docs to Impersonate the Nepali GovernmentDecember 20, 2023·6 min read
MalwareCredential TheftCloud Threats Memo: A Parasite Exploiting Legitimate Cloud ServicesDecember 1, 2023·3 min read
MalwareCloudCloud Threats Memo: Multiple DarkGate Loader Campaigns Exploiting Legitimate Cloud ServicesOctober 30, 2023·3 min read
MalwareCredential TheftNew Python NodeStealer Goes Beyond Facebook Credentials, Now Stealing All Browser Cookies and Login CredentialsSeptember 14, 2023·6 min read
MalwareCloudCloud Threats Memo: Russian State-sponsored Threat Actors Increasingly Exploiting Legitimate Cloud ServicesAugust 4, 2023·2 min read
VulnerabilityPhishingNetskope Threat Coverage: Microsoft Office and Windows Zero Day (CVE-2023-36884)July 20, 2023·1 min read
MalwarePhishingCloud Threats Memo: Another State-Sponsored Actor Exploiting DropboxJuly 17, 2023·2 min read
MalwareCloudCloud Threats Memo: A Recent Campaign Exploiting Digital Trust Through GithubJune 26, 2023·3 min read
MalwarePhishingCloud Threats Memo: Threat Actors Continue to Exploit the Flexibility of GitHub for Malicious PurposesJune 5, 2023·3 min read
CloudMalwareCloud Threats Memo: More Details on Long-Lasting Campaigns Targeting Eastern EuropeMay 19, 2023·2 min read
CloudMalwareCloud Threats Memo: North-Korean State-Sponsored Threat Actors Continue to Exploit Legitimate Cloud ServicesMay 4, 2023·3 min read
CloudMalwareCloud Threats Memo: Threat Actors Increasingly Exploiting Google DriveApril 21, 2023·3 min read
CloudEspionageNetskope Cloud Threats Memo: Cyber Espionage Campaign Abusing OneDrive and DropboxMarch 29, 2023·2 min read
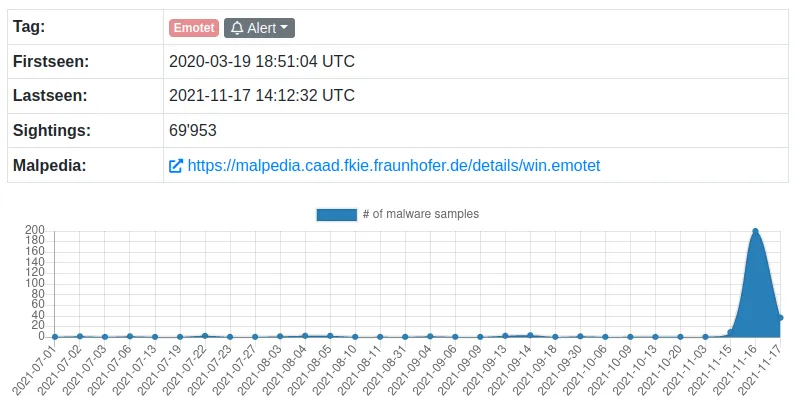
MalwareBotnetEmotet Comeback: New Campaign Using Binary Padding to Evade DetectionMarch 22, 2023·3 min read
MalwareEspionageCloud Threats Memo: Cyber Espionage Campaign Using Remote Access ToolsMarch 14, 2023·2 min read
MalwareEspionageCloud Threats Memo: Multiple Different Cloud Apps Abused in a Single Cyber Espionage CampaignMarch 3, 2023·3 min read
MalwareCloudCloud Threats Memo: Threat Actors Continue to Abuse Cloud Services to Deliver Malware in 2023January 19, 2023·3 min read
MalwareCloudCloud Threats Memo: Understanding the Dead Drop Resolver TechniqueDecember 13, 2022·2 min read
MalwareCloudCloud Threats Memo: Cyber Espionage Exploiting Google Drive for C2 InfrastructureDecember 6, 2022·2 min read
MalwarePhishingCloud Threats Memo: Yet Another Cyber Espionage Campaign Exploiting Cloud ServicesNovember 30, 2022·2 min read
RansomwareMalwareBlackCat Ransomware: Tactics and Techniques From a Targeted AttackNovember 9, 2022·13 min read
MalwareCloudCloud Threats Memo: Lampion Exploiting WeTransfer to Deliver MalwareSeptember 13, 2022·2 min read
PhishingCloudCloud Threats Memo: Cloud Storage Services are Increasingly Exploited to Deliver MalwareAugust 2, 2022·2 min read
MalwareCloudCloud Threats Memo: Dropbox: Flexible Cloud Storage Increasingly Exploited by AttackersJuly 26, 2022·2 min read
VulnerabilityMalwareCVE-2022-30190: New Zero-Day Vulnerability (Follina) in Microsoft Support Diagnostic ToolJune 1, 2022·3 min read
MalwareCredential TheftRedLine Stealer Campaign Using Binance Mystery Box Videos to Spread GitHub-Hosted PayloadMay 12, 2022·6 min read
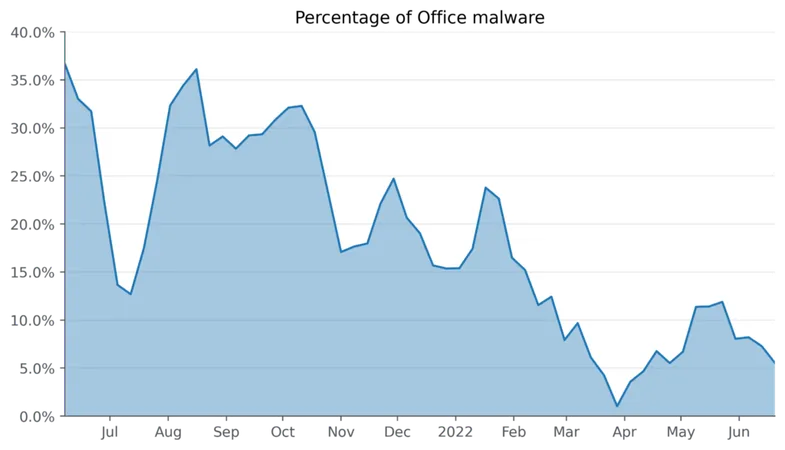
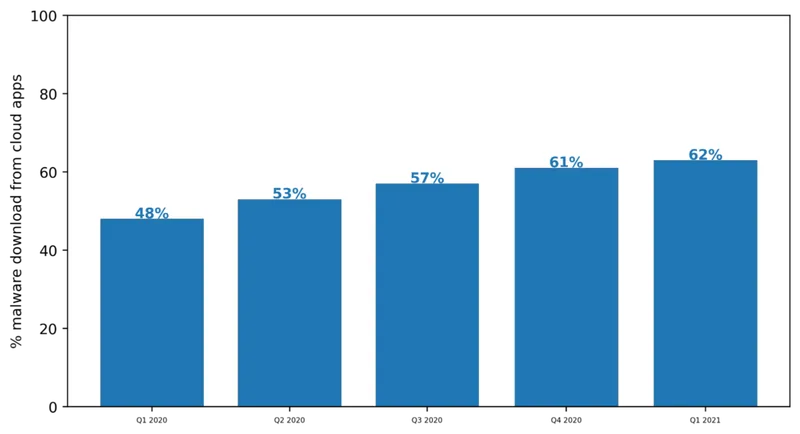
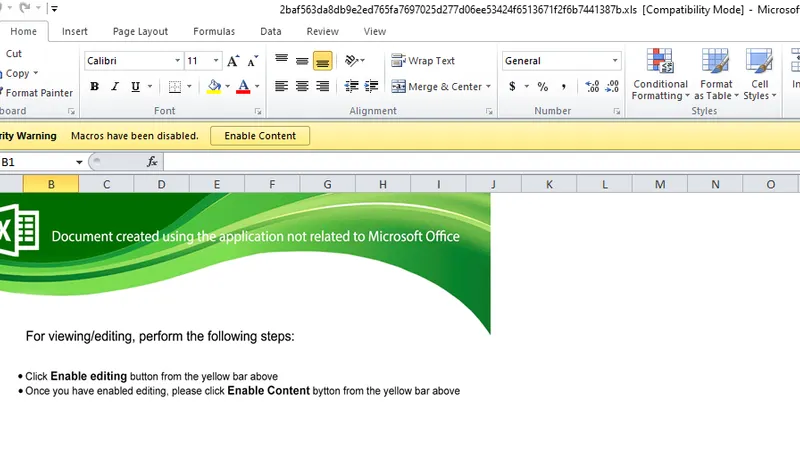
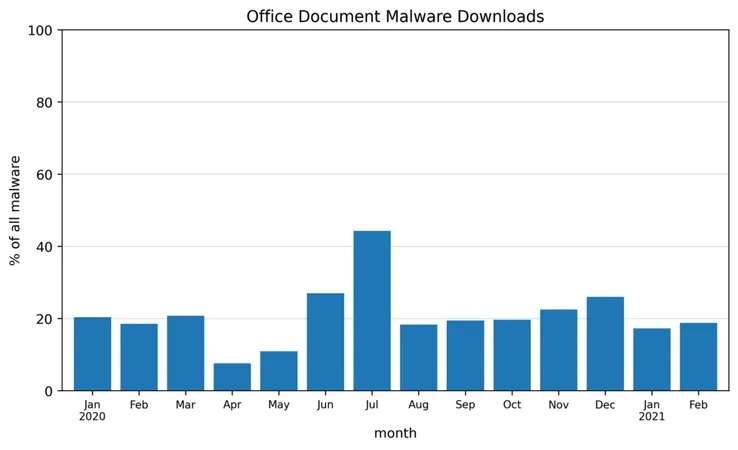
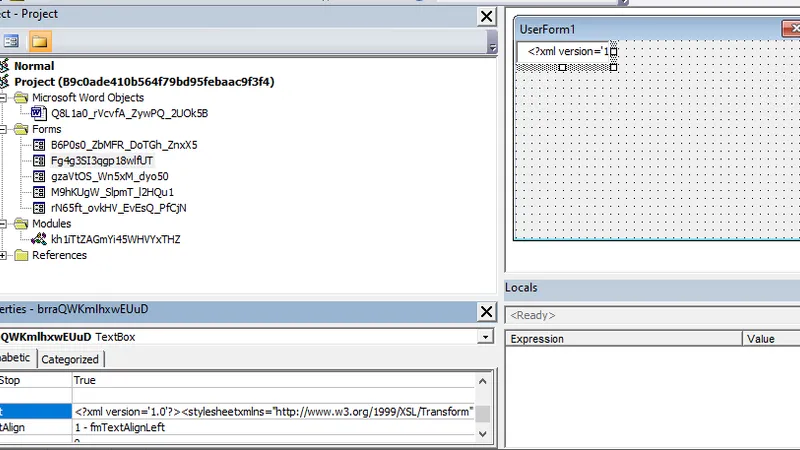
MalwarePhishingOffice Documents and Cloud Apps: Perfect for Malware DeliveryMarch 22, 2022·5 min read
MalwarePhishingMicrosoft Office: VBA Blocked By Default in Files From the InternetFebruary 24, 2022·7 min read
PhishingMalwareInfected PowerPoint Files Using Cloud Services to Deliver Multiple MalwareJanuary 24, 2022·7 min read
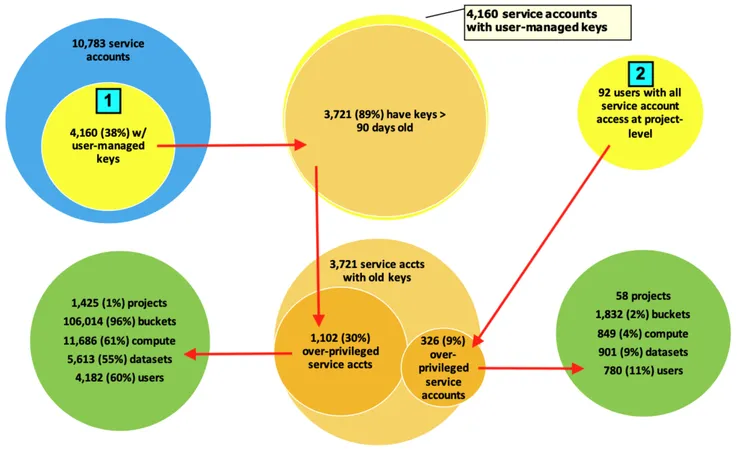
CloudCredential TheftOver-Privileged Service Accounts Create Escalation of Privileges and Lateral Movement in Google CloudDecember 2, 2021·13 min read
MalwareCloudCloud Threats Memo: BazarLoader Exploiting Popular Cloud ServicesOctober 25, 2021·2 min read
MalwareCommand and ControlSquirrelWaffle: New Malware Loader Delivering Cobalt Strike and QakBotOctober 7, 2021·6 min read
MalwareBazarLoader: Using LoLBins through Office Documents to Deliver PayloadsSeptember 22, 2021·4 min read
MalwarePhishingCloud Threats Memo: Hancitor Continues Exploiting DocuSign and Google Docs TemplatesJuly 15, 2021·1 min read
MalwareCloudCloud Threats Memo: Preventing the Exploitation of Dropbox as a Command and ControlJuly 8, 2021·1 min read
MalwarePhishingCloud Threats Memo: Malicious Campaigns Taking Advantage of Well-known Collaboration AppsApril 20, 2021·1 min read
PhishingMalwareCloud Threats Memo: LinkedIn Spearphishing and Malware-as-a-ServiceApril 13, 2021·1 min read
PhishingMalwareCloud Threats Memo: Dridex Phishing Posing as COVID-19 ReliefMarch 19, 2021·1 min read
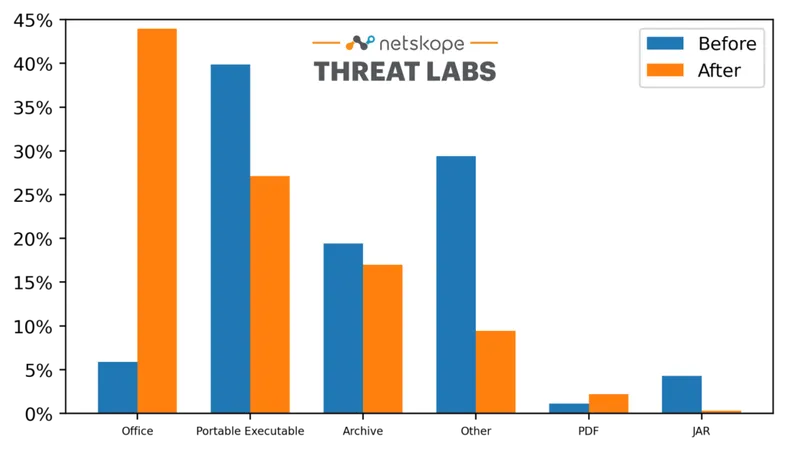
MalwarePhishingCloud and Threat Report: Was 2020 the Year of the Malicious Office Document?March 16, 2021·3 min read
MalwarePhishingCloud Threats Memo: Protecting Against Hancitor Distributed Through Malicious Office DocumentsMarch 4, 2021·1 min read
MalwareCloudCloud Threats Memo: Hard Times for ARM-based Mac M1 ProcessorsFebruary 23, 2021·2 min read
Supply ChainMalwareNetskope Threat Coverage: SUNBURST & FireEye Red Team (Offensive Security) ToolsDecember 15, 2020·2 min read
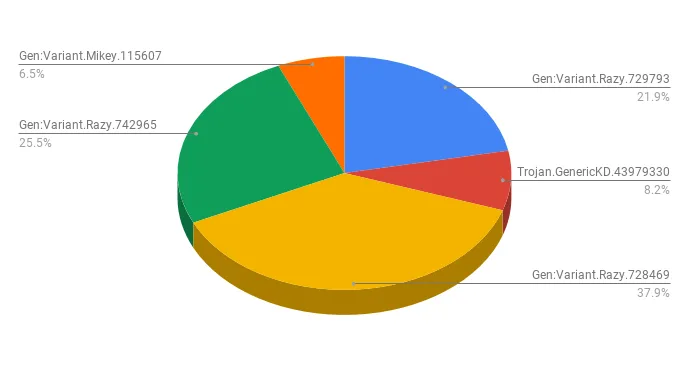
Credential TheftMalwareHere Comes TroubleGrabber: Stealing Credentials Through DiscordNovember 13, 2020·9 min read
CloudMalwareLeaky Chats: Accidental Exposure and Malware in Discord AttachmentsNovember 4, 2020·5 min read
MalwareBotnetOMNI (MIRAI variant) Botnet Infections Detected in Polycom Video Conferencing DevicesOctober 26, 2020·6 min read
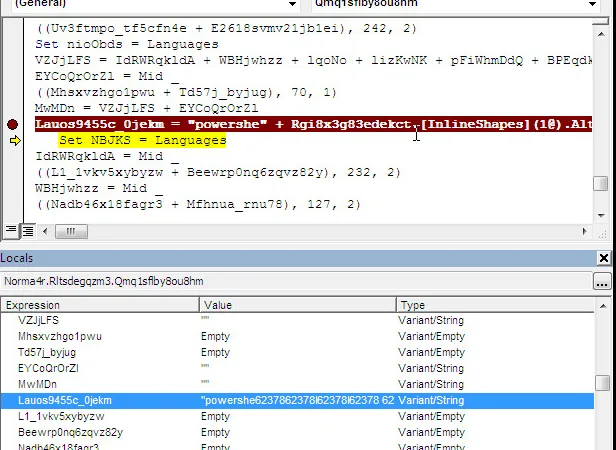
MalwarePhishingYou Can Run, But You Can’t Hide: Detecting Malicious Office DocumentsOctober 8, 2020·7 min read
MalwareCloudDangerous Docs: Surge in Cloud-delivered Malicious Office DocumentsSeptember 30, 2020·3 min read
CloudMalwareLeaky Images: Accidental Exposure and Malware in Google Photos and HangoutsSeptember 29, 2020·5 min read
MalwareVulnerabilityTelegramRAT evades traditional defenses via the cloudDecember 18, 2017·7 min read
MalwareVulnerabilityTargeted Attack BadWolf Exploits Office Vulnerabilities to Exfiltrate DataDecember 14, 2017·5 min read
PhishingMalwarePhishing Attacks on Retail Industry Ramp Up as the Holiday Shopping Season ApproachesDecember 13, 2017·5 min read
MalwareCloudNetskope Threat Research Labs analysis of ongoing cloud aware data theft attackJuly 25, 2017·4 min read
VulnerabilityMalwareLatest Microsoft Office Zero-day Served via Godzilla BotnetApril 11, 2017·1 min read
CloudMalwareVirlock’s resurgence poses bigger threat to file syncing over the cloudJanuary 30, 2017·2 min read
CloudMalwareNitol Botnet makes a resurgence with evasive sandbox analysis techniqueOctober 14, 2016·4 min read
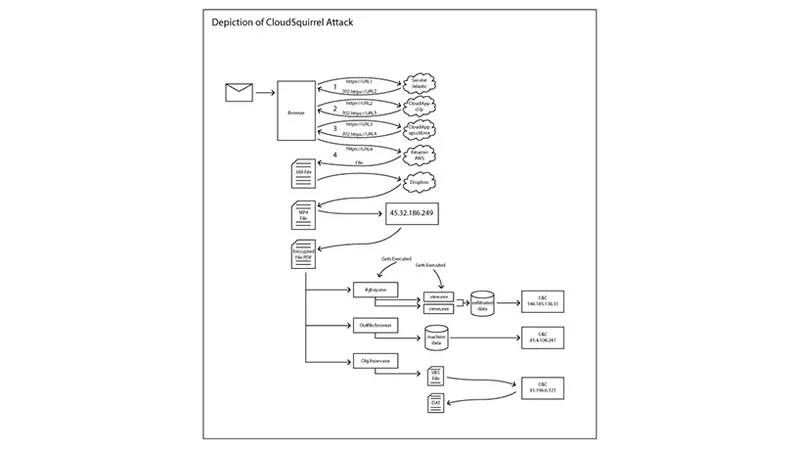
CloudMalwareNetskope Threat Research Labs Technical Analysis: CloudSquirrel MalwareJuly 27, 2016·8 min read
CloudMalwareZepto variant of Locky ransomware delivered via popular Cloud Storage appsJuly 19, 2016·5 min read
CloudMalwareCloudSquirrel Malware Squirrels Away Sensitive User Data Using Popular Cloud AppsJuly 15, 2016·2 min read
CloudMalwareAnatomy of a Ransomware Attack: Cerber Uses Steganography to “Hide in Plain Sight”June 30, 2016·6 min read