Description
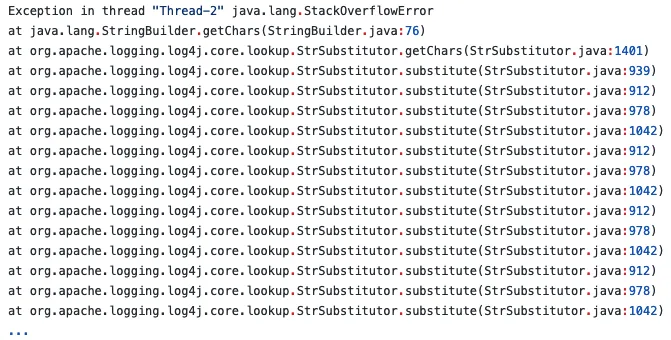
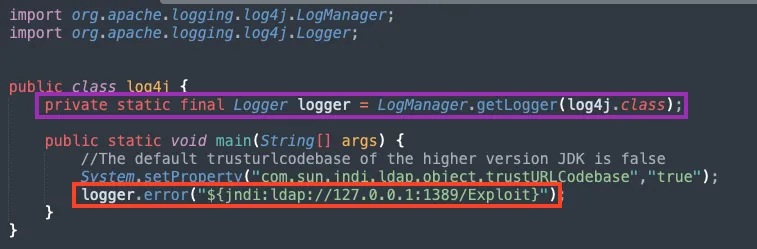
Detects indicators of compromise consistent with an active intrusion using JNDI LDAP searchResEntry dynamic code download attempt. The underlying flaw carries the identifier CVE-2021-4104, CVE-2021-44228, CVE-2021-44832, and 2 others. The flaw, known as Log4Shell, saw mass exploitation within hours of disclosure.
CVEs
Related malware families
Related blogs