Description
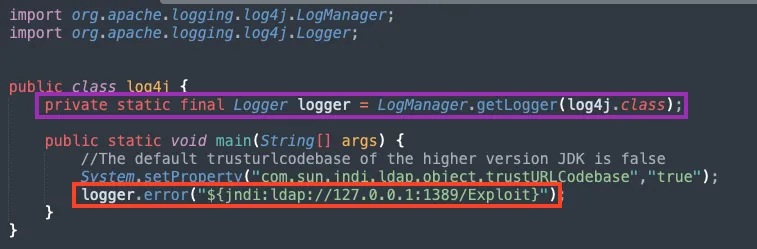
This detection identifies exploitation attempts targeting CVE-2021-44228, which has a CRITICAL severity rating. Apache Log4j2 2.0-beta9 through 2.15.0 does not protect JNDI features used in configuration, log messages, and parameters against cyberattacker controlled LDAP and other JNDI endpoints. A cyberattacker who can control log messages or their parameters can execute arbitrary code loaded from LDAP servers when the configuration enables message lookup substitution, an issue known as Log4Shell. Later releases turned the behavior off and then removed it entirely, and the vulnerability affects only log4j-core.
Stats
- First seen
- July 2022
- Last seen
- October 2026
CVEs
Alert name variants
| Alert Name |
|---|
| Binary.Exploit.CVE-2021-44228 |
| ByteCode-JAVA.Exploit.CVE-2021-44228 |
| Document-HTML.Exploit.CVE-2021-44228 |
| Linux.Exploit.CVE-2021-44228 |
| Package.Exploit.CVE-2021-44228 |
| Win32.Exploit.CVE-2021-44228 |
| Win64.Exploit.CVE-2021-44228 |
Related IPS Signatures
Related blogs