Description
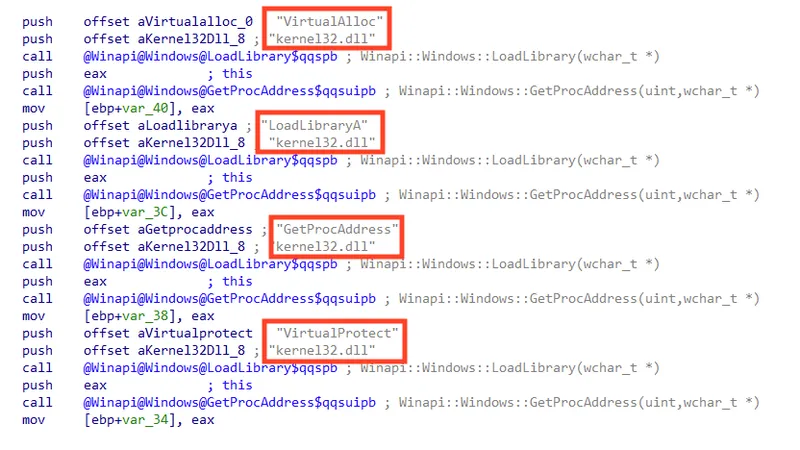
Astaroth is a trojan and information stealer known to affect companies in Europe, Brazil, and throughout Latin America, publicly known since at least late 2017.
Stats
- First seen
- May 2022
- Last seen
- October 2026
Also known as
Guildma
MITRE ATT&CK techniques
36 techniques across 9 tactics.
TA0002 Execution
TA0003 Persistence
TA0005 Stealth
- T1027Obfuscated Files or Information
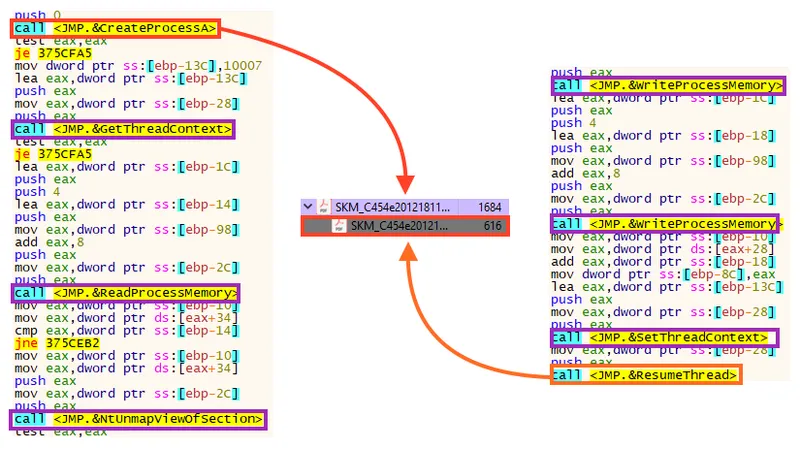
- T1055Process Injection
- T1055.012Process Hollowing
- T1140Deobfuscate/Decode Files or Information
- T1218System Binary Proxy Execution
- T1220XSL Script Processing
- T1497Virtualization/Sandbox Evasion
- T1497.001System Checks
- T1564Hide Artifacts
- T1574Hijack Execution Flow
- T1574.001DLL
TA0007 Discovery
TA0009 Collection
TA0011 Command and Control
TA0010 Exfiltration
- T1041Exfiltration Over C2 Channel
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Trojan.Guildma |
| Document-HTML.Downloader.Astaroth |
| Email-MSG.Downloader.Astaroth |
| Script-JS.Downloader.Astaroth |
| Script-JS.Downloader.Guildma |
| Script-JS.Trojan.Astaroth |
| Script-JS.Trojan.Guildma |
| Shortcut.Trojan.Astaroth |
| Win32.Spyware.Guildma |
| Win32.Trojan.Astaroth |