Description
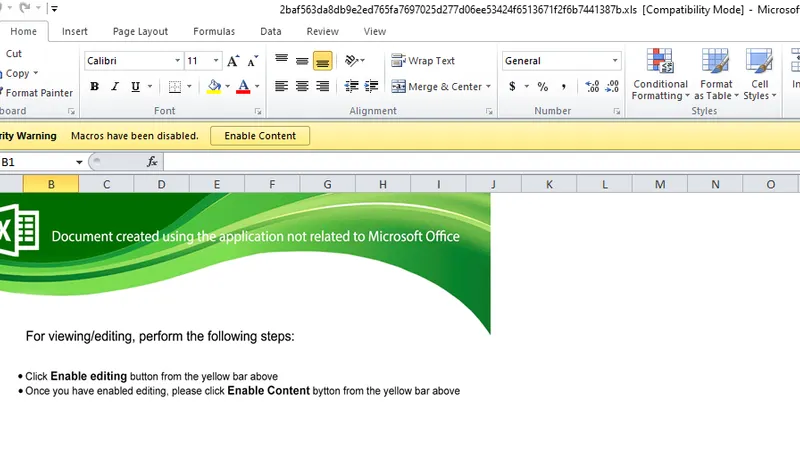
Bazar (a.k.a. BazarLoader, BazarLoader) is a backdoor and downloader associated with the Wizard Spider threat group (the criminal network behind TrickBot and Conti). It arrives through phishing emails with malicious links or attachments, establishes a persistent channel to its operators, and downloads additional payloads, including ransomware, onto corporate networks. Its authors have rewritten it in multiple languages and frequently change its infrastructure, which has made tracking the family an ongoing effort.
Stats
- First seen
- March 2022
- Last seen
- October 2026
Also known as
BazaarLoaderBazaloaderBazarLoaderBazarloader
MITRE ATT&CK techniques
51 techniques across 8 tactics.
TA0002 Execution
TA0003 Persistence
TA0005 Stealth
TA0007 Discovery
- T1012Query Registry
- T1016System Network Configuration Discovery
- T1018Remote System Discovery
- T1033System Owner/User Discovery
- T1057Process Discovery
- T1082System Information Discovery
- T1083File and Directory Discovery
- T1087Account Discovery
- T1124System Time Discovery
- T1135Network Share Discovery
- T1482Domain Trust Discovery
- T1518Software Discovery
- T1518.001Security Software Discovery
- T1518Software Discovery
- T1518.001Security Software Discovery
- T1614System Location Discovery
- T1614.001System Language Discovery
TA0009 Collection
- T1005Data from Local System
TA0011 Command and Control
Associated groups
Associated campaigns
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Downloader.BazarLoader |
| DeepScan:Generic.Bazar.3.A7B72870 |
| Document-Excel.Trojan.Bazarloader |
| Document-Excel.Trojan.BazarLoader |
| Document-Office.Downloader.BazarLoader |
| Document-Word.Downloader.BazarLoader |
| Document-Word.Trojan.Bazarloader |
| Dump:Generic.Bazar.3.A7B72870 |
| Gen:Variant.BazarLoader.2 |
| Generic.Bazar.1.B267EA4F |
Related IPS Signatures
Related blogs