Description
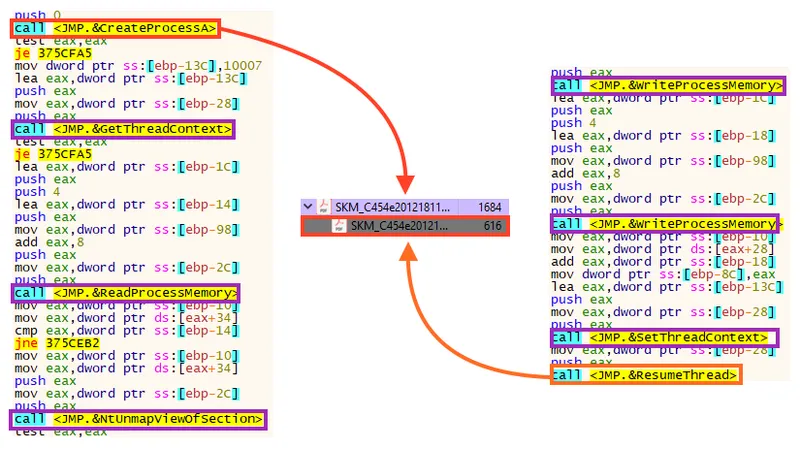
TrickBot is a modular banking trojan and malware loader that has been active since 2016, evolving from credential theft into the core of a major criminal ecosystem. Its module system added reconnaissance, lateral movement, and delivery capabilities, and it fed access and payloads to operations such as Ryuk and Conti. Repeated takedown efforts disrupted its infrastructure, yet rebuilt versions and successor tooling keep its tactics alive in modern campaigns.
Stats
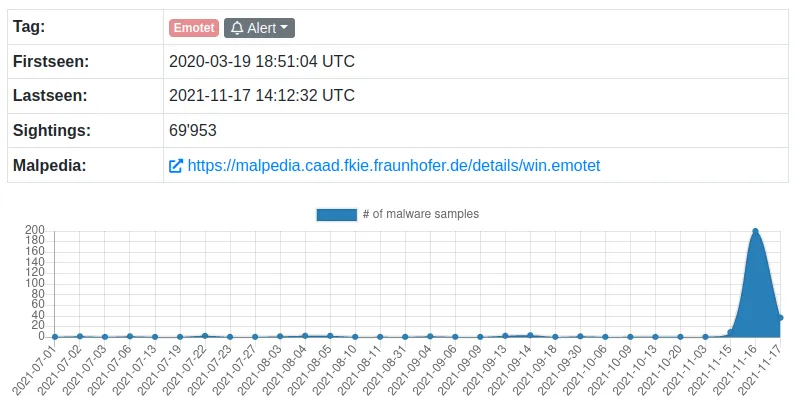
- First seen
- February 2022
- Last seen
- October 2026
Also known as
TotbrickTrickbot
MITRE ATT&CK techniques
55 techniques across 12 tactics.
TA0002 Execution
TA0003 Persistence
TA0005 Stealth
TA0006 Credential Access
TA0007 Discovery
- T1007System Service Discovery
- T1016System Network Configuration Discovery
- T1018Remote System Discovery
- T1033System Owner/User Discovery
- T1057Process Discovery
- T1069Permission Groups Discovery
- T1082System Information Discovery
- T1083File and Directory Discovery
- T1087Account Discovery
- T1135Network Share Discovery
- T1482Domain Trust Discovery
TA0009 Collection
TA0011 Command and Control
TA0010 Exfiltration
- T1041Exfiltration Over C2 Channel
TA0040 Impact
- T1495Firmware Corruption
Associated groups
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Spyware.Trickbot |
| ByteCode-MSIL.Spyware.TrickBot |
| ByteCode-MSIL.Trojan.TrickBot |
| DeepScan:Generic.TrickBot.1832592A |
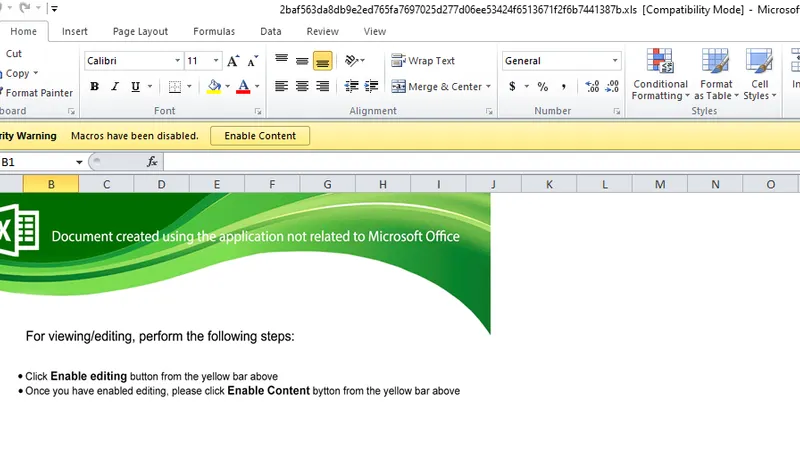
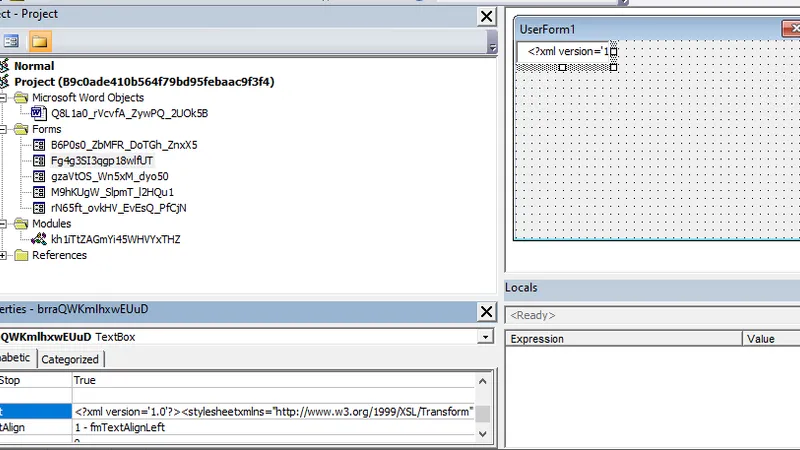
| Document-Excel.Downloader.TrickBot |
| Document-Excel.Trojan.TrickBot |
| Document-Office.Downloader.TrickBot |
| Document-Office.Trojan.TrickBot |
| Document-Word.Trojan.TrickBot |
| Dump:Generic.TrickBot.1832592A |
Related IPS Signatures
Related blogs