

Description
Remcos is a remote access trojan sold as a legitimate surveillance product that provides an extensive list of features to remotely control devices, and cyberattackers popularly abuse it in many campaigns. Its capabilities include remote desktop, keystroke logging, camera access, and file management, and its builder produces customized implants for each buyer. Distributed through phishing and loader chains, it remains one of the most commonly detected commercial RATs.
Stats
- First seen
- February 2022
- Last seen
- October 2026
Also known as
RemcosRATRemcosrat
MITRE ATT&CK techniques
38 techniques across 10 tactics.
TA0002 Execution
TA0003 Persistence
TA0004 Privilege Escalation
TA0005 Stealth
TA0007 Discovery
TA0009 Collection
TA0011 Command and Control
TA0112 Defense Impairment
- T1112Modify Registry
Associated groups
Associated campaigns
Alert name variants
| Alert Name | Engine |
|---|---|
| Binary.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| ByteCode-MSIL.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| ByteCode-MSIL.Downloader.Remcos | ATP Sandbox Adv. Heuristics |
| ByteCode-MSIL.Spyware.Remcos | ATP Sandbox Adv. Heuristics |
| ByteCode-MSIL.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| ByteCode-MSIL.Trojan.RemcosRAT | ATP Sandbox Adv. Heuristics |
| DeepScan:Generic.Remcos.0AD18DBD | AV |
| DeepScan:Generic.Remcos.0E4A57A9 | AV |
| DeepScan:Generic.Remcos.145BCFF3 | AV |
| DeepScan:Generic.Remcos.157C6A34 | AV |
| DeepScan:Generic.Remcos.1B43BE21 | AV |
| DeepScan:Generic.Remcos.2025940B | AV |
| DeepScan:Generic.Remcos.24501F03 | AV |
| DeepScan:Generic.Remcos.260FC5FD | AV |
| DeepScan:Generic.Remcos.2CF3BFB3 | AV |
| DeepScan:Generic.Remcos.316EC261 | AV |
| DeepScan:Generic.Remcos.3199DD05 | AV |
| DeepScan:Generic.Remcos.3952DC10 | AV |
| DeepScan:Generic.Remcos.446BC206 | AV |
| DeepScan:Generic.Remcos.450E34AD | AV |
| DeepScan:Generic.Remcos.4A24C7C8 | AV |
| DeepScan:Generic.Remcos.50C93B57 | AV |
| DeepScan:Generic.Remcos.532D89D7 | AV |
| DeepScan:Generic.Remcos.53717B15 | AV |
| DeepScan:Generic.Remcos.5AA4A9B2 | AV |
| DeepScan:Generic.Remcos.5BEFD07E | AV |
| DeepScan:Generic.Remcos.62287E42 | AV |
| DeepScan:Generic.Remcos.660F8EF5 | AV |
| DeepScan:Generic.Remcos.6C51EB95 | AV |
| DeepScan:Generic.Remcos.71AE33B5 | AV |
| DeepScan:Generic.Remcos.7579FD45 | AV |
| DeepScan:Generic.Remcos.7E06FB9B | AV |
| DeepScan:Generic.Remcos.83A002AA | AV |
| DeepScan:Generic.Remcos.83DA6EA8 | AV |
| DeepScan:Generic.Remcos.887A3199 | AV |
| DeepScan:Generic.Remcos.8BB1E6BE | AV |
| DeepScan:Generic.Remcos.8EE12CDB | AV |
| DeepScan:Generic.Remcos.94826D9E | AV |
| DeepScan:Generic.Remcos.98C291A1 | AV |
| DeepScan:Generic.Remcos.9AA8D9AA | AV |
| DeepScan:Generic.Remcos.9E4C8AF5 | AV |
| DeepScan:Generic.Remcos.A27C3960 | AV |
| DeepScan:Generic.Remcos.A949DFC7 | AV |
| DeepScan:Generic.Remcos.B1936791 | AV |
| DeepScan:Generic.Remcos.C40F687B | AV |
| DeepScan:Generic.Remcos.CD9A084D | AV |
| DeepScan:Generic.Remcos.D1174F97 | AV |
| DeepScan:Generic.Remcos.D4B7C843 | AV |
| DeepScan:Generic.Remcos.DC631D07 | AV |
| DeepScan:Generic.Remcos.DC888FD1 | AV |
| DeepScan:Generic.Remcos.E247242B | AV |
| DeepScan:Generic.Remcos.E7E3CC66 | AV |
| DeepScan:Generic.Remcos.E9DAD608 | AV |
| DeepScan:Generic.Remcos.EAE8FFD7 | AV |
| DeepScan:Generic.Remcos.F1B84143 | AV |
| DeepScan:Generic.Remcos.F39BA3B6 | AV |
| DeepScan:Generic.Remcos.F5F5D1B5 | AV |
| DeepScan:Generic.Remcos.FE0519B3 | AV |
| Document-Excel.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Document-HTML.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Document-HTML.Downloader.Remcos | ATP Sandbox Adv. Heuristics |
| Document-Office.Downloader.Remcos | ATP Sandbox Adv. Heuristics |
| Document-Office.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Document-PDF.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Document-Word.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Document-Word.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Dropped:Generic.Remcos.C094B26F | AV |
| Dropped:Generic.Remcos.D39AB2F6 | AV |
| Dump:Generic.Remcos.1CEBA797 | AV |
| Dump:Generic.Remcos.344FA4F6 | AV |
| Dump:Generic.Remcos.3FBA42DD | AV |
| Dump:Generic.Remcos.50119FF6 | AV |
| Dump:Generic.Remcos.6869D405 | AV |
| Dump:Generic.Remcos.8862D53D | AV |
| Dump:Generic.Remcos.8C88DCB9 | AV |
| Dump:Generic.Remcos.920EF17C | AV |
| Dump:Generic.Remcos.9D006679 | AV |
| Dump:Generic.Remcos.A58CC589 | AV |
| Dump:Generic.Remcos.B08ED8A7 | AV |
| Dump:Generic.Remcos.B09C89C8 | AV |
| Dump:Generic.Remcos.B832EF31 | AV |
| Dump:Generic.Remcos.B87091B1 | AV |
| Dump:Generic.Remcos.BEDD5F4C | AV |
| Dump:Generic.Remcos.DFE51DF9 | AV |
| Dump:Generic.Remcos.EDA16ABF | AV |
| Dump:Generic.Remcos.F1511AFA | AV |
| Dump:Generic.Remcos.F3E7EA60 | AV |
| Dump:Generic.Remcos.FABC647A | AV |
| Email-MIME.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Email-MIME.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Email-MSG.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Gen:Heur.Mint.RemcosRAT.1 | AV |
| Gen:Variant.Remcos.10 | AV |
| Gen:Variant.Remcos.15 | AV |
| Gen:Variant.Remcos.23 | AV |
| Gen:Variant.RemcosRAT.1 | AV |
| Gen:Variant.RemcosRAT.145 | AV |
| Gen:Variant.RemcosRAT.18 | AV |
| Gen:Variant.RemcosRAT.67 | AV |
| Generic.Remcos.02FBA5D6 | AV |
| Generic.Remcos.03200FC3 | AV |
| Generic.Remcos.041EEA59 | AV |
| Generic.Remcos.04990326 | AV |
| Generic.Remcos.058E1F24 | AV |
| Generic.Remcos.05C20D99 | AV |
| Generic.Remcos.05E3FD40 | AV |
| Generic.Remcos.06709544 | AV |
| Generic.Remcos.0764FE1C | AV |
| Generic.Remcos.0774708A | AV |
| Generic.Remcos.0910507B | AV |
| Generic.Remcos.0921EE85 | AV |
| Generic.Remcos.09806BF8 | AV |
| Generic.Remcos.099D505F | AV |
| Generic.Remcos.0A30D3D5 | AV |
| Generic.Remcos.0A5B1918 | AV |
| Generic.Remcos.0AEB0349 | AV |
| Generic.Remcos.0B44352C | AV |
| Generic.Remcos.0B969F89 | AV |
| Generic.Remcos.0C88C40F | AV |
| Generic.Remcos.0D0CEFB9 | AV |
| Generic.Remcos.0D46F9C9 | AV |
| Generic.Remcos.0D97CA3C | AV |
| Generic.Remcos.0E825F6E | AV |
| Generic.Remcos.0EF0CD0B | AV |
| Generic.Remcos.0F1A0D4E | AV |
| Generic.Remcos.0F54AA5E | AV |
| Generic.Remcos.0F9A5F45 | AV |
| Generic.Remcos.0FA5915E | AV |
| Generic.Remcos.1006BBF4 | AV |
| Generic.Remcos.11058B4E | AV |
| Generic.Remcos.110C1EFD | AV |
| Generic.Remcos.112CED6D | AV |
| Generic.Remcos.11A25AE3 | AV |
| Generic.Remcos.1237694D | AV |
| Generic.Remcos.1245E3B6 | AV |
| Generic.Remcos.12481E14 | AV |
| Generic.Remcos.12AB727E | AV |
| Generic.Remcos.12CDC907 | AV |
| Generic.Remcos.13284579 | AV |
| Generic.Remcos.138B30D4 | AV |
| Generic.Remcos.1391E001 | AV |
| Generic.Remcos.143E2412 | AV |
| Generic.Remcos.147FB3D8 | AV |
| Generic.Remcos.14D39BC3 | AV |
| Generic.Remcos.158B84BA | AV |
| Generic.Remcos.15BFEDC7 | AV |
| Generic.Remcos.15EE7010 | AV |
| Generic.Remcos.15FC84DF | AV |
| Generic.Remcos.1627F63F | AV |
| Generic.Remcos.16784802 | AV |
| Generic.Remcos.178B43EC | AV |
| Generic.Remcos.17A06C01 | AV |
| Generic.Remcos.17ABB07C | AV |
| Generic.Remcos.17E5F88A | AV |
| Generic.Remcos.18824FA4 | AV |
| Generic.Remcos.1975636E | AV |
| Generic.Remcos.1A6E5EA1 | AV |
| Generic.Remcos.1AAFE305 | AV |
| Generic.Remcos.1AD6655E | AV |
| Generic.Remcos.1BD6B009 | AV |
| Generic.Remcos.1EE2DAE0 | AV |
| Generic.Remcos.1F9EFA93 | AV |
| Generic.Remcos.217676CE | AV |
| Generic.Remcos.2191EEE1 | AV |
| Generic.Remcos.22434798 | AV |
| Generic.Remcos.23BA3608 | AV |
| Generic.Remcos.23C9AB06 | AV |
| Generic.Remcos.23CE69EB | AV |
| Generic.Remcos.249C38D8 | AV |
| Generic.Remcos.24F7C1A4 | AV |
| Generic.Remcos.25431839 | AV |
| Generic.Remcos.25B20CD6 | AV |
| Generic.Remcos.262CA01E | AV |
| Generic.Remcos.269616D5 | AV |
| Generic.Remcos.2699012F | AV |
| Generic.Remcos.27BAA5A3 | AV |
| Generic.Remcos.28D7F539 | AV |
| Generic.Remcos.28E0FB9A | AV |
| Generic.Remcos.2965D09A | AV |
| Generic.Remcos.298B782A | AV |
| Generic.Remcos.29C8D90D | AV |
| Generic.Remcos.2A2915FD | AV |
| Generic.Remcos.2A7FF5F5 | AV |
| Generic.Remcos.2AD82458 | AV |
| Generic.Remcos.2AE445A5 | AV |
| Generic.Remcos.2B0C87D9 | AV |
| Generic.Remcos.2B4A9DBB | AV |
| Generic.Remcos.2BF7C199 | AV |
| Generic.Remcos.2C076A17 | AV |
| Generic.Remcos.2CC9318B | AV |
| Generic.Remcos.2D0236B9 | AV |
| Generic.Remcos.2D1518BD | AV |
| Generic.Remcos.2D35EB2D | AV |
| Generic.Remcos.2DA5E714 | AV |
| Generic.Remcos.2E24E0E6 | AV |
| Generic.Remcos.2F445AA9 | AV |
| Generic.Remcos.2F800398 | AV |
| Generic.Remcos.2FB2C504 | AV |
| Generic.Remcos.2FE38B04 | AV |
| Generic.Remcos.3024D919 | AV |
| Generic.Remcos.30ECE132 | AV |
| Generic.Remcos.30F31E01 | AV |
| Generic.Remcos.313377C9 | AV |
| Generic.Remcos.31A4A958 | AV |
| Generic.Remcos.31AE3FEC | AV |
| Generic.Remcos.31AF7E4F | AV |
| Generic.Remcos.320D5C8F | AV |
| Generic.Remcos.327FDBB8 | AV |
| Generic.Remcos.332911C5 | AV |
| Generic.Remcos.3352F8C4 | AV |
| Generic.Remcos.337DD229 | AV |
| Generic.Remcos.340B1E30 | AV |
| Generic.Remcos.34302585 | AV |
| Generic.Remcos.34C1AD75 | AV |
| Generic.Remcos.37627AB5 | AV |
| Generic.Remcos.3791227E | AV |
| Generic.Remcos.37AE8B82 | AV |
| Generic.Remcos.3896950E | AV |
| Generic.Remcos.39796332 | AV |
| Generic.Remcos.3A923D77 | AV |
| Generic.Remcos.3ABAF767 | AV |
| Generic.Remcos.3BE41B44 | AV |
| Generic.Remcos.3BF92679 | AV |
| Generic.Remcos.3C079F21 | AV |
| Generic.Remcos.3CB4D1D5 | AV |
| Generic.Remcos.3CC08E36 | AV |
| Generic.Remcos.3CDD2CAE | AV |
| Generic.Remcos.3D092F0F | AV |
| Generic.Remcos.3E122250 | AV |
| Generic.Remcos.3E367326 | AV |
| Generic.Remcos.3E8E2BD6 | AV |
| Generic.Remcos.3EA04298 | AV |
| Generic.Remcos.41E43552 | AV |
| Generic.Remcos.4254337F | AV |
| Generic.Remcos.42D74D99 | AV |
| Generic.Remcos.43547A9E | AV |
| Generic.Remcos.439AE01D | AV |
| Generic.Remcos.440B90AF | AV |
| Generic.Remcos.44548711 | AV |
| Generic.Remcos.44AD19B3 | AV |
| Generic.Remcos.45B602A3 | AV |
| Generic.Remcos.46C7D2EB | AV |
| Generic.Remcos.46D6568E | AV |
| Generic.Remcos.46DD9D1D | AV |
| Generic.Remcos.471D7A5A | AV |
| Generic.Remcos.47D8FEDF | AV |
| Generic.Remcos.487B3DA9 | AV |
| Generic.Remcos.48A09CFF | AV |
| Generic.Remcos.4960C102 | AV |
| Generic.Remcos.4AD1692F | AV |
| Generic.Remcos.4B4FCAEE | AV |
| Generic.Remcos.4BD68A03 | AV |
| Generic.Remcos.4D4597E7 | AV |
| Generic.Remcos.4E8EFF41 | AV |
| Generic.Remcos.4E98971F | AV |
| Generic.Remcos.4F506006 | AV |
| Generic.Remcos.504DCEC3 | AV |
| Generic.Remcos.504E373B | AV |
| Generic.Remcos.50F06FC0 | AV |
| Generic.Remcos.5123D173 | AV |
| Generic.Remcos.51685DFC | AV |
| Generic.Remcos.519BAE02 | AV |
| Generic.Remcos.51C19ACA | AV |
| Generic.Remcos.5234AC2A | AV |
| Generic.Remcos.52C31CA9 | AV |
| Generic.Remcos.52E20A20 | AV |
| Generic.Remcos.53192B70 | AV |
| Generic.Remcos.53A2354E | AV |
| Generic.Remcos.54958801 | AV |
| Generic.Remcos.561A793C | AV |
| Generic.Remcos.587F6318 | AV |
| Generic.Remcos.58900041 | AV |
| Generic.Remcos.590180B2 | AV |
| Generic.Remcos.59022B69 | AV |
| Generic.Remcos.59A72523 | AV |
| Generic.Remcos.59D37AC0 | AV |
| Generic.Remcos.5A1EB938 | AV |
| Generic.Remcos.5B9DDF20 | AV |
| Generic.Remcos.5CF3E759 | AV |
| Generic.Remcos.5DC4ABD9 | AV |
| Generic.Remcos.5E37B98D | AV |
| Generic.Remcos.5EABA2BE | AV |
| Generic.Remcos.5ED501E3 | AV |
| Generic.Remcos.5EE5FD75 | AV |
| Generic.Remcos.5F251664 | AV |
| Generic.Remcos.5F2895B9 | AV |
| Generic.Remcos.5FB48E8A | AV |
| Generic.Remcos.60D1F96F | AV |
| Generic.Remcos.611D0D08 | AV |
| Generic.Remcos.6164C783 | AV |
| Generic.Remcos.62DC08A5 | AV |
| Generic.Remcos.63857A3E | AV |
| Generic.Remcos.639F16A9 | AV |
| Generic.Remcos.65387562 | AV |
| Generic.Remcos.655412FE | AV |
| Generic.Remcos.6570B8D6 | AV |
| Generic.Remcos.65F4A6DA | AV |
| Generic.Remcos.661904CF | AV |
| Generic.Remcos.66718829 | AV |
| Generic.Remcos.670C5719 | AV |
| Generic.Remcos.681E81B0 | AV |
| Generic.Remcos.682152DC | AV |
| Generic.Remcos.68550D3F | AV |
| Generic.Remcos.689B56A3 | AV |
| Generic.Remcos.691EB3BF | AV |
| Generic.Remcos.697FF55D | AV |
| Generic.Remcos.6A360816 | AV |
| Generic.Remcos.6BF2322F | AV |
| Generic.Remcos.6C82CD4E | AV |
| Generic.Remcos.6CA5A8AC | AV |
| Generic.Remcos.6D913E21 | AV |
| Generic.Remcos.6DD6E263 | AV |
| Generic.Remcos.6E7B903A | AV |
| Generic.Remcos.7031F55B | AV |
| Generic.Remcos.70ADEE68 | AV |
| Generic.Remcos.716C1AC5 | AV |
| Generic.Remcos.7236A3E6 | AV |
| Generic.Remcos.73CE8F39 | AV |
| Generic.Remcos.73E495F2 | AV |
| Generic.Remcos.751F9208 | AV |
| Generic.Remcos.75421D51 | AV |
| Generic.Remcos.75535057 | AV |
| Generic.Remcos.76114B49 | AV |
| Generic.Remcos.76FDFBE5 | AV |
| Generic.Remcos.772FB501 | AV |
| Generic.Remcos.77398E53 | AV |
| Generic.Remcos.775BEAE2 | AV |
| Generic.Remcos.77630FB5 | AV |
| Generic.Remcos.778898F4 | AV |
| Generic.Remcos.7795B17E | AV |
| Generic.Remcos.781E61DA | AV |
| Generic.Remcos.7892E91E | AV |
| Generic.Remcos.78E072E5 | AV |
| Generic.Remcos.791B8B47 | AV |
| Generic.Remcos.798102D6 | AV |
| Generic.Remcos.7A2F53FE | AV |
| Generic.Remcos.7A8748F1 | AV |
| Generic.Remcos.7AF38F39 | AV |
| Generic.Remcos.7B0258C1 | AV |
| Generic.Remcos.7B248F8A | AV |
| Generic.Remcos.7BF7D344 | AV |
| Generic.Remcos.7C274E9F | AV |
| Generic.Remcos.7CBB55AC | AV |
| Generic.Remcos.7CC0F24D | AV |
| Generic.Remcos.7CEAE886 | AV |
| Generic.Remcos.7E6DC6AF | AV |
| Generic.Remcos.7ECADC40 | AV |
| Generic.Remcos.7FDF1EB2 | AV |
| Generic.Remcos.8095D395 | AV |
| Generic.Remcos.8174C2EE | AV |
| Generic.Remcos.82282363 | AV |
| Generic.Remcos.82477FF3 | AV |
| Generic.Remcos.830342B2 | AV |
| Generic.Remcos.83276B83 | AV |
| Generic.Remcos.83836DA1 | AV |
| Generic.Remcos.8485F61F | AV |
| Generic.Remcos.850A885F | AV |
| Generic.Remcos.857ED7BC | AV |
| Generic.Remcos.877A41D1 | AV |
| Generic.Remcos.87CB3B84 | AV |
| Generic.Remcos.8856E2C9 | AV |
| Generic.Remcos.88A0BF4A | AV |
| Generic.Remcos.88CFFC05 | AV |
| Generic.Remcos.88F29619 | AV |
| Generic.Remcos.896FB897 | AV |
| Generic.Remcos.8A0AD7D0 | AV |
| Generic.Remcos.8A0D8BA8 | AV |
| Generic.Remcos.8A465CB0 | AV |
| Generic.Remcos.8A700070 | AV |
| Generic.Remcos.8AC38BA3 | AV |
| Generic.Remcos.8C0D3FC6 | AV |
| Generic.Remcos.8C5417CB | AV |
| Generic.Remcos.8C7E1258 | AV |
| Generic.Remcos.8C803FE2 | AV |
| Generic.Remcos.8C8AD6B9 | AV |
| Generic.Remcos.8CF128A4 | AV |
| Generic.Remcos.8D6134D6 | AV |
| Generic.Remcos.8D8E7C0F | AV |
| Generic.Remcos.8E127BDB | AV |
| Generic.Remcos.8E2510F9 | AV |
| Generic.Remcos.8FB4860C | AV |
| Generic.Remcos.901BEB23 | AV |
| Generic.Remcos.911D11ED | AV |
| Generic.Remcos.91583865 | AV |
| Generic.Remcos.9186A1BD | AV |
| Generic.Remcos.91BAC040 | AV |
| Generic.Remcos.925227B1 | AV |
| Generic.Remcos.92F4C431 | AV |
| Generic.Remcos.93E20002 | AV |
| Generic.Remcos.93FCAC50 | AV |
| Generic.Remcos.94816F1C | AV |
| Generic.Remcos.95CD6C7E | AV |
| Generic.Remcos.97550BDE | AV |
| Generic.Remcos.97D19B84 | AV |
| Generic.Remcos.97E8D305 | AV |
| Generic.Remcos.98079E8F | AV |
| Generic.Remcos.986CC79B | AV |
| Generic.Remcos.994C5016 | AV |
| Generic.Remcos.9998221D | AV |
| Generic.Remcos.9A046F82 | AV |
| Generic.Remcos.9B1F0C34 | AV |
| Generic.Remcos.9ED0186F | AV |
| Generic.Remcos.9EEC0772 | AV |
| Generic.Remcos.9FEF6BAB | AV |
| Generic.Remcos.A.1.0D19711B | AV |
| Generic.Remcos.A.1.53908EA3 | AV |
| Generic.Remcos.A.1.717B3CC7 | AV |
| Generic.Remcos.A.1.9D45B7F4 | AV |
| Generic.Remcos.A.1.B02FB9FF | AV |
| Generic.Remcos.A.1.E64C4F7C | AV |
| Generic.Remcos.A0491749 | AV |
| Generic.Remcos.A0F693E8 | AV |
| Generic.Remcos.A10D40DF | AV |
| Generic.Remcos.A1A06B28 | AV |
| Generic.Remcos.A1A32C6E | AV |
| Generic.Remcos.A28ECA3F | AV |
| Generic.Remcos.A2BACAC7 | AV |
| Generic.Remcos.A306EC2D | AV |
| Generic.Remcos.A3F764DD | AV |
| Generic.Remcos.A3F82ECF | AV |
| Generic.Remcos.A3FE7FD7 | AV |
| Generic.Remcos.A43F4462 | AV |
| Generic.Remcos.A44B1B81 | AV |
| Generic.Remcos.A44FF3C4 | AV |
| Generic.Remcos.A458A867 | AV |
| Generic.Remcos.A58BCD06 | AV |
| Generic.Remcos.A5A1D7CD | AV |
| Generic.Remcos.A7AA505C | AV |
| Generic.Remcos.A8263FDF | AV |
| Generic.Remcos.A8288490 | AV |
| Generic.Remcos.A8863BF1 | AV |
| Generic.Remcos.A886D2EB | AV |
| Generic.Remcos.A9ACD8CB | AV |
| Generic.Remcos.AA85B072 | AV |
| Generic.Remcos.AAC0BEFB | AV |
| Generic.Remcos.ACBBB032 | AV |
| Generic.Remcos.ACCFEFD1 | AV |
| Generic.Remcos.AE022A35 | AV |
| Generic.Remcos.B01ED0DD | AV |
| Generic.Remcos.B15563BE | AV |
| Generic.Remcos.B1C9788D | AV |
| Generic.Remcos.B1F56790 | AV |
| Generic.Remcos.B31E9295 | AV |
| Generic.Remcos.B33080FC | AV |
| Generic.Remcos.B3C1080C | AV |
| Generic.Remcos.B417012A | AV |
| Generic.Remcos.B4F8A043 | AV |
| Generic.Remcos.B5CFD4CD | AV |
| Generic.Remcos.B5D9E7FF | AV |
| Generic.Remcos.B72E6970 | AV |
| Generic.Remcos.B789B8DD | AV |
| Generic.Remcos.B7DF6A0D | AV |
| Generic.Remcos.B8878916 | AV |
| Generic.Remcos.B8EC6F12 | AV |
| Generic.Remcos.BAA185DF | AV |
| Generic.Remcos.BB31A3BF | AV |
| Generic.Remcos.BC734A29 | AV |
| Generic.Remcos.BC8DDCE3 | AV |
| Generic.Remcos.BE07F6EF | AV |
| Generic.Remcos.BF035285 | AV |
| Generic.Remcos.BF3AB762 | AV |
| Generic.Remcos.BF7F288B | AV |
| Generic.Remcos.C032E6F1 | AV |
| Generic.Remcos.C095375C | AV |
| Generic.Remcos.C226877F | AV |
| Generic.Remcos.C3164A97 | AV |
| Generic.Remcos.C3A5B078 | AV |
| Generic.Remcos.C3BD7F60 | AV |
| Generic.Remcos.C4F246D9 | AV |
| Generic.Remcos.C61518DB | AV |
| Generic.Remcos.C6614738 | AV |
| Generic.Remcos.C6AA033E | AV |
| Generic.Remcos.C6AF1CA4 | AV |
| Generic.Remcos.C7293439 | AV |
| Generic.Remcos.C7E8F410 | AV |
| Generic.Remcos.C8FC3205 | AV |
| Generic.Remcos.C9A844C4 | AV |
| Generic.Remcos.C9DC1B27 | AV |
| Generic.Remcos.CA7EB87D | AV |
| Generic.Remcos.CA87D022 | AV |
| Generic.Remcos.CAE3ABA0 | AV |
| Generic.Remcos.CB7C8030 | AV |
| Generic.Remcos.CBFA1167 | AV |
| Generic.Remcos.CD2A435C | AV |
| Generic.Remcos.CD7E8213 | AV |
| Generic.Remcos.CE7D7610 | AV |
| Generic.Remcos.CE91EC8B | AV |
| Generic.Remcos.CFEFA507 | AV |
| Generic.Remcos.D041EF8E | AV |
| Generic.Remcos.D05B6F30 | AV |
| Generic.Remcos.D08BCA0E | AV |
| Generic.Remcos.D13EDE79 | AV |
| Generic.Remcos.D18005CE | AV |
| Generic.Remcos.D19F0B56 | AV |
| Generic.Remcos.D1C8B226 | AV |
| Generic.Remcos.D1EB54B5 | AV |
| Generic.Remcos.D2D0C8AF | AV |
| Generic.Remcos.D3F7A34F | AV |
| Generic.Remcos.D47BEF98 | AV |
| Generic.Remcos.D503EA25 | AV |
| Generic.Remcos.D65BDB5E | AV |
| Generic.Remcos.D66053F3 | AV |
| Generic.Remcos.D671C195 | AV |
| Generic.Remcos.D6A6A319 | AV |
| Generic.Remcos.D8134DF7 | AV |
| Generic.Remcos.D8404F8B | AV |
| Generic.Remcos.D87C2E76 | AV |
| Generic.Remcos.D9D8EF8F | AV |
| Generic.Remcos.DA06239B | AV |
| Generic.Remcos.DAD6EC19 | AV |
| Generic.Remcos.DAF4DB9F | AV |
| Generic.Remcos.DB55DB1E | AV |
| Generic.Remcos.DBBB6411 | AV |
| Generic.Remcos.DBF5DF30 | AV |
| Generic.Remcos.DC6CF2A9 | AV |
| Generic.Remcos.DD3738F6 | AV |
| Generic.Remcos.DD580120 | AV |
| Generic.Remcos.DD7BE0D7 | AV |
| Generic.Remcos.DDDC317A | AV |
| Generic.Remcos.DE5608AA | AV |
| Generic.Remcos.DEA7805A | AV |
| Generic.Remcos.DFDAAE87 | AV |
| Generic.Remcos.E04DB332 | AV |
| Generic.Remcos.E078B8EE | AV |
| Generic.Remcos.E0AA6B5E | AV |
| Generic.Remcos.E1858BF1 | AV |
| Generic.Remcos.E1B3AFEB | AV |
| Generic.Remcos.E1CE0B39 | AV |
| Generic.Remcos.E1DB8C8D | AV |
| Generic.Remcos.E1EBC9BD | AV |
| Generic.Remcos.E2058B53 | AV |
| Generic.Remcos.E28BA73B | AV |
| Generic.Remcos.E426EF1F | AV |
| Generic.Remcos.E4E023D1 | AV |
| Generic.Remcos.E67EAAF8 | AV |
| Generic.Remcos.E686D021 | AV |
| Generic.Remcos.E6A64FC1 | AV |
| Generic.Remcos.E71CC16A | AV |
| Generic.Remcos.E720D4E6 | AV |
| Generic.Remcos.E7D15C16 | AV |
| Generic.Remcos.E7E3CC66 | AV |
| Generic.Remcos.E87D2232 | AV |
| Generic.Remcos.E89D88F9 | AV |
| Generic.Remcos.EB747A4E | AV |
| Generic.Remcos.ECE3C3C0 | AV |
| Generic.Remcos.EDAC4982 | AV |
| Generic.Remcos.EDD83FF1 | AV |
| Generic.Remcos.EE788E4E | AV |
| Generic.Remcos.EF543A59 | AV |
| Generic.Remcos.F0D354EA | AV |
| Generic.Remcos.F2C32F83 | AV |
| Generic.Remcos.F3445E07 | AV |
| Generic.Remcos.F3DF664D | AV |
| Generic.Remcos.F4F3D442 | AV |
| Generic.Remcos.F53D0720 | AV |
| Generic.Remcos.F5D743E3 | AV |
| Generic.Remcos.F5FBC73D | AV |
| Generic.Remcos.F7936F24 | AV |
| Generic.Remcos.F7E730C7 | AV |
| Generic.Remcos.F81387F6 | AV |
| Generic.Remcos.F90EF45A | AV |
| Generic.Remcos.F9452C0C | AV |
| Generic.Remcos.F9A925F7 | AV |
| Generic.Remcos.F9D9373F | AV |
| Generic.Remcos.F9F7873B | AV |
| Generic.Remcos.FADDA593 | AV |
| Generic.Remcos.FB343A4B | AV |
| Generic.Remcos.FB48984A | AV |
| Generic.Remcos.FD55B37E | AV |
| Generic.Remcos.FD7E28B3 | AV |
| Generic.Remcos.FE733716 | AV |
| Generic.Remcos.FF179B74 | AV |
| GenPack:Generic.Remcos.18BE308D | AV |
| GenPack:Generic.Remcos.7869E776 | AV |
| GT:JS.Remcos.1.02246478 | AV |
| GT:JS.Remcos.1.02D9AEEE | AV |
| GT:JS.Remcos.1.0425B0DF | AV |
| GT:JS.Remcos.1.0588612F | AV |
| GT:JS.Remcos.1.06F1437B | AV |
| GT:JS.Remcos.1.086E7C53 | AV |
| GT:JS.Remcos.1.09360390 | AV |
| GT:JS.Remcos.1.0C4666D6 | AV |
| GT:JS.Remcos.1.10723E96 | AV |
| GT:JS.Remcos.1.10DD9469 | AV |
| GT:JS.Remcos.1.110F1482 | AV |
| GT:JS.Remcos.1.126940F6 | AV |
| GT:JS.Remcos.1.12F0FC98 | AV |
| GT:JS.Remcos.1.1512856F | AV |
| GT:JS.Remcos.1.1822759E | AV |
| GT:JS.Remcos.1.184437FC | AV |
| GT:JS.Remcos.1.1AC41F6C | AV |
| GT:JS.Remcos.1.1B0295C5 | AV |
| GT:JS.Remcos.1.1B943062 | AV |
| GT:JS.Remcos.1.1BD561B2 | AV |
| GT:JS.Remcos.1.1C4EC8ED | AV |
| GT:JS.Remcos.1.1C630D2E | AV |
| GT:JS.Remcos.1.1CEB60A7 | AV |
| GT:JS.Remcos.1.1ED0825A | AV |
| GT:JS.Remcos.1.20627E6E | AV |
| GT:JS.Remcos.1.21D27C2C | AV |
| GT:JS.Remcos.1.24DD6425 | AV |
| GT:JS.Remcos.1.25C7DB06 | AV |
| GT:JS.Remcos.1.262A4024 | AV |
| GT:JS.Remcos.1.265E15B5 | AV |
| GT:JS.Remcos.1.2CB6874A | AV |
| GT:JS.Remcos.1.2F04F9B8 | AV |
| GT:JS.Remcos.1.3223857B | AV |
| GT:JS.Remcos.1.323B151A | AV |
| GT:JS.Remcos.1.3590C5BC | AV |
| GT:JS.Remcos.1.36AB3A58 | AV |
| GT:JS.Remcos.1.386A0636 | AV |
| GT:JS.Remcos.1.3C2708D4 | AV |
| GT:JS.Remcos.1.3E51D973 | AV |
| GT:JS.Remcos.1.3F9D0683 | AV |
| GT:JS.Remcos.1.3FEFEA37 | AV |
| GT:JS.Remcos.1.4297F6EB | AV |
| GT:JS.Remcos.1.42AD669C | AV |
| GT:JS.Remcos.1.4425AE60 | AV |
| GT:JS.Remcos.1.46F00C03 | AV |
| GT:JS.Remcos.1.4756CC6B | AV |
| GT:JS.Remcos.1.4AD239D6 | AV |
| GT:JS.Remcos.1.4B485E0F | AV |
| GT:JS.Remcos.1.4BF4BE86 | AV |
| GT:JS.Remcos.1.4CC7F9D1 | AV |
| GT:JS.Remcos.1.4DC653FC | AV |
| GT:JS.Remcos.1.521759BF | AV |
| GT:JS.Remcos.1.53B63BD8 | AV |
| GT:JS.Remcos.1.541B0B59 | AV |
| GT:JS.Remcos.1.5436FE01 | AV |
| GT:JS.Remcos.1.547E1753 | AV |
| GT:JS.Remcos.1.558EBC55 | AV |
| GT:JS.Remcos.1.55AC9C96 | AV |
| GT:JS.Remcos.1.55EB03FB | AV |
| GT:JS.Remcos.1.57F8C9A3 | AV |
| GT:JS.Remcos.1.5928E400 | AV |
| GT:JS.Remcos.1.5B040F78 | AV |
| GT:JS.Remcos.1.5B9CB8E7 | AV |
| GT:JS.Remcos.1.5BFB5702 | AV |
| GT:JS.Remcos.1.5E94EFA5 | AV |
| GT:JS.Remcos.1.603FEBDF | AV |
| GT:JS.Remcos.1.6041762E | AV |
| GT:JS.Remcos.1.60926721 | AV |
| GT:JS.Remcos.1.6270B999 | AV |
| GT:JS.Remcos.1.65922E2F | AV |
| GT:JS.Remcos.1.665CF764 | AV |
| GT:JS.Remcos.1.69073632 | AV |
| GT:JS.Remcos.1.6BEADD5A | AV |
| GT:JS.Remcos.1.700DADFB | AV |
| GT:JS.Remcos.1.71A0BD29 | AV |
| GT:JS.Remcos.1.71BE0331 | AV |
| GT:JS.Remcos.1.74171728 | AV |
| GT:JS.Remcos.1.74CD1F0E | AV |
| GT:JS.Remcos.1.7711CF75 | AV |
| GT:JS.Remcos.1.774F9D4F | AV |
| GT:JS.Remcos.1.77DA1B1E | AV |
| GT:JS.Remcos.1.7B8343DB | AV |
| GT:JS.Remcos.1.7CA97AA5 | AV |
| GT:JS.Remcos.1.7EFC6136 | AV |
| GT:JS.Remcos.1.7FE739B1 | AV |
| GT:JS.Remcos.1.7FED5B8B | AV |
| GT:JS.Remcos.1.81C49CB1 | AV |
| GT:JS.Remcos.1.83349029 | AV |
| GT:JS.Remcos.1.89BCC746 | AV |
| GT:JS.Remcos.1.8AB2D486 | AV |
| GT:JS.Remcos.1.8B416C30 | AV |
| GT:JS.Remcos.1.9043BB38 | AV |
| GT:JS.Remcos.1.9111766C | AV |
| GT:JS.Remcos.1.9486F0D4 | AV |
| GT:JS.Remcos.1.952747F5 | AV |
| GT:JS.Remcos.1.9661D0D0 | AV |
| GT:JS.Remcos.1.96694E14 | AV |
| GT:JS.Remcos.1.97B483F3 | AV |
| GT:JS.Remcos.1.9A963915 | AV |
| GT:JS.Remcos.1.9B4F4187 | AV |
| GT:JS.Remcos.1.9CB45A01 | AV |
| GT:JS.Remcos.1.9FDE0CCA | AV |
| GT:JS.Remcos.1.A0A2451E | AV |
| GT:JS.Remcos.1.A1226717 | AV |
| GT:JS.Remcos.1.A17FCFC4 | AV |
| GT:JS.Remcos.1.A1F9B60B | AV |
| GT:JS.Remcos.1.A3B69AB8 | AV |
| GT:JS.Remcos.1.A471A697 | AV |
| GT:JS.Remcos.1.A5563358 | AV |
| GT:JS.Remcos.1.A6D093FB | AV |
| GT:JS.Remcos.1.A71EB674 | AV |
| GT:JS.Remcos.1.A7AE8376 | AV |
| GT:JS.Remcos.1.A92929E8 | AV |
| GT:JS.Remcos.1.A94EE70F | AV |
| GT:JS.Remcos.1.AA85F24C | AV |
| GT:JS.Remcos.1.ACAD3CAA | AV |
| GT:JS.Remcos.1.AE1EC376 | AV |
| GT:JS.Remcos.1.AE9DAF65 | AV |
| GT:JS.Remcos.1.AF8DB309 | AV |
| GT:JS.Remcos.1.B0027238 | AV |
| GT:JS.Remcos.1.B7746079 | AV |
| GT:JS.Remcos.1.BA04EB64 | AV |
| GT:JS.Remcos.1.BA6C2489 | AV |
| GT:JS.Remcos.1.BDCC1D8B | AV |
| GT:JS.Remcos.1.BE2E4DB6 | AV |
| GT:JS.Remcos.1.BEB51D95 | AV |
| GT:JS.Remcos.1.C007E883 | AV |
| GT:JS.Remcos.1.C0CC83DE | AV |
| GT:JS.Remcos.1.C10DC964 | AV |
| GT:JS.Remcos.1.C2141760 | AV |
| GT:JS.Remcos.1.C2D58672 | AV |
| GT:JS.Remcos.1.C3DA52D3 | AV |
| GT:JS.Remcos.1.C3EAFD2D | AV |
| GT:JS.Remcos.1.C50042F6 | AV |
| GT:JS.Remcos.1.C52FBB23 | AV |
| GT:JS.Remcos.1.C7036D81 | AV |
| GT:JS.Remcos.1.CB162887 | AV |
| GT:JS.Remcos.1.CE2ACD4A | AV |
| GT:JS.Remcos.1.CE81075C | AV |
| GT:JS.Remcos.1.D06335C5 | AV |
| GT:JS.Remcos.1.D1428527 | AV |
| GT:JS.Remcos.1.D1A5EA05 | AV |
| GT:JS.Remcos.1.D239203F | AV |
| GT:JS.Remcos.1.D4482355 | AV |
| GT:JS.Remcos.1.DAD5223F | AV |
| GT:JS.Remcos.1.DEE71695 | AV |
| GT:JS.Remcos.1.E0BCC57F | AV |
| GT:JS.Remcos.1.E147FF55 | AV |
| GT:JS.Remcos.1.E3558139 | AV |
| GT:JS.Remcos.1.E3B1E066 | AV |
| GT:JS.Remcos.1.E60532DD | AV |
| GT:JS.Remcos.1.E6112D08 | AV |
| GT:JS.Remcos.1.E6DDE2AB | AV |
| GT:JS.Remcos.1.E8D0DC50 | AV |
| GT:JS.Remcos.1.EA1AC553 | AV |
| GT:JS.Remcos.1.EB28E2F8 | AV |
| GT:JS.Remcos.1.EB341B98 | AV |
| GT:JS.Remcos.1.EB7724A6 | AV |
| GT:JS.Remcos.1.EC363695 | AV |
| GT:JS.Remcos.1.ECEC3B75 | AV |
| GT:JS.Remcos.1.ED21DBFF | AV |
| GT:JS.Remcos.1.F361D88B | AV |
| GT:JS.Remcos.1.F4DD0039 | AV |
| GT:JS.Remcos.1.F5B590BF | AV |
| GT:JS.Remcos.1.F805FA2A | AV |
| GT:JS.Remcos.1.F940B05D | AV |
| GT:JS.Remcos.1.FB0E1CEC | AV |
| GT:JS.Remcos.1.FC5B8361 | AV |
| GT:JS.Remcos.1.FCEC50D7 | AV |
| GT:JS.Remcos.1.FD1989F7 | AV |
| GT:JS.Remcos.1.FDD13FA4 | AV |
| GT:VB.Remcos.2.108776E5 | AV |
| GT:VB.Remcos.2.3C0CCD94 | AV |
| GT:VB.Remcos.2.45E6A93C | AV |
| GT:VB.Remcos.2.4B874D8C | AV |
| GT:VB.Remcos.2.5EC79433 | AV |
| GT:VB.Remcos.2.8B001951 | AV |
| GT:VB.Remcos.2.8CDE0DA2 | AV |
| GT:VB.Remcos.2.A2333A2C | AV |
| GT:VB.Remcos.2.A81EACE1 | AV |
| GT:VB.Remcos.2.B581B4EF | AV |
| GT:VB.Remcos.2.B72E4DF8 | AV |
| GT:VB.Remcos.2.BD748B33 | AV |
| GT:VB.Remcos.2.BDB84847 | AV |
| GT:VB.Remcos.2.CE4F68C0 | AV |
| GT:VB.Remcos.2.D0F0EA3A | AV |
| GT:VB.Remcos.2.DA9FEF01 | AV |
| GT:VB.Remcos.2.F5C337B4 | AV |
| GT:VB.Remcos.2.F9B5ECB1 | AV |
| IL:Trojan.RemcosRAT.13 | AV |
| IL:Trojan.RemcosRAT.228 | AV |
| IL:Trojan.RemcosRAT.249 | AV |
| IL:Trojan.RemcosRAT.251 | AV |
| JS:Trojan.RemcosRAT.59 | AV |
| JS:Trojan.RemcosRAT.60 | AV |
| Script-AutoIt.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Script-AutoIt.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Script-BAT.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Script-BAT.Downloader.Remcos | ATP Sandbox Adv. Heuristics |
| Script-JS.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Script-JS.Downloader.Remcos | ATP Sandbox Adv. Heuristics |
| Script-JS.Downloader.Remcosrat | ATP Sandbox Adv. Heuristics |
| Script-JS.Downloader.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Script-JS.Dropper.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Script-JS.Malware.Remcos | ATP Sandbox Adv. Heuristics |
| Script-JS.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Script-PowerShell.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Script-PowerShell.Downloader.Remcos | ATP Sandbox Adv. Heuristics |
| Script-PowerShell.Downloader.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Script-PowerShell.Dropper.Remcos | ATP Sandbox Adv. Heuristics |
| Script-PowerShell.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Script-PowerShell.Trojan.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Script-WScript.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Script-WScript.Downloader.Remcos | ATP Sandbox Adv. Heuristics |
| Script-WScript.Downloader.Remcosrat | ATP Sandbox Adv. Heuristics |
| Script-WScript.Downloader.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Script-WScript.Dropper.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Script-WScript.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Script-WScript.Trojan.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Script.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Script.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Shortcut.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Shortcut.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Trojan.RemcosRAT.1 | AV |
| Trojan.RemcosRAT.209 | AV |
| Trojan.RemcosRAT.209:740E6 | ATP Sandbox Adv. Heuristics |
| Trojan.RemcosRAT.216 | AV |
| Trojan.RemcosRAT.218 | AV |
| Win32.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Win32.Downloader.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Win32.Dropper.Remcos | ATP Sandbox Adv. Heuristics |
| Win32.Dropper.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Win32.Exploit.Remcos | ATP Sandbox Adv. Heuristics |
| Win32.Infostealer.Remcos | ATP Sandbox Adv. Heuristics |
| Win32.Malware.Remcos | ATP Sandbox Adv. Heuristics |
| Win32.Ransomware.Remcos | ATP Sandbox Adv. Heuristics |
| Win32.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
| Win32.Trojan.Remcosrat | ATP Sandbox Adv. Heuristics |
| Win32.Trojan.RemcosRAT | ATP Sandbox Adv. Heuristics |
| Win64.Backdoor.Remcos | ATP Sandbox Adv. Heuristics |
| Win64.Trojan.Remcos | ATP Sandbox Adv. Heuristics |
Related IPS Signatures
| Signature Name | Engine |
|---|---|
| MALWARE-CNC Remcos.APT.bits traffic detected | IPS-SWG |
| MALWARE-OTHER Win.Trojan.Remcos variant download attempt | IPS-SWG |
Related blogs
Netskope Threat Labs Stats for March 2024
·4 min read
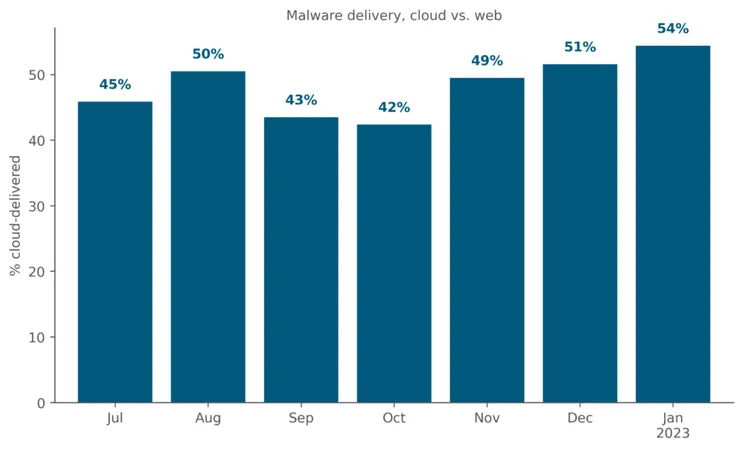
Netskope Threat Labs Stats for January 2023
·5 min read