Description
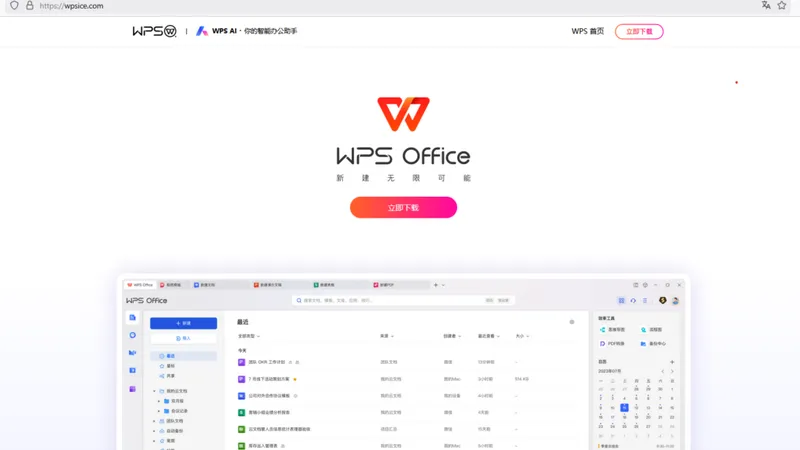
SainBox is a remote access trojan hidden within fake DeepSeek applications that includes rootkit delivery capabilities to conceal its presence. Its lures imitate popular artificial intelligence tools, and users who install the trojanized applications grant operators hidden control of their systems. Researchers documented the campaign's installer, implant, and rootkit component.
Stats
- First seen
- January 2025
- Last seen
- October 2026
Alert name variants
| Alert Name |
|---|
| Win32.Backdoor.Sainbox |