Description
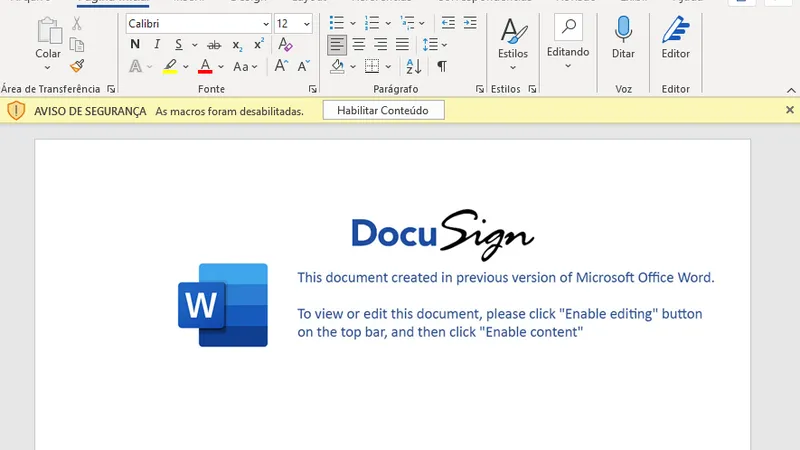
Squirrelwaffle is a malware loader distributed as malicious Office documents in spam campaigns. When a recipient enables macros in the document, a Visual Basic script downloads and executes further malicious files, giving its operators an initial foothold and a channel for delivering additional malware. Its operators also used DocuSign branded lures to trick users into enabling macros.
Stats
- First seen
- March 2022
- Last seen
- September 2026
Also known as
SquirrelWaffle
MITRE ATT&CK techniques
21 techniques across 7 tactics.
TA0002 Execution
TA0005 Stealth
TA0007 Discovery
TA0011 Command and Control
TA0010 Exfiltration
- T1041Exfiltration Over C2 Channel
Alert name variants
| Alert Name |
|---|
| Document-Excel.Trojan.Squirrelwaffle |
| Document-Word.Trojan.Squirrelwaffle |
| Script-WScript.Trojan.Squirrelwaffle |
| Win32.Dropper.SquirrelWaffle |
Related IPS Signatures
| Signature Name |
|---|
| MALWARE-CNC Doc.Dropper.SquirrelWaffle download attempt |