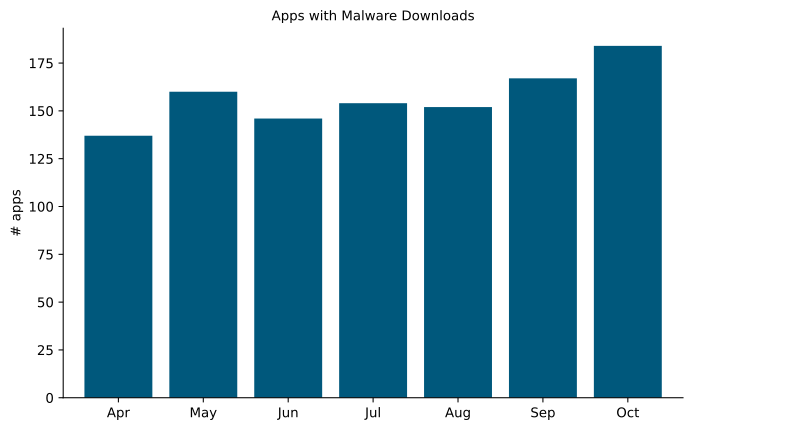
Description
Upatre is a downloader used to distribute other payloads such as Locky and Dridex during large spam campaigns in the mid 2010s. Its small size and rapid code rotation let it slip past signature defenses while its operators cycled delivery infrastructure. Although the original campaigns faded, the family exemplifies the lightweight, disposable downloader model that still underpins malware distribution today.
Stats
- First seen
- February 2022
- Last seen
- October 2026
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Downloader.Upatre |
| Document-Word.Downloader.Upatre |
| Email.Downloader.Upatre |
| Gen:Variant.Downloader.Upatre.3 |
| GenPack:Trojan.Upatre.ET |
| GenPack:Trojan.Upatre.EW |
| Linux.Downloader.Upatre |
| Trojan.Downloader.Upatre.A |
| Trojan.Downloader.Upatre.AB |
| Trojan.Downloader.Upatre.AE |