Description
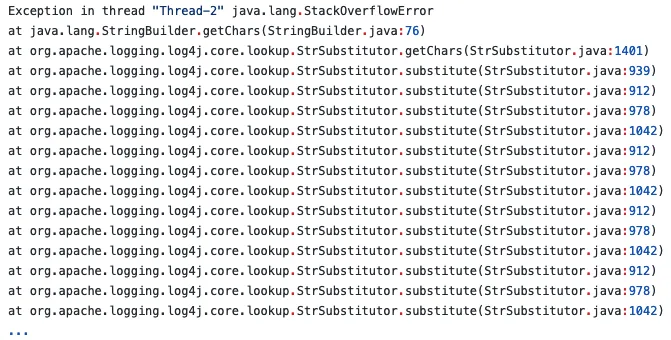
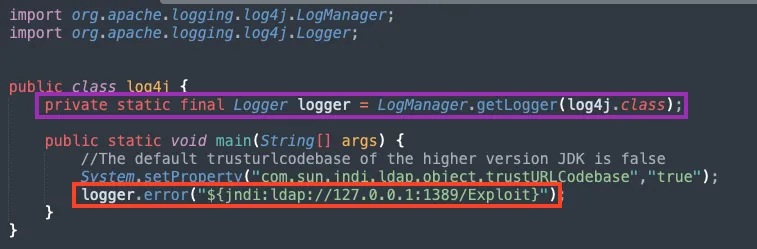
Detects an attempt to exploit CVE-2021-44228, CVE-2021-44832, CVE-2021-45046, and 2 others, a remote code execution flaw that can run code on the server in Apache Log4j logging. The flaw, known as Log4Shell, saw mass exploitation within hours of disclosure and reached nearly every Java service that logged untrusted text.
CVEs
Related malware families
Related blogs