Description
Dridex has been around since at least 2015 and has had its botnet infrastructure taken down multiple times, but it continues to re-emerge with new features and new infrastructure. The banking trojan steals credentials through web injects and form grabbing, and its operators rent out the botnet as a loader for ransomware and other payloads. Its resilience comes from a modular design and a criminal organization, Evil Corp, that repeatedly rebuilds its delivery chains after disruption.
Stats
- First seen
- January 2022
- Last seen
- October 2026
MITRE ATT&CK techniques
15 techniques across 5 tactics.
Associated groups
Alert name variants
| Alert Name | Engine |
|---|---|
| Binary.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Binary.Trojan.Dridex | ATP Sandbox Adv. Heuristics |
| DeepScan:Generic.Dridex.Y.D1888308 | AV |
| Document-Excel.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Document-Excel.Trojan.Dridex | ATP Sandbox Adv. Heuristics |
| Document-Office.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Document-Word.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Document-Word.Trojan.Dridex | ATP Sandbox Adv. Heuristics |
| Email-MIME.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Gen:Variant.Application.Jaik.Dridex.39019 | AV |
| Gen:Variant.Dridex.13 | AV |
| Gen:Variant.Dridex.30 | AV |
| Gen:Variant.Dridex.5 | AV |
| Gen:Variant.Dridex.50 | AV |
| Gen:Variant.Dridex.54 | AV |
| Gen:Variant.Midie.Dridex.78697 | AV |
| Gen:Variant.Mikey.Dridex.118488 | AV |
| Generic.Dacic.1.Dridex.A.6CC572F6 | AV |
| GT:VB.Dridex.5.00BDEEDE | AV |
| GT:VB.Dridex.5.02AD00F7 | AV |
| GT:VB.Dridex.5.03991B48 | AV |
| GT:VB.Dridex.5.053D5832 | AV |
| GT:VB.Dridex.5.062D0011 | AV |
| GT:VB.Dridex.5.081BF4DA | AV |
| GT:VB.Dridex.5.09E09BA1 | AV |
| GT:VB.Dridex.5.0A089E23 | AV |
| GT:VB.Dridex.5.0B78D06D | AV |
| GT:VB.Dridex.5.0BD37F61 | AV |
| GT:VB.Dridex.5.0D2DFB74 | AV |
| GT:VB.Dridex.5.0E718163 | AV |
| GT:VB.Dridex.5.1103B39A | AV |
| GT:VB.Dridex.5.1103B39A:EBA84 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.113DB985 | AV |
| GT:VB.Dridex.5.1A8DBEF4 | AV |
| GT:VB.Dridex.5.1A8DBEF4:85550 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.1B473027 | AV |
| GT:VB.Dridex.5.1B473027:407E6 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.2096B13E | AV |
| GT:VB.Dridex.5.20BB8CDD | AV |
| GT:VB.Dridex.5.22847738 | AV |
| GT:VB.Dridex.5.228F6DD0 | AV |
| GT:VB.Dridex.5.24F92994 | AV |
| GT:VB.Dridex.5.2555FE2C | AV |
| GT:VB.Dridex.5.2557CA8D | AV |
| GT:VB.Dridex.5.25B5944D | AV |
| GT:VB.Dridex.5.28AB0F28 | AV |
| GT:VB.Dridex.5.28D38440 | AV |
| GT:VB.Dridex.5.2D98A06F | AV |
| GT:VB.Dridex.5.32FA1B12 | AV |
| GT:VB.Dridex.5.34C8130B | AV |
| GT:VB.Dridex.5.35FD733F | AV |
| GT:VB.Dridex.5.3D178E21 | AV |
| GT:VB.Dridex.5.3D5548A9 | AV |
| GT:VB.Dridex.5.40685C73 | AV |
| GT:VB.Dridex.5.42702391 | AV |
| GT:VB.Dridex.5.43CBC7FC | AV |
| GT:VB.Dridex.5.43DA37A7 | AV |
| GT:VB.Dridex.5.440EA819 | AV |
| GT:VB.Dridex.5.445805D8 | AV |
| GT:VB.Dridex.5.445805D8:1BB22 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.445805D8:35E44 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.445805D8:6C39F | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.445805D8:BADD7 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.445805D8:FA68C | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.4F48278B | AV |
| GT:VB.Dridex.5.53E1E045 | AV |
| GT:VB.Dridex.5.551922BA | AV |
| GT:VB.Dridex.5.5A6411DB | AV |
| GT:VB.Dridex.5.5AD21F40 | AV |
| GT:VB.Dridex.5.5E0AC4FD | AV |
| GT:VB.Dridex.5.618055C0 | AV |
| GT:VB.Dridex.5.63B920EE | AV |
| GT:VB.Dridex.5.68388C29 | AV |
| GT:VB.Dridex.5.6C8888F7 | AV |
| GT:VB.Dridex.5.6FBD7052 | AV |
| GT:VB.Dridex.5.74356A21 | AV |
| GT:VB.Dridex.5.7435DCF0 | AV |
| GT:VB.Dridex.5.7567241E | AV |
| GT:VB.Dridex.5.75A8B65D | AV |
| GT:VB.Dridex.5.7667D79A | AV |
| GT:VB.Dridex.5.7721E7B0 | AV |
| GT:VB.Dridex.5.78567888 | AV |
| GT:VB.Dridex.5.79841A12 | AV |
| GT:VB.Dridex.5.7A439A3B | AV |
| GT:VB.Dridex.5.7B422363 | AV |
| GT:VB.Dridex.5.7C35716E | AV |
| GT:VB.Dridex.5.830A6419 | AV |
| GT:VB.Dridex.5.83567794 | AV |
| GT:VB.Dridex.5.88B60A7D | AV |
| GT:VB.Dridex.5.893AB377 | AV |
| GT:VB.Dridex.5.89BA7EE9 | AV |
| GT:VB.Dridex.5.8EDB07BC | AV |
| GT:VB.Dridex.5.8F02E187 | AV |
| GT:VB.Dridex.5.8F0650EC | AV |
| GT:VB.Dridex.5.8F2D825C | AV |
| GT:VB.Dridex.5.8FDADA24 | AV |
| GT:VB.Dridex.5.8FDADA24:AF5D3 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.915021E6 | AV |
| GT:VB.Dridex.5.92BE2F77 | AV |
| GT:VB.Dridex.5.92BE2F77:28DFA | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.92D868CC | AV |
| GT:VB.Dridex.5.9476CC72 | AV |
| GT:VB.Dridex.5.9746A5B7 | AV |
| GT:VB.Dridex.5.9B32A7AB | AV |
| GT:VB.Dridex.5.9FBEEAC2 | AV |
| GT:VB.Dridex.5.9FBEEAC2:0B4D6 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.9FBEEAC2:0E22F | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.9FBEEAC2:1C859 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.9FBEEAC2:3D8C7 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.9FBEEAC2:AA5FE | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.9FBEEAC2:E24E4 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.9FBEEAC2:E4F24 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.9FBEEAC2:EDD58 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.A06D2B4F | AV |
| GT:VB.Dridex.5.A2974CF9 | AV |
| GT:VB.Dridex.5.A41BFA50 | AV |
| GT:VB.Dridex.5.A51A51D7 | AV |
| GT:VB.Dridex.5.A6982853 | AV |
| GT:VB.Dridex.5.A7AA12F1 | AV |
| GT:VB.Dridex.5.A7AA12F1:0CFE1 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.A7AA12F1:F4698 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.A81780F6 | AV |
| GT:VB.Dridex.5.A81780F6:02B5E | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.A81780F6:3CBE7 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.A81780F6:414EA | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.A81780F6:D2ACD | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.A91937AA | AV |
| GT:VB.Dridex.5.AC7A5FAB | AV |
| GT:VB.Dridex.5.ACDD2EE3 | AV |
| GT:VB.Dridex.5.ACDEC421 | AV |
| GT:VB.Dridex.5.AFCF6EAE | AV |
| GT:VB.Dridex.5.B7AA13C3 | AV |
| GT:VB.Dridex.5.B7E0F06B | AV |
| GT:VB.Dridex.5.B82F92FA | AV |
| GT:VB.Dridex.5.BC78D97D | AV |
| GT:VB.Dridex.5.BC9DAE06 | AV |
| GT:VB.Dridex.5.BEA46348 | AV |
| GT:VB.Dridex.5.C142B45A | AV |
| GT:VB.Dridex.5.C436F699 | AV |
| GT:VB.Dridex.5.C7EFB29A | AV |
| GT:VB.Dridex.5.C7EFB29A:0F26C | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:154EB | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:17D46 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:2F87A | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:38C1A | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:4A7E9 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:552F0 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:6996B | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:93319 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:AF034 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:C314C | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:CDD8A | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:EA9CB | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:EC004 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:EC24D | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C7EFB29A:FB7EC | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.C8DFA87C | AV |
| GT:VB.Dridex.5.C8DFA87C:4BE0B | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.CA7D21F9 | AV |
| GT:VB.Dridex.5.CE14ADBE | AV |
| GT:VB.Dridex.5.CEFD1F8C | AV |
| GT:VB.Dridex.5.CFBA6AFD | AV |
| GT:VB.Dridex.5.D35621A8 | AV |
| GT:VB.Dridex.5.D670FFBB | AV |
| GT:VB.Dridex.5.D829C987 | AV |
| GT:VB.Dridex.5.D8CB6576 | AV |
| GT:VB.Dridex.5.DC8B9577 | AV |
| GT:VB.Dridex.5.DEFAB3B7 | AV |
| GT:VB.Dridex.5.E1D6B662 | AV |
| GT:VB.Dridex.5.E35E705F | AV |
| GT:VB.Dridex.5.E35E705F:18EF1 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.E35E705F:23208 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.E35E705F:5D738 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.E35E705F:B8F54 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.E35E705F:FC13E | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.E4036FBE | AV |
| GT:VB.Dridex.5.E6C864A3 | AV |
| GT:VB.Dridex.5.E70424F2 | AV |
| GT:VB.Dridex.5.E83B73ED | AV |
| GT:VB.Dridex.5.E9343305 | AV |
| GT:VB.Dridex.5.E9D06AF9 | AV |
| GT:VB.Dridex.5.EAFBC89B | AV |
| GT:VB.Dridex.5.EC72C434 | AV |
| GT:VB.Dridex.5.EC9FB87D | AV |
| GT:VB.Dridex.5.EC9FB87D:59A56 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.ECC0660F | AV |
| GT:VB.Dridex.5.EE74A1CE | AV |
| GT:VB.Dridex.5.EE74A1CE:51E67 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EE74A1CE:6D391 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EE74A1CE:AC776 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F | AV |
| GT:VB.Dridex.5.EEC1CD2F:00E3E | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:0CDF5 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:10790 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:138B5 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:16C26 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:21844 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:22550 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:22680 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:24298 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:24C31 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:27EEE | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:2931A | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:2BFB9 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:3A5C2 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:3D185 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:43FDE | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:4482A | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:46C1E | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:4A52F | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:4ACCB | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:4EB3B | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:70D6A | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:7E1D9 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:7FF4A | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:8766E | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:A0C75 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:AB57D | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:AB697 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:AD14D | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:B1727 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:B46FE | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:B6C5D | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:B960D | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:C4893 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:C94ED | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:CDBA9 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:D362B | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:D9C69 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:D9DBF | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:DA773 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:E1D0C | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:E3EE3 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:F6A66 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.EEC1CD2F:FF983 | ATP Sandbox Adv. Heuristics |
| GT:VB.Dridex.5.F0200EE1 | AV |
| GT:VB.Dridex.5.F154E600 | AV |
| GT:VB.Dridex.5.F652E6D8 | AV |
| GT:VB.Dridex.5.FA04D66B | AV |
| GT:VB.Dridex.5.FB2BC5A8 | AV |
| GT:VB.Dridex.5.FC42BE13 | AV |
| GT:VB.Dridex.5.FEE03C61 | AV |
| GT:VB.Dridex.7.0A15215D | AV |
| GT:VB.Dridex.7.5B917B86 | AV |
| GT:VB.Dridex.7.5DBDA9DD | AV |
| GT:VB.Dridex.7.770CC8D4 | AV |
| GT:VB.Dridex.7.9335641E | AV |
| GT:VB.Dridex.7.9B1E4B05 | AV |
| GT:VB.Dridex.7.AE5042AC | AV |
| GT:VB.Dridex.7.BBC9A366 | AV |
| GT:VB.Dridex.7.C11E13F5 | AV |
| GT:VB.Dridex.7.ED323D19 | AV |
| GT:VB.Heur2.Dridex.4.004D1656 | AV |
| GT:VB.Heur2.Dridex.4.0150BB52 | AV |
| GT:VB.Heur2.Dridex.4.0200F5A1 | AV |
| GT:VB.Heur2.Dridex.4.060C4F8E | AV |
| GT:VB.Heur2.Dridex.4.08C6C316 | AV |
| GT:VB.Heur2.Dridex.4.0A302BAA | AV |
| GT:VB.Heur2.Dridex.4.0B1CCC6B | AV |
| GT:VB.Heur2.Dridex.4.313FFC98 | AV |
| GT:VB.Heur2.Dridex.4.360202C4 | AV |
| GT:VB.Heur2.Dridex.4.383CC20B | AV |
| GT:VB.Heur2.Dridex.4.3B115AEB | AV |
| GT:VB.Heur2.Dridex.4.3E097447 | AV |
| GT:VB.Heur2.Dridex.4.4C9613E9 | AV |
| GT:VB.Heur2.Dridex.4.56DAA493 | AV |
| GT:VB.Heur2.Dridex.4.572DEAED | AV |
| GT:VB.Heur2.Dridex.4.59D9DF6C | AV |
| GT:VB.Heur2.Dridex.4.6B6946F6 | AV |
| GT:VB.Heur2.Dridex.4.6DA06840 | AV |
| GT:VB.Heur2.Dridex.4.7495D490 | AV |
| GT:VB.Heur2.Dridex.4.7495D490:4F4E5 | ATP Sandbox Adv. Heuristics |
| GT:VB.Heur2.Dridex.4.82CFF517 | AV |
| GT:VB.Heur2.Dridex.4.8D822A6C | AV |
| GT:VB.Heur2.Dridex.4.8FC3710E | AV |
| GT:VB.Heur2.Dridex.4.93A57678 | AV |
| GT:VB.Heur2.Dridex.4.93A70A78 | AV |
| GT:VB.Heur2.Dridex.4.94348579 | AV |
| GT:VB.Heur2.Dridex.4.95C4C124 | AV |
| GT:VB.Heur2.Dridex.4.A432016B | AV |
| GT:VB.Heur2.Dridex.4.B6D59A28 | AV |
| GT:VB.Heur2.Dridex.4.B7D1F792 | AV |
| GT:VB.Heur2.Dridex.4.BA66A901 | AV |
| GT:VB.Heur2.Dridex.4.D0C751EC | AV |
| GT:VB.Heur2.Dridex.4.DCAD876C | AV |
| GT:VB.Heur2.Dridex.4.DD0BFC5C | AV |
| GT:VB.Heur2.Dridex.4.DDD6E863 | AV |
| GT:VB.Heur2.Dridex.4.E673575D | AV |
| GT:VB.Heur2.Dridex.4.EE96F915 | AV |
| GT:VB.Heur2.Dridex.4.F11FBCB3 | AV |
| GT:VB.Heur2.Dridex.4.F34FE344 | AV |
| GT:VB.Heur2.Dridex.4.FBE928CE | AV |
| GT:VB.Heur2.Dridex.4.FBE928CE:DBEBF | ATP Sandbox Adv. Heuristics |
| GT:VB.Heur2.Dridex.4.FE45C54E | AV |
| GT:VB.Heur2.Dridex.4.FFB55140 | AV |
| GT:VB.Macros.Heur2.Dridex.2.286C4B13 | AV |
| GT:VB.Macros.Heur2.Dridex.2.28B1EAA6 | AV |
| GT:VB.Macros.Heur2.Dridex.2.5FC2AD91 | AV |
| GT:VB.Macros.Heur2.Dridex.2.5FC2AD91:3CEBB | ATP Sandbox Adv. Heuristics |
| GT:VB.Macros.Heur2.Dridex.2.60229261 | AV |
| GT:VB.Macros.Heur2.Dridex.2.60229261:293C4 | ATP Sandbox Adv. Heuristics |
| GT:VB.Macros.Heur2.Dridex.2.60229261:5A33E | ATP Sandbox Adv. Heuristics |
| GT:VB.Macros.Heur2.Dridex.2.60229261:611A2 | ATP Sandbox Adv. Heuristics |
| GT:VB.Macros.Heur2.Dridex.2.7C856BC6 | AV |
| GT:VB.Macros.Heur2.Dridex.2.7C856BC6:7FABA | ATP Sandbox Adv. Heuristics |
| GT:VB.Macros.Heur2.Dridex.2.7CFF9C92 | AV |
| GT:VB.Macros.Heur2.Dridex.2.7CFF9C92:9C109 | ATP Sandbox Adv. Heuristics |
| GT:VB.Macros.Heur2.Dridex.2.8AC71602 | AV |
| GT:VB.Macros.Heur2.Dridex.2.E075ABA3 | AV |
| GT:VB.Macros.Heur2.Dridex.2.E075ABA3:0C6C9 | ATP Sandbox Adv. Heuristics |
| GT:VB.Macros.Heur2.Dridex.2.EBE0A72E | AV |
| Script-JS.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Script-Macro.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Script-Macro.Trojan.Dridex | ATP Sandbox Adv. Heuristics |
| Script-WScript.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Script-WScript.Trojan.Dridex | ATP Sandbox Adv. Heuristics |
| Trojan.Dridex.AB | AV |
| Trojan.Dridex.L | AV |
| VBA.Heur2.Dridex.2.7CFF9C92.Gen | AV |
| VBA.Heur2.Dridex.2.DED7ADAE.Gen | AV |
| VBA.Heur2.Dridex.2.E1246782.Gen | AV |
| VBA.Heur2.Dridex.4.0200F5A1.Gen | AV |
| VBA.Heur2.Dridex.4.060C4F8E.Gen | AV |
| VBA.Heur2.Dridex.4.0E1C9304.Gen | AV |
| VBA.Heur2.Dridex.4.0FF988BA.Gen | AV |
| VBA.Heur2.Dridex.4.150C4F6B.Gen | AV |
| VBA.Heur2.Dridex.4.16A81170.Gen | AV |
| VBA.Heur2.Dridex.4.1F66EA2E.Gen | AV |
| VBA.Heur2.Dridex.4.233BEDFF.Gen | AV |
| VBA.Heur2.Dridex.4.360202C4.Gen | AV |
| VBA.Heur2.Dridex.4.36CE9DEC.Gen | AV |
| VBA.Heur2.Dridex.4.383CC20B.Gen | AV |
| VBA.Heur2.Dridex.4.3E097447.Gen | AV |
| VBA.Heur2.Dridex.4.40BACFFD.Gen | AV |
| VBA.Heur2.Dridex.4.4353CD0C.Gen | AV |
| VBA.Heur2.Dridex.4.50C8B739.Gen | AV |
| VBA.Heur2.Dridex.4.572DEAED.Gen | AV |
| VBA.Heur2.Dridex.4.591ECEF4.Gen | AV |
| VBA.Heur2.Dridex.4.619D5BC1.Gen | AV |
| VBA.Heur2.Dridex.4.65036224.Gen | AV |
| VBA.Heur2.Dridex.4.666A15E9.Gen | AV |
| VBA.Heur2.Dridex.4.67442045.Gen | AV |
| VBA.Heur2.Dridex.4.6DA06840.Gen | AV |
| VBA.Heur2.Dridex.4.7F409681.Gen | AV |
| VBA.Heur2.Dridex.4.8D822A6C.Gen | AV |
| VBA.Heur2.Dridex.4.93A57678.Gen | AV |
| VBA.Heur2.Dridex.4.94348579.Gen | AV |
| VBA.Heur2.Dridex.4.95C4C124.Gen | AV |
| VBA.Heur2.Dridex.4.A0C6558D.Gen | AV |
| VBA.Heur2.Dridex.4.AF625415.Gen | AV |
| VBA.Heur2.Dridex.4.AFF07D34.Gen | AV |
| VBA.Heur2.Dridex.4.B520F08E.Gen | AV |
| VBA.Heur2.Dridex.4.B6D59A28.Gen | AV |
| VBA.Heur2.Dridex.4.B7D1F792.Gen | AV |
| VBA.Heur2.Dridex.4.BE283C42.Gen | AV |
| VBA.Heur2.Dridex.4.CE654366.Gen | AV |
| VBA.Heur2.Dridex.4.DACC84B5.Gen | AV |
| VBA.Heur2.Dridex.4.DDD6E863.Gen | AV |
| VBA.Heur2.Dridex.4.E2E58C1C.Gen | AV |
| VBA.Heur2.Dridex.4.E4DA9DF5.Gen | AV |
| VBA.Heur2.Dridex.4.EE81CE43.Gen | AV |
| VBA.Heur2.Dridex.4.F34FE344.Gen | AV |
| VBA.Heur2.Dridex.4.F55C2AE6.Gen | AV |
| VBA.Heur2.Dridex.4.F9CC66DA.Gen | AV |
| VBA.Heur2.Dridex.4.FA4396EE.Gen | AV |
| VBA.Heur2.Dridex.4.FBD86DDF.Gen | AV |
| VBA.Heur2.Dridex.5.0073475F.Gen | AV |
| VBA.Heur2.Dridex.5.02AD00F7.Gen | AV |
| VBA.Heur2.Dridex.5.053D5832.Gen | AV |
| VBA.Heur2.Dridex.5.062D0011.Gen | AV |
| VBA.Heur2.Dridex.5.17628F44.Gen | AV |
| VBA.Heur2.Dridex.5.188B7513.Gen | AV |
| VBA.Heur2.Dridex.5.1A42A706.Gen | AV |
| VBA.Heur2.Dridex.5.1FC512E7.Gen | AV |
| VBA.Heur2.Dridex.5.23B96864.Gen | AV |
| VBA.Heur2.Dridex.5.2470662C.Gen | AV |
| VBA.Heur2.Dridex.5.2557CA8D.Gen | AV |
| VBA.Heur2.Dridex.5.26586DDD.Gen | AV |
| VBA.Heur2.Dridex.5.2716EDC7.Gen | AV |
| VBA.Heur2.Dridex.5.271E239F.Gen | AV |
| VBA.Heur2.Dridex.5.28D38440.Gen | AV |
| VBA.Heur2.Dridex.5.2D98A06F.Gen | AV |
| VBA.Heur2.Dridex.5.32D14839.Gen | AV |
| VBA.Heur2.Dridex.5.32FA1B12.Gen | AV |
| VBA.Heur2.Dridex.5.440EA819.Gen | AV |
| VBA.Heur2.Dridex.5.4F48278B.Gen | AV |
| VBA.Heur2.Dridex.5.507F1575.Gen | AV |
| VBA.Heur2.Dridex.5.52BA9675.Gen | AV |
| VBA.Heur2.Dridex.5.555FC9E4.Gen | AV |
| VBA.Heur2.Dridex.5.5CFC3153.Gen | AV |
| VBA.Heur2.Dridex.5.600FA94B.Gen | AV |
| VBA.Heur2.Dridex.5.63B920EE.Gen | AV |
| VBA.Heur2.Dridex.5.66C85BF0.Gen | AV |
| VBA.Heur2.Dridex.5.6A216DA4.Gen | AV |
| VBA.Heur2.Dridex.5.6AEC69D9.Gen | AV |
| VBA.Heur2.Dridex.5.7E50A0B1.Gen | AV |
| VBA.Heur2.Dridex.5.82529CDB.Gen | AV |
| VBA.Heur2.Dridex.5.8266CD36.Gen | AV |
| VBA.Heur2.Dridex.5.830A6419.Gen | AV |
| VBA.Heur2.Dridex.5.83567794.Gen | AV |
| VBA.Heur2.Dridex.5.84575621.Gen | AV |
| VBA.Heur2.Dridex.5.8684BA56.Gen | AV |
| VBA.Heur2.Dridex.5.8F0650EC.Gen | AV |
| VBA.Heur2.Dridex.5.8F1EC6F4.Gen | AV |
| VBA.Heur2.Dridex.5.90BA3A5E.Gen | AV |
| VBA.Heur2.Dridex.5.914DB25A.Gen | AV |
| VBA.Heur2.Dridex.5.937E81C3.Gen | AV |
| VBA.Heur2.Dridex.5.9476CC72.Gen | AV |
| VBA.Heur2.Dridex.5.95EE32C7.Gen | AV |
| VBA.Heur2.Dridex.5.9E9B49AF.Gen | AV |
| VBA.Heur2.Dridex.5.A149446E.Gen | AV |
| VBA.Heur2.Dridex.5.A1DD49A8.Gen | AV |
| VBA.Heur2.Dridex.5.A41BFA50.Gen | AV |
| VBA.Heur2.Dridex.5.A91937AA.Gen | AV |
| VBA.Heur2.Dridex.5.B31B77B4.Gen | AV |
| VBA.Heur2.Dridex.5.B99B331B.Gen | AV |
| VBA.Heur2.Dridex.5.BEA46348.Gen | AV |
| VBA.Heur2.Dridex.5.C023ED87.Gen | AV |
| VBA.Heur2.Dridex.5.C204A927.Gen | AV |
| VBA.Heur2.Dridex.5.C436F699.Gen | AV |
| VBA.Heur2.Dridex.5.C7EFB29A.Gen | AV |
| VBA.Heur2.Dridex.5.CBFCC1FC.Gen | AV |
| VBA.Heur2.Dridex.5.CC37D21A.Gen | AV |
| VBA.Heur2.Dridex.5.D0661662.Gen | AV |
| VBA.Heur2.Dridex.5.D1EE7870.Gen | AV |
| VBA.Heur2.Dridex.5.D224EC08.Gen | AV |
| VBA.Heur2.Dridex.5.D8CB6576.Gen | AV |
| VBA.Heur2.Dridex.5.D91F3ECA.Gen | AV |
| VBA.Heur2.Dridex.5.DFE6ABD3.Gen | AV |
| VBA.Heur2.Dridex.5.E9D06AF9.Gen | AV |
| VBA.Heur2.Dridex.5.ED12BD63.Gen | AV |
| VBA.Heur2.Dridex.5.EE093FF2.Gen | AV |
| VBA.Heur2.Dridex.5.F0200EE1.Gen | AV |
| VBA.Heur2.Dridex.5.FDD23238.Gen | AV |
| Win32.Backdoor.Dridex | ATP Sandbox Adv. Heuristics |
| Win32.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Win32.Trojan.Dridex | ATP Sandbox Adv. Heuristics |
| Win64.Infostealer.Dridex | ATP Sandbox Adv. Heuristics |
| Win64.Trojan.Dridex | ATP Sandbox Adv. Heuristics |
Related IPS Signatures
| Signature Name | Engine |
|---|---|
| MALWARE-OTHER Win.Trojan.Dridex malicious executable download attempt | IPS-SWG |
Related blogs
Netskope Threat Labs Stats for October 2023
·5 min read
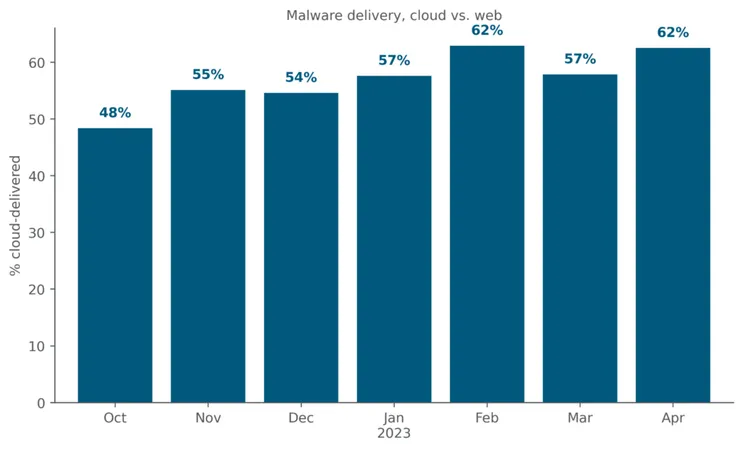
Netskope Threat Labs Stats for April 2023
·5 min read