Description
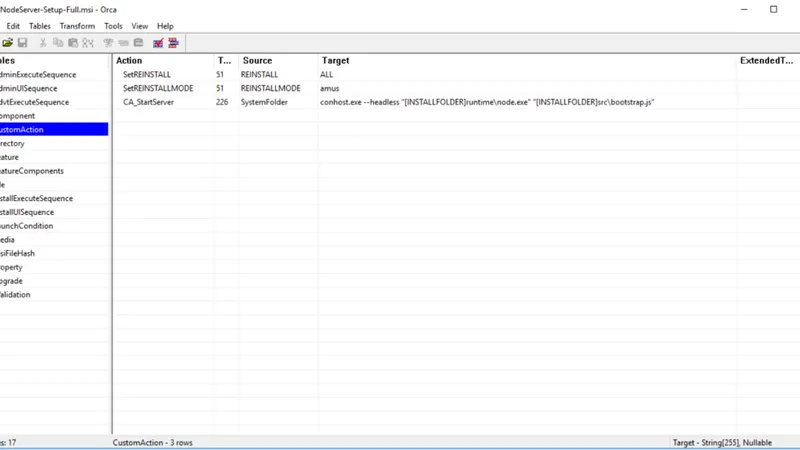
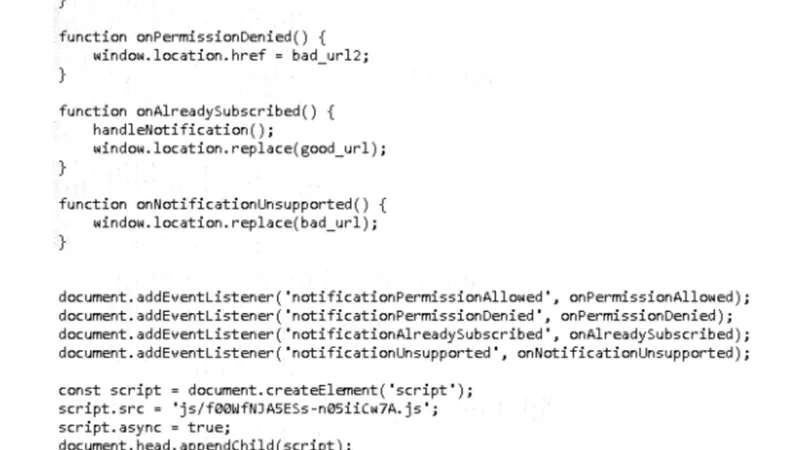
LegionLoader, also tracked as Satacom, CurlyGate, and RobotDropper, is a loader that cyberattackers distribute through malicious advertising, search engine poisoning, and fake CAPTCHA pages. It runs obfuscated scripts to install malicious browser extensions that steal cryptocurrency, and it can download follow-on payloads such as information stealers and remote access trojans. Detections under this name indicate a loader infection, so responders should hunt for malicious browser extension persistence and credential theft.
Stats
- First seen
- July 2022
- Last seen
- November 2026
Also known as
CurlygateSatacom
Alert name variants
| Alert Name |
|---|
| Win32.Downloader.Satacom |
| Win32.Trojan.Satacom |
| Win64.Trojan.Curlygate |
Related IPS Signatures
| Signature Name |
|---|
| MALWARE-CNC Win.CURLYGATE C2 outbound traffic detected |