Description
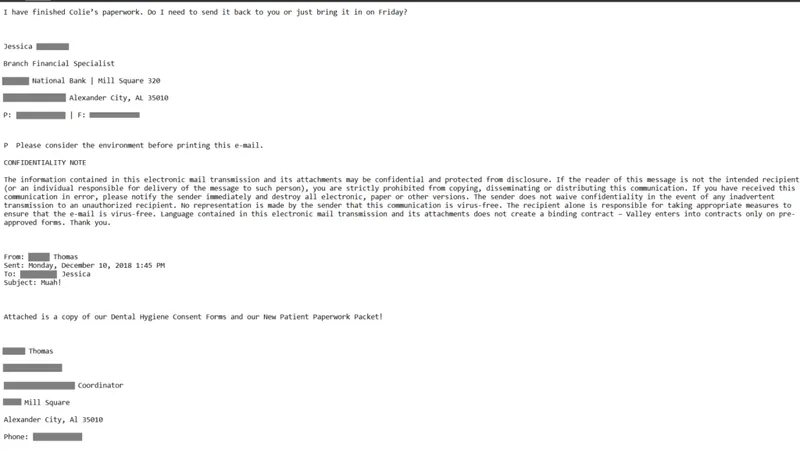
Lokibot (a.k.a. Loki) is an information stealer and keylogger that targets credentials stored in browsers, email clients, FTP programs, and other applications, with variants that also run on Android. Sold cheaply and rebranded many times, it became one of the most widely distributed commodity stealers of its era. Its campaigns rely on phishing, cracked software, and loaders, and stolen data flows to panels that operators use or resell.
Stats
- First seen
- March 2022
- Last seen
- October 2026
Also known as
LokiBot
MITRE ATT&CK techniques
28 techniques across 10 tactics.
TA0002 Execution
TA0004 Privilege Escalation
TA0005 Stealth
- T1027Obfuscated Files or Information
- T1027.002Software Packing
- T1027Obfuscated Files or Information
- T1027.002Software Packing
- T1055Process Injection
- T1055.012Process Hollowing
- T1070Indicator Removal
- T1070.004File Deletion
- T1140Deobfuscate/Decode Files or Information
- T1497Virtualization/Sandbox Evasion
- T1497.003Time Based Checks
- T1564Hide Artifacts
- T1564.001Hidden Files and Directories
- T1620Reflective Code Loading
TA0007 Discovery
TA0011 Command and Control
TA0010 Exfiltration
- T1041Exfiltration Over C2 Channel
TA0112 Defense Impairment
- T1112Modify Registry
Associated groups
Alert name variants
| Alert Name |
|---|
| Android.Ransomware.LokiBot |
| ByteCode-MSIL.Infostealer.LokiBot |
| ByteCode-MSIL.Trojan.LokiBot |
| Document-Office.Downloader.Lokibot |
| Document-Word.Downloader.Lokibot |
| Email-MIME.Trojan.LokiBot |
| Email-MSG.Infostealer.LokiBot |
| Script-AutoIt.Infostealer.LokiBot |
| Script-WScript.Trojan.LokiBot |
| Win32.Infostealer.LokiBot |