Description
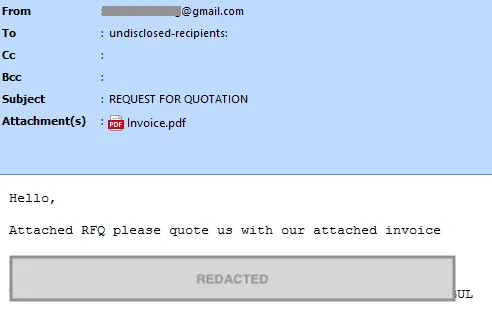
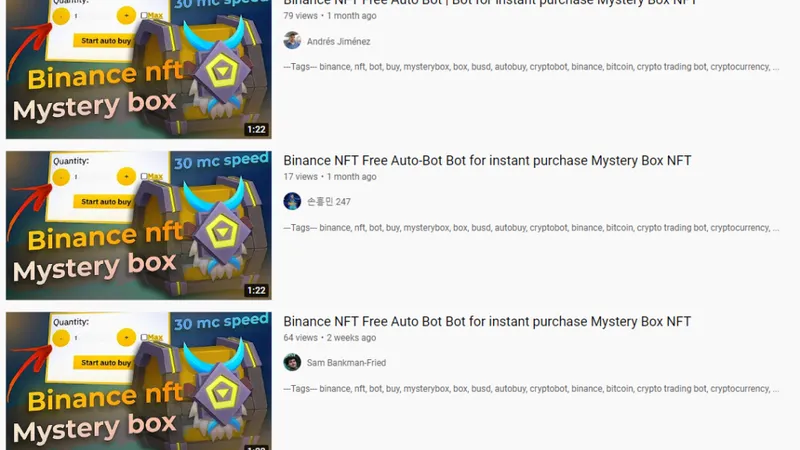
RedLine Stealer is an information stealer first identified in 2020 and sold on underground forums as malware as a service, either as a standalone purchase or a subscription. It harvests saved browser credentials, autocomplete data, and credit card information, it takes a system inventory that includes installed security software, and it can upload and download files and execute commands on infected machines. Stolen data from the family has been resold on the deep and dark web to initial access brokers for further intrusions.
Stats
- First seen
- March 2022
- Last seen
- October 2026
Also known as
RedLineRedLineStealerRedlineRedlineStealerRedlinestealer
MITRE ATT&CK techniques
35 techniques across 9 tactics.
TA0002 Execution
TA0005 Stealth
TA0006 Credential Access
TA0007 Discovery
- T1012Query Registry
- T1016System Network Configuration Discovery
- T1033System Owner/User Discovery
- T1082System Information Discovery
- T1087Account Discovery
- T1087.001Local Account
- T1217Browser Information Discovery
- T1518Software Discovery
- T1518.001Security Software Discovery
- T1518Software Discovery
- T1518.001Security Software Discovery
- T1614System Location Discovery
- T1614.001System Language Discovery
TA0011 Command and Control
TA0010 Exfiltration
- T1041Exfiltration Over C2 Channel
TA0040 Impact
- T1657Financial Theft
Alert name variants
| Alert Name |
|---|
| Binary.Trojan.RedLine |
| ByteCode-MSIL.Infostealer.RedLine |
| ByteCode-MSIL.Ransomware.RedLine |
| ByteCode-MSIL.Spyware.Redline |
| ByteCode-MSIL.Spyware.RedLine |
| ByteCode-MSIL.Spyware.Redlinestealer |
| ByteCode-MSIL.Trojan.Redline |
| ByteCode-MSIL.Trojan.RedLine |
| ByteCode-MSIL.Trojan.Redlinestealer |
| ByteCode-MSIL.Trojan.RedlineStealer |
Related IPS Signatures
Related blogs