Description
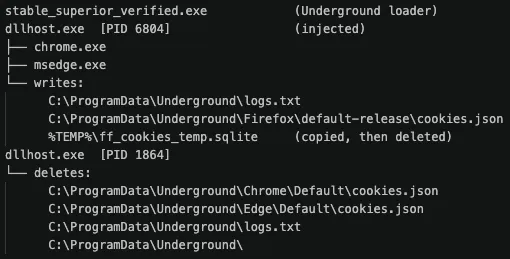
Rhadamanthys is a modular information stealer sold as a subscription service that targets credentials, browser data, and cryptocurrency wallets on infected systems. Its implementation includes advanced evasion features, and its operators ship regular updates that add capabilities such as clipboard hijacking and screenshot capture. Distributors reach victims through malvertising, search engine poisoning, and fake software downloads, and stolen data feeds established criminal marketplaces.
Stats
- First seen
- January 2023
- Last seen
- October 2026
Also known as
RhadamanthysStealer
Alert name variants
| Alert Name |
|---|
| ByteCode-MSIL.Spyware.Rhadamanthys |
| ByteCode-MSIL.Trojan.Rhadamanthys |
| Document-PDF.Trojan.Rhadamanthys |
| Script-BAT.Spyware.Rhadamanthys |
| Script-JS.Trojan.Rhadamanthys |
| Script-PowerShell.Spyware.Rhadamanthys |
| Script-PowerShell.Trojan.Rhadamanthys |
| Script-WScript.Spyware.Rhadamanthys |
| Win32.Downloader.Rhadamanthys |
| Win32.Exploit.Rhadamanthys |