This report covers organizations in the manufacturing sector. The sample is broad, spanning automotive, chemicals, consumer goods, food and beverage, aerospace and defense, and heavy industrial engineering, with a long tail of smaller specialized sub-sectors.
That breadth matters because manufacturing turns cyber incidents into physical and commercial ones. Plant operations and corporate IT are increasingly interconnected, so an intrusion can halt a production line and expose decades of process intellectual property, with consequences that go well beyond data loss. The sector is a standing target for state-sponsored industrial espionage seeking designs and process know-how, and its deep, just-in-time supply chains let a single compromise propagate across tiers of suppliers and customers, and manufacturing breaches increasingly involve third parties and web applications.
At the same time, manufacturers are modernizing quickly (cloud, SaaS, IIoT, and now AI), and that digital transformation is outpacing governance. Many plants still run legacy OT that is long-lived and often unpatchable, while labor shortages push aggressive AI and agentic adoption. Regulators are responding: EU NIS2 brings many manufacturers into scope, and the US CMMC program extended cybersecurity requirements to the defense industrial base.
This report is based on real-world, anonymized telemetry from the Netskope One platform, not from surveys or self-reported data. It highlights trends and emerging risks in the manufacturing sector so that organizations can anticipate attack vectors and make more informed strategic decisions.
Key findings
AI systems, tools, and applications are now embedded across manufacturing organizations. More organizations are deploying managed AI applications, AI is taking a larger role in everyday applications and agentic workflows, and these shifts are bringing new security, data, and malware risks.
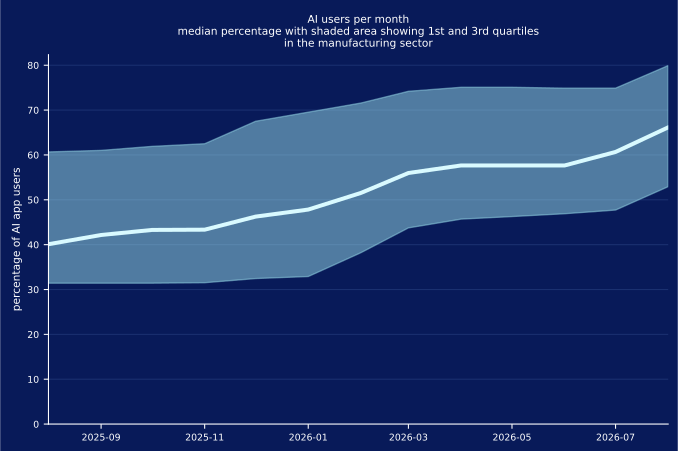
AI use continues to grow: Over the past year, active AI users rose from 40% to 67% of total users in manufacturing. Microsoft Copilot now ranks as the most widely adopted AI application in the sector, which sets manufacturing apart from other industries. Organization-managed AI application use rose from 35% to 70%, while personal AI account use fell from 75% to 55%. But AI activity within organizations isn’t limited to dedicated tools or direct usage: 96% of employees use applications with embedded AI features, and 90% interact with systems that specifically use customer or user data for training, which compliance teams need to account for.
Sensitive data travels through AI workflows: Regulated data accounts for 57% of AI-related data policy violations in manufacturing, followed by passwords and keys at 19%, intellectual property at 16%, and source code at 9%. Remote Model Context Protocol (MCP) activity grew sharply over the period: the number of non-human entities connecting to remote MCP servers rose by 490%, and MCP events rose by 600%. Organizations need to understand not only which AI applications and agents operate in their environments, but also the users and systems they interact with, and what they can access.
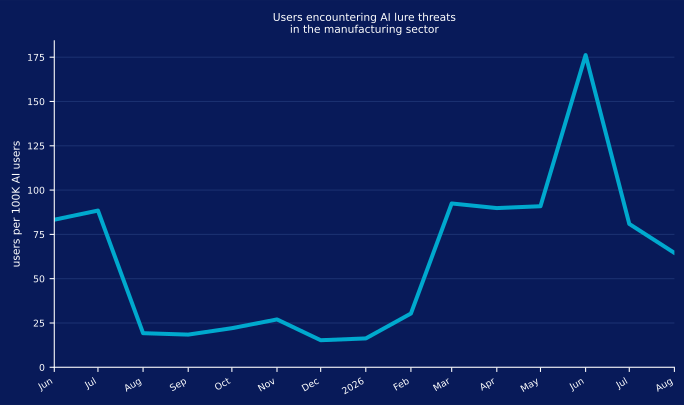
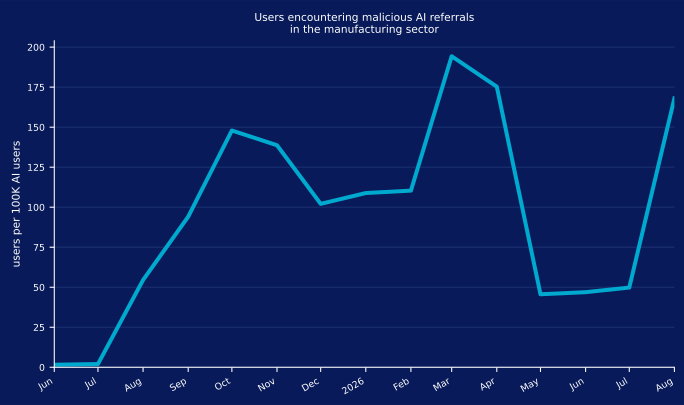
Attackers are capitalizing on the AI trend: AI lures consistently target corporate users, with activity spiking in February and rising further in June 2026. Malicious AI link interactions followed a similar pattern, emerging in waves starting in July 2025 and rising further in early 2026.
AI use
AI: Adoption and usage trends
As manufacturers become more comfortable adopting AI, the technology is playing a larger role in everyday business operations. Over the past year, the share of users actively using AI applications in the manufacturing sector rose from 40% to 67%, reflecting continued AI adoption across the industry and aligning with broader global trends.
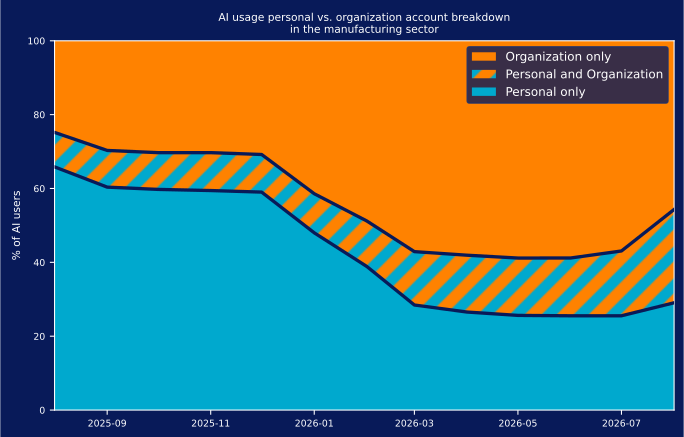
Meanwhile, manufacturers have steadily reduced shadow AI risk by guiding users away from personal AI accounts and toward organization-managed tools. Over the past year, the use of personal AI applications fell from 75% to 55%, while adoption of organization-managed AI solutions rose from 35% to 70%. At the same time, the share of users switching between personal and enterprise accounts increased from 9% to 25%, suggesting that employees continue to move between managed and personal accounts as they explore new tools. Manufacturers can reduce this switching by speeding up the review and approval of new AI applications while keeping tighter instance-level controls.
Manufacturers are moving users to managed AI, improving data protection and compliance without limiting productivity. Personal AI use remains common, however, and the overlap between personal and enterprise accounts has grown. Shadow AI rarely disappears entirely, so organizations need long-term guardrails, clear policies, and a simple process for requesting new AI tools.
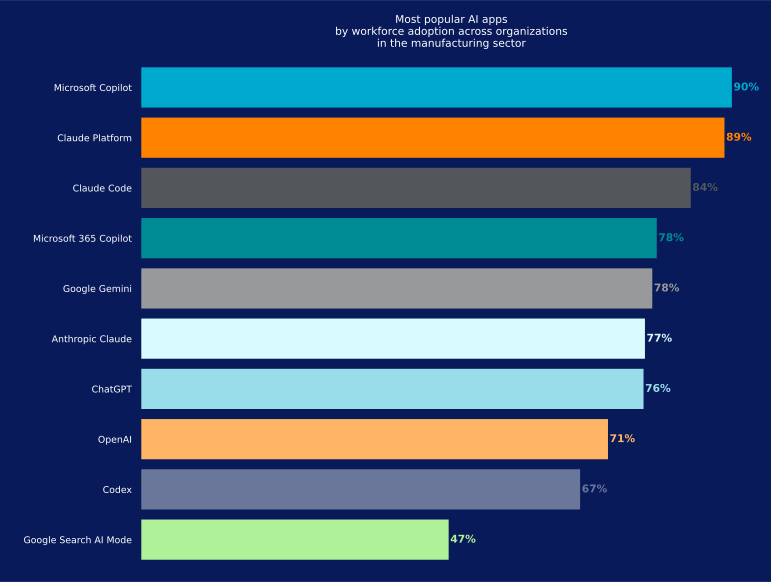
For the first time, Microsoft Copilot ranks as the most widely adopted AI application in the manufacturing sector, used by 90% of organizations. Claude Platform follows closely at 89%, while ChatGPT trails at 76%.
Microsoft Copilot’s move to the top of the list is accompanied by a comparatively low ranking for ChatGPT, whose adoption is now well below that of the two leading applications. The strong showing of both Copilot and Claude Platform also suggests manufacturers are embracing AI across workflows, from tools integrated into everyday business operations to platforms that support software development. For security teams, this means AI traffic no longer comes mainly from standalone chatbots. Much of it now runs inside existing business applications and development environments.
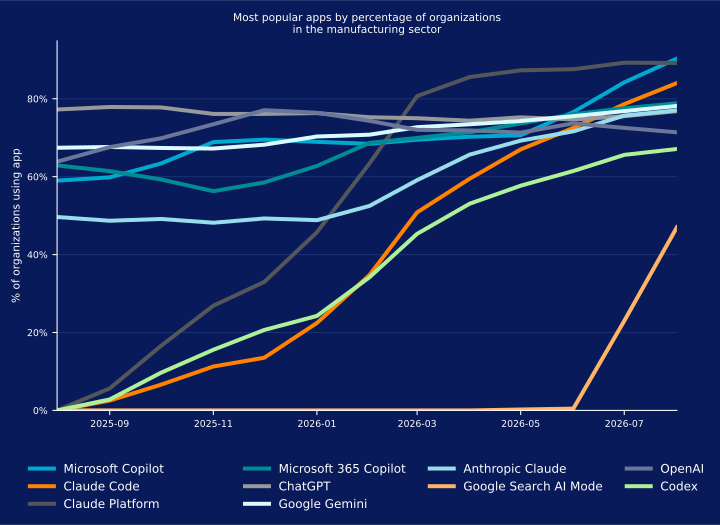
The chart below shows how adoption of the leading AI applications in the manufacturing sector has evolved over the past year, highlighting a rise in Microsoft Copilot adoption beginning in April 2026, while Claude Platform usage has remained steady since February. Google AI Search also began appearing in the data in June, reaching 47% adoption. These trends differ from the global picture, reflecting a distinct pattern of AI application adoption in manufacturing.
AI: App usage and data policy violation
As AI adoption continues to grow in the manufacturing sector, data exposure is becoming a bigger concern. Employees are using AI tools to summarize documents, generate reports, get assistance, and streamline everyday business processes. These activities can involve sensitive customer, business, and operational information, creating new opportunities for data exposure.
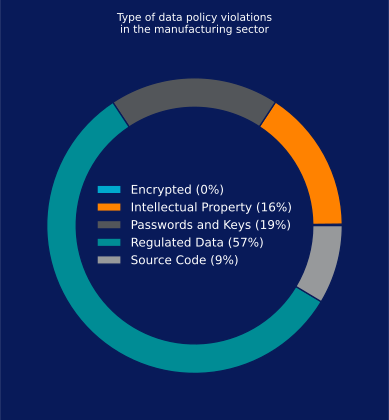
Our analysis shows that regulated data remains the most common type of sensitive information involved in AI-related data policy violations in the manufacturing sector, accounting for 57% of events. Passwords and API keys follow at 19%, intellectual property at 16%, and source code at 9%.
Most blocked AI apps
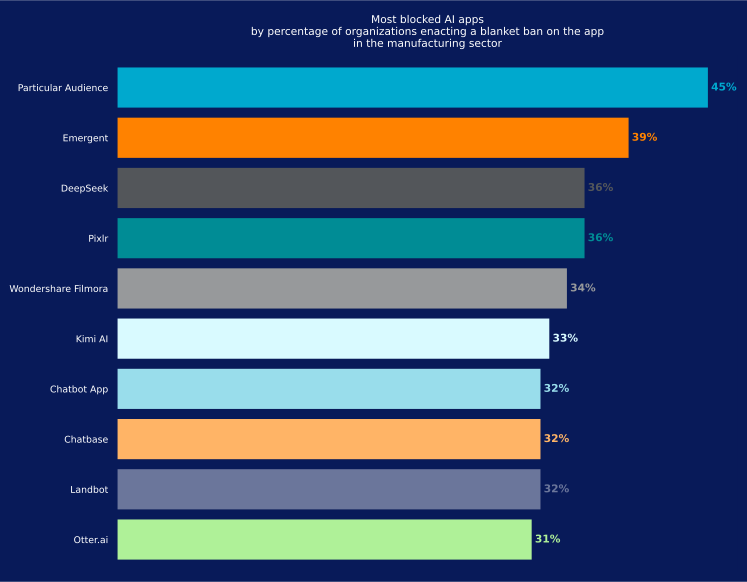
Many manufacturers are restricting specific AI applications because of security, privacy, and compliance concerns. While policies vary by organization, some applications are blocked more often than others, offering insight into where security teams see the greatest risks.
Particular Audience is the most frequently blocked AI application in the manufacturing sector, with 45% of organizations restricting access. Emergent follows at 39%, while DeepSeek is blocked by 36% of organizations.
These restrictions reflect concerns about how AI applications handle sensitive information and connect to business systems; where prompts and uploaded files are stored; which internal resources an app can reach; and whether its processing happens outside established security and compliance controls.
Agentic AI adoption
User adoption of AI
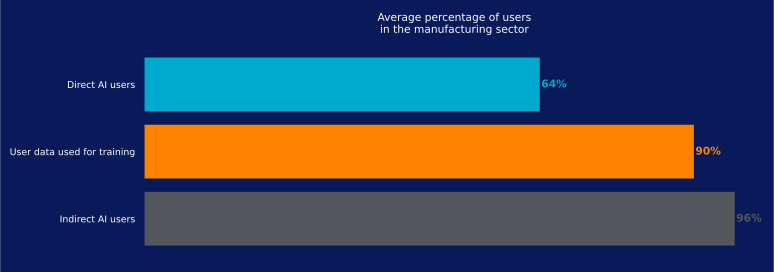
Across the manufacturing sector, 64% of employees use AI applications directly, while 96% use applications that include AI-powered features. In addition, 90% interact with AI systems that use customer or user data to train models, a compliance risk unless properly governed.
Most AI use happens inside applications employees already rely on, not in standalone tools. That makes it harder for manufacturers to track where sensitive information is shared and how it is used, both in direct interactions with AI tools and in AI features running in the background.
MCP: Rapidly increasing interconnectedness
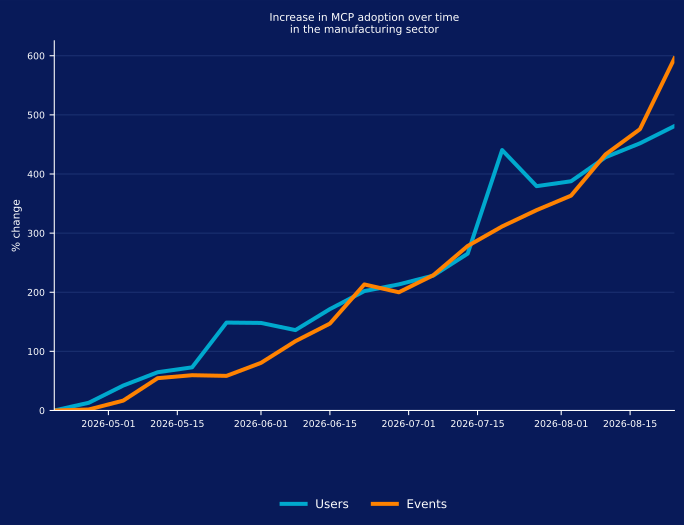
MCP, the open-source standard that lets AI models connect to external and internal data sources and tools, is growing rapidly in the manufacturing sector. Over the research period, the number of non-human entities interacting with remote MCP servers rose 490%, while MCP-related events grew 600%, with a spike in activity in July and August.
Each remote MCP connection gives an AI agent a path to a server outside the organization, and some of those agents can also reach business data or other sensitive resources. Security teams need to know which agents are making these connections and what data they carry.
These figures relate specifically to remote MCP usage, where AI agents connect to MCP servers hosted on the internet rather than locally or within an organization’s own network. The sharp growth, especially the July spike, suggests that agentic AI is becoming more integrated into business workflows.
AI-adjacent threats
Categorizing AI Risks
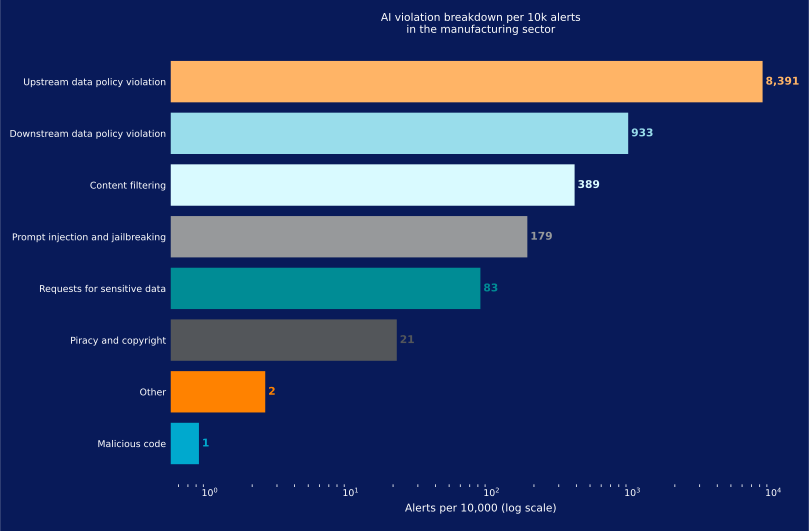
Effective AI visibility, governance, and protection start with a clear understanding of the risks organizations face. In the manufacturing sector, upstream data policy violations account for 83% of AI-related violations, making them the most prevalent risk category. Downstream data policy violations also remain a concern, reflecting the risk of exposing sensitive information both when it is entered into AI tools and when AI-generated content is shared or used elsewhere.
Malicious code-related violations are less common, but when they occur, they can lead directly to compromised systems, applications, and business data.
Malicious AI lures
A malicious AI lure tricks users into downloading malware or visiting a malicious website by posing as a trusted AI brand or tool. In the manufacturing sector, activity showed a quick increase in February from around 25 to around 100 users per 100,000 employees, remained constant until May, and then spiked further to nearly 175 per 100,000 in June.
The pattern suggests that malicious AI lures arrive in waves rather than at a steady rate: two short bursts in February, then a larger rise in June.
Recent campaigns have included fake AI application installers, trojanized developer tools, and other AI-themed lures designed to exploit interest in AI. As adoption expands, attackers will likely keep refining these techniques, including targeting software supply chains and distributing malicious packages that take advantage of AI-assisted development.
Malicious AI links
A malicious AI link is a harmful link returned by an AI application that a user clicks or an AI agent follows. These links are similar to malicious links planted in search engine results, where users may click them believing they lead to legitimate websites. Attackers can promote them through SEO techniques, paid advertisements, or compromised legitimate infrastructure.
The approach is similar in AI environments, though malicious content reaches users through different channels. Techniques such as artificial intelligence engine optimization (AIEO) are emerging as attackers seek to influence the content AI models surface, while advertising is also beginning to appear within AI applications.
In the manufacturing sector, interactions with malicious AI links began to rise in July 2025, reaching 150 per 100,000 users in October. A second increase began in February 2026, with activity climbing further to 200 per 100,000 users in March. Security teams should inspect links returned by AI applications the same way they inspect links in search results and email, before users or agents follow them.
Recommendations
With the growing use of AI tools, both corporate and personal, and the misuse of personal cloud apps, it is essential to strengthen visibility, improve policies, and prioritize proactive defenses to protect your organization in this fast-changing threat landscape.
Based on the trends uncovered in this report, Netskope Threat Labs strongly encourages organizations across the manufacturing sector to take a fresh look at their overall security stance:
- Inspect all HTTP and HTTPS downloads, including all web and cloud traffic, to prevent malware from infiltrating your network. Netskope customers can configure their Netskope One NG-SWG with a threat protection policy that applies to downloads across all categories and all file types.
- Block access to apps that do not serve any legitimate business purpose or pose a disproportionate risk to the organization. A good starting point is a policy to allow reputable apps currently in use while blocking all others.
- Use DLP policies to detect potentially sensitive information, including source code, regulated data, passwords and keys, intellectual property, and encrypted data, being sent to personal app instances, AI apps, or other unauthorized locations.
- Use Remote Browser Isolation (RBI) technology to provide additional protection when visiting websites in categories that may pose a higher risk, such as newly observed or newly registered domains.
- Use Netskope Skylight AI Gateway to gain visibility and control over AI applications and API interactions, helping secure data flows between users, applications, and LLMs.
- Deploy Netskope Skylight AI Guardrails to enforce consistent protections against sensitive data exposure, unsafe prompts, and policy violations across managed and unmanaged AI environments.
- Use Netskope Skylight AI App Security to discover both managed and unmanaged AI applications, apply real-time controls, and enforce governance policies across personal and enterprise AI use.
- Leverage Netskope Skylight AI Analytics to monitor AI adoption trends, user activities, and DLP incidents, facilitating organizations to better understand and reduce AI-related risk exposure.
- Consider Netskope Skylight AI Red Teaming to actively identify vulnerabilities and misconfigurations in private AI deployments before they may be exploited in production environments.
Netskope Threat Labs
Staffed by the industry’s foremost cloud threat and malware researchers, Netskope Threat Labs discovers, analyzes, and designs defenses against the latest cloud threats affecting enterprises. Our researchers are regular presenters and volunteers at top security conferences, including DEF CON, Black Hat, and RSA.
About this report
Netskope provides threat protection to millions of users globally. The information presented in this report is based on aggregate use data collected by the Netskope One platform for a subset of Netskope customers in the manufacturing sector.
The statistics in this report are based on the period from June 1, 2025, through August 31, 2026. Stats reflect attacker tactics, user behavior, and organization policy.